Black Friday Madness- 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: fifty75ct

Network-Security-Essentials Network Security Essentials for Locally-Managed Fireboxes Questions and Answers

Questions 4

You enable a network device monitoring application on a server with IP address 10.0.1.22. After you run the application, it reports that it cannot ping the Firebox at 10.0.1.1, and you see this log message in Traffic Monitor. What is the most likely cause of this issue? (Select one.)

(Log: Deny 10.0.1.22 10.0.1.1 icmp/8 255-Unhandled Internal Packet-00)

Options:

A.

The server IP address is on the Blocked Sites list

B.

There is no route on the Firebox for the 10.0.1.0/24 subnet

C.

The dynamic NAT statement is not configured correctly for the 10.0.1.0/24 subnet

D.

The default Unhandled Internal Packet policy is at the top of the policy set

E.

There is no policy that allows Ping traffic from the server to the Firebox alias

Buy Now
Questions 5

Which WatchGuard tools can you use to review the traffic log messages generated by your Firebox? (Select three.)

Options:

A.

FireWatch

B.

Policy Manager

C.

Traffic Monitor

D.

Dimension

E.

Status Report

F.

WatchGuard Cloud

Buy Now
Questions 6

To accurately detect applications over an HTTPS connection with Application Control, you must enable content inspection in the HTTPS proxy.

Options:

A.

True

B.

False

Buy Now
Questions 7

You configured your Firebox interfaces and routes and want to verify the status of the routes and connected hosts. You found this information in Firebox System Manager > Status Report. What is true about the IPv4 routes and ARP table in this deployment? (Select one.)
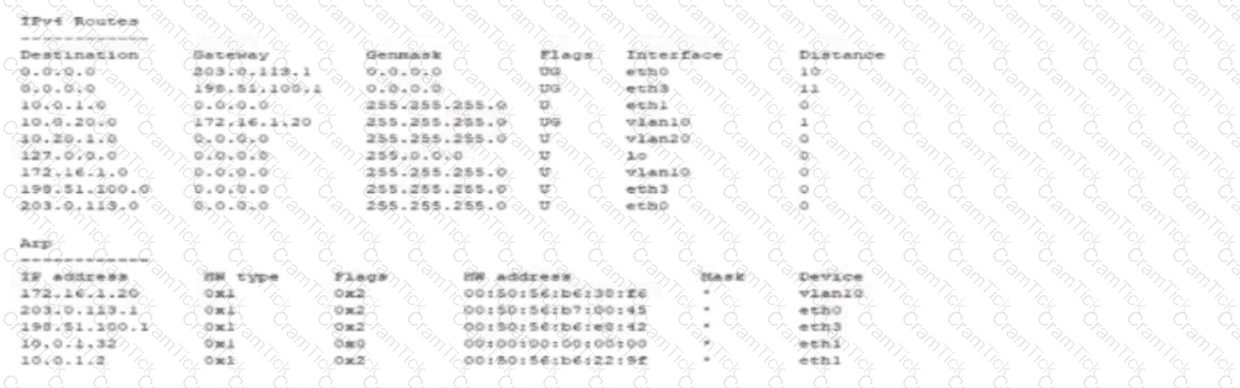
Options:

A.

The Firebox is publicly reachable at 198.51.100.1 through the eth0 interface

B.

10.0.20.53 can be reached through the vlan20 interface

C.

The MAC address for the default gateway that currently routes traffic is 00:50:56:b5:e5:42

D.

The MAC address for 172.16.1.20 is 00:50:56:b0:22:0f

E.

The Firebox cannot resolve a MAC address for 10.0.1.32

Buy Now
Questions 8

The Audit Trail report shows information about Firebox configuration changes. How can you make sure the Audit Trail report includes the names of the specific person that made each change? (Select one.)

Options:

A.

Enable the Logging > AuditTrack feature

B.

Create unique device administrator accounts for each Firebox administrative user

C.

Configure all Firebox administrators to use the Authentication Portal to log in to the Firebox

D.

Install the SSO Client on each computer used by Firebox administrators

E.

Configure your RADIUS server to send accounting messages to the Firebox

Buy Now
Questions 9

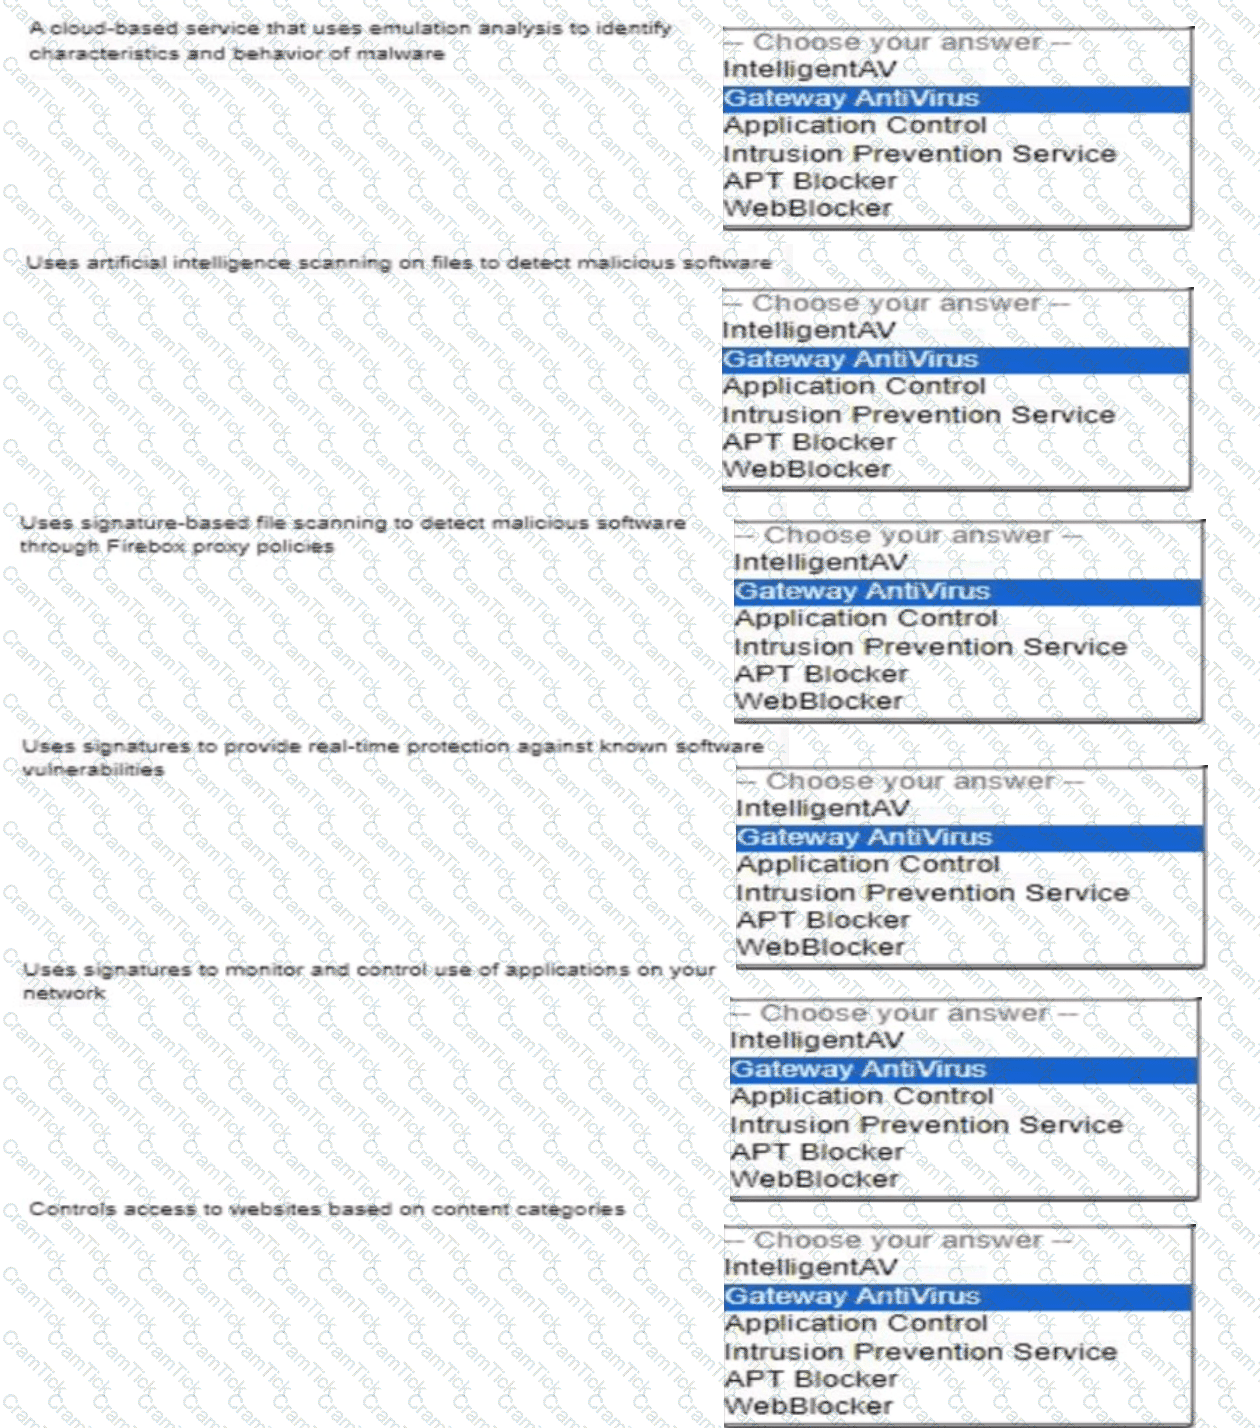
Match each WatchGuard Subscription Service with its function:

Options:

Buy Now
Questions 10

The Firebox can scan the contents of encrypted zip files with Gateway AntiVirus when HTTPS content inspection is enabled.

Options:

A.

True

B.

False

Buy Now
Questions 11

You can run TCP Dump directly from the Firebox.

Options:

A.

True

B.

False

Buy Now
Questions 12

Before packets are examined by Default Threat Protection, they are processed by firewall policies in top-down order.

Options:

A.

True

B.

False

Buy Now
Questions 13

When you configure a Branch Office VPN tunnel to a third-party device, AES-GCM encryption is recommended for:

Options:

A.

Better performance and throughput when supported by both VPN endpoints

B.

Troubleshooting purposes

C.

Better uptime because of additional keep-alive options

D.

Routing over a BOVPN

E.

Connections to third-party firewalls only

Buy Now
Questions 14

Which of these sites are denied by the WebBlocker action shown in this image? (Select three.)
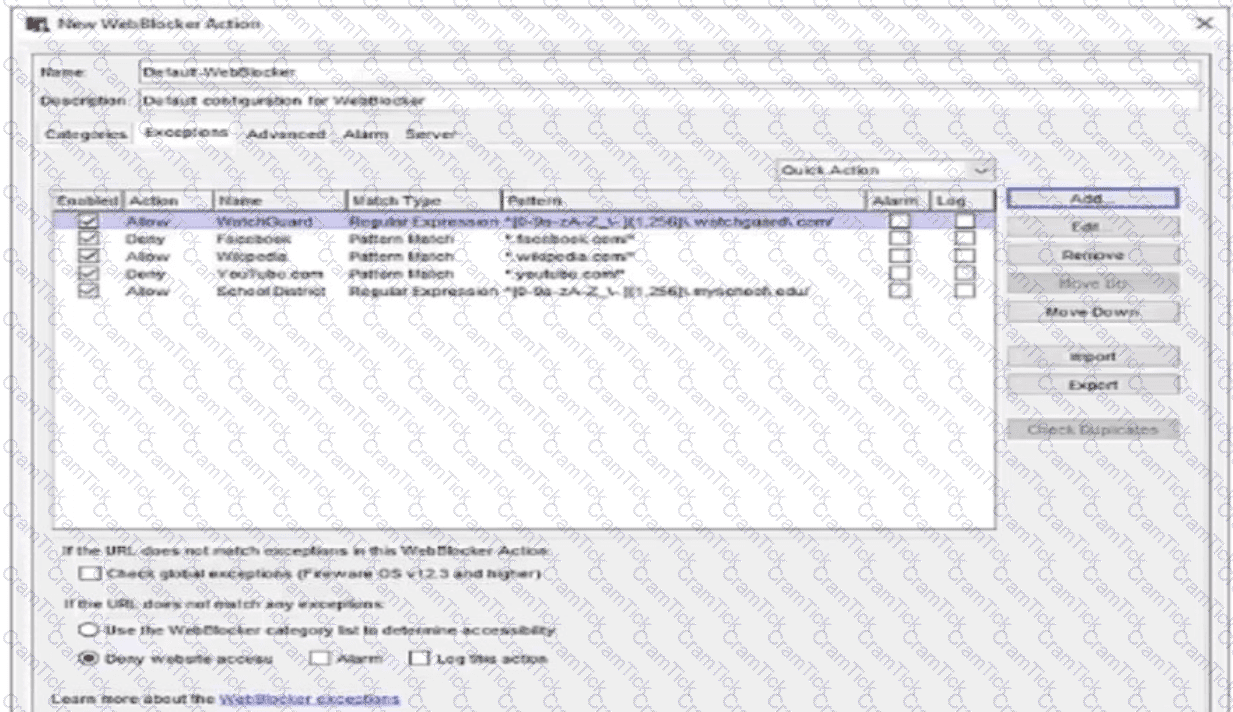
Options:

A.

www.wikipedia.com/firewall

B.

www.youtube.com

C.

www.google.com

D.

schedule.myschool.edu

E.

www.watchguard.com/wgrd-blog

F.

login.facebook.com

Buy Now
Questions 15

You configured email notifications in WatchGuard Cloud for your Firebox Device Alarms and want to receive an email when your users download any .exe files through an HTTP proxy. You must enable what type of log message in the Firebox configuration? (Select one.)

Options:

A.

Allowed traffic logs for the HTTP proxy policy

B.

Alarm logs for the EXE/DLL Body Content rule in the HTTP proxy

C.

Diagnostic logs for Gateway AntiVirus

D.

Alarm logs for when a virus is detected in the HTTP proxy

E.

Denied traffic logs for the HTTP proxy policy

Buy Now
Questions 16

Some management tasks require you to use a specific management interface. Match the task below with the management interface that supports it.
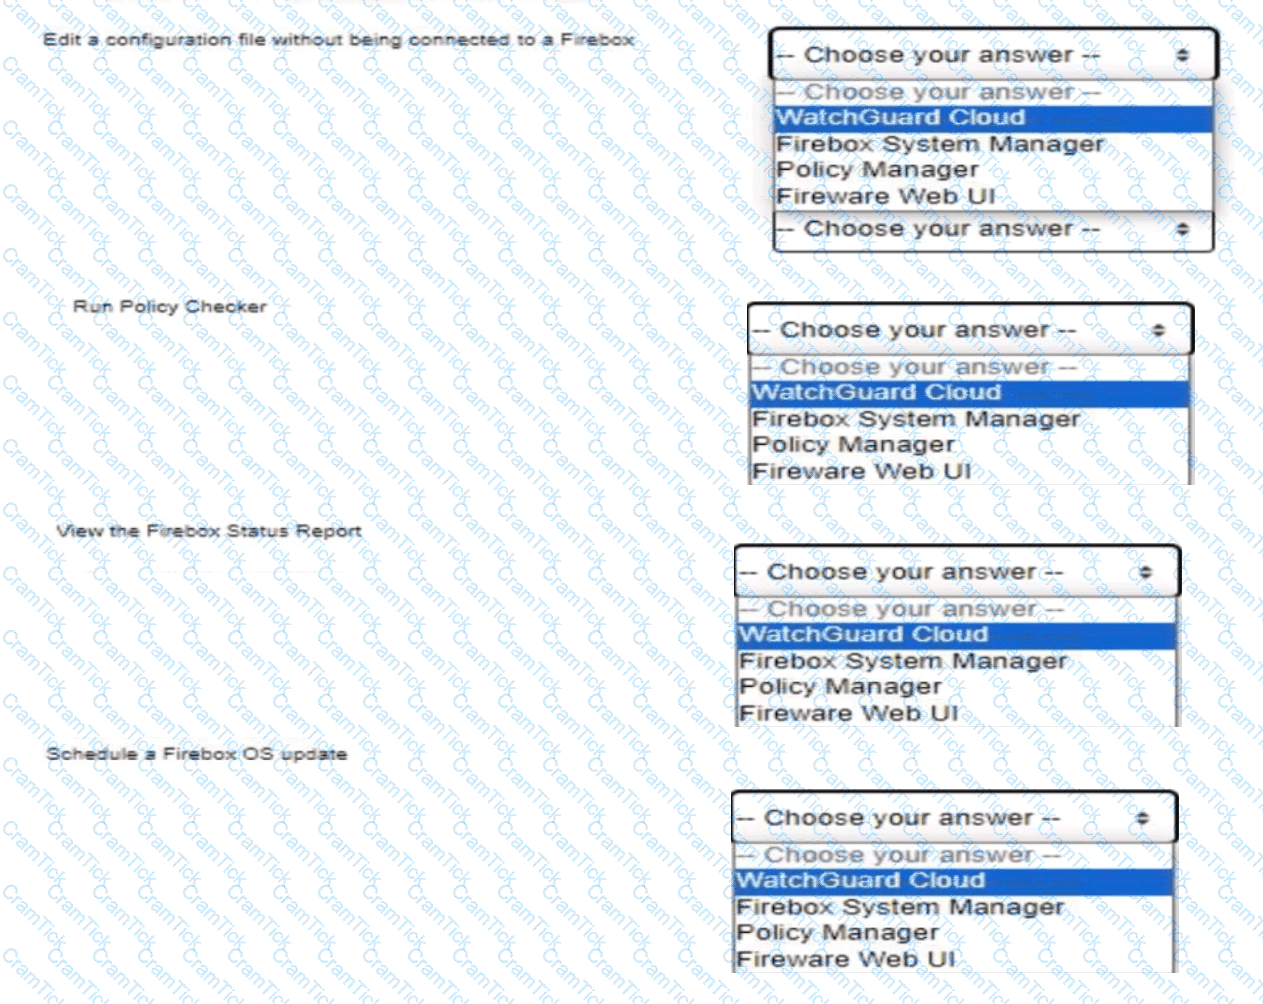
Options:

Buy Now
Questions 17

Which of these options are private IPv4 address spaces described in RFC 1918 Address Allocation for Private Internets? (Select three.)

Options:

A.

192.168.0.0/16

B.

172.16.0.0/12

C.

102.0.2.0/24

D.

172.0.0.0/16

E.

10.0.0.0/8

Buy Now
Questions 18

What steps must you take to send log messages from a Firebox to WatchGuard Cloud? (Select two.)
Options:

A.

Enable WatchGuard Cloud in the Firebox configuration

B.

Add the FQDN of your WatchGuard Cloud account as a Log Server on the Firebox

C.

Define an Authentication Key that all your Fireboxes use to communicate with WatchGuard Cloud

D.

Configure Dimension to synchronize log messages with WatchGuard Cloud

E.

Use the WatchGuard Cloud Add Device wizard to add the Firebox to WatchGuard Cloud

Buy Now
Exam Name: Network Security Essentials for Locally-Managed Fireboxes
Last Update: Nov 19, 2026
Questions: 60
Network-Security-Essentials pdf

Network-Security-Essentials PDF

$22.5  $89.99
Network-Security-Essentials Engine

Network-Security-Essentials Testing Engine

$26.25  $104.99
Network-Security-Essentials PDF + Engine

Network-Security-Essentials PDF + Testing Engine

$35  $139.99