Black Friday Madness- 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: fifty75ct

NSE7_FSN_AR-7.6 Fortinet NSE 7 - Secure Networking 7.6 Architect Questions and Answers

Questions 4

What are two reasons you might see iprope_in check () check failed, drop when using the debug How? (Choose two.)

Options:

A.

The packet was dropped because it is not allowed by any firewall policy.

B.

The packet was dropped because there is no route to the source.

C.

The packet was dropped because the trusted host list is misconfigured

D.

The packet was dropped because the requested service is not enabled on FortiGate

Buy Now
Questions 5

Refer to the exhibit, which shows the partial output of a diagnose command.
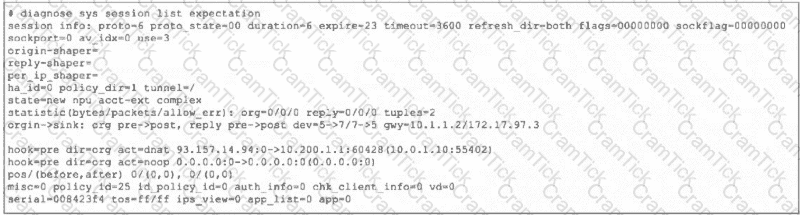
Which two conclusions can you draw from the output shown in the exhibit? (Choose two.)

Options:

A.

FortiGate will drop the expected traffic if it does not arrive within 23 seconds.

B.

Clearing the master session has no impact on the expectation session.

C.

This is a pinhole session to allow traffic for a TCP protocol that dynamically assigns TCP ports.

D.

The session is checked against firewall policy ID 25.

Buy Now
Questions 6

Refer to the exhibit, which shows the output o! the BGP database.
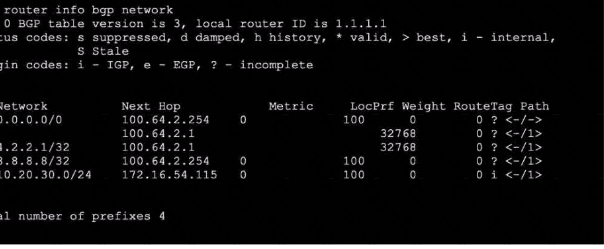
Which two statements are correct? (Choose two.)

Options:

A.

The advertised prefix of 10.20.30.0/24 was configured using the network command.

B.

The first four prefixes are being advertised using a legacy route advertisement.

C.

The advertised prefix of 10.20.30.0/24 is being advertised through the redistribution of another routing protocol.

D.

The output shows all prefixes advertised by all neighbors as well as the local router.

Buy Now
Questions 7

Exhibit.

Refer to the exhibit, which shows two entries that were generated in the FSSO collector agent logs.eeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeee

What three conclusions can you draw from these log entries? {Choose three.)

Options:

A.

Remote registry is not running on the workstation.

B.

The user ' s status shows as " not verified " in the collector agent.

C.

DNS resolution is unable to resolve the workstation name.

D.

The FortiGate firmware version is not compatible with that of the collector agent.

E.

A firewall is blocking traffic to port 139 and 445.

Buy Now
Questions 8

What can cause an IKEv2 tunnel to go down after it was initially brought up successfully?

Options:

A.

Mismatched traffic selectors (phase 2 / “quick-mode selectors”) were detected during the CREATE_CHILD_SA exchange.

B.

A mismatched proposal was detected during the IKE_AUTH exchange.

C.

A mismatched pre-shared key was detected during the IKE_AUTH exchange.

D.

A mismatched Diffie-Hellman group was detected during the IKE_SA_INIT exchange.

Buy Now
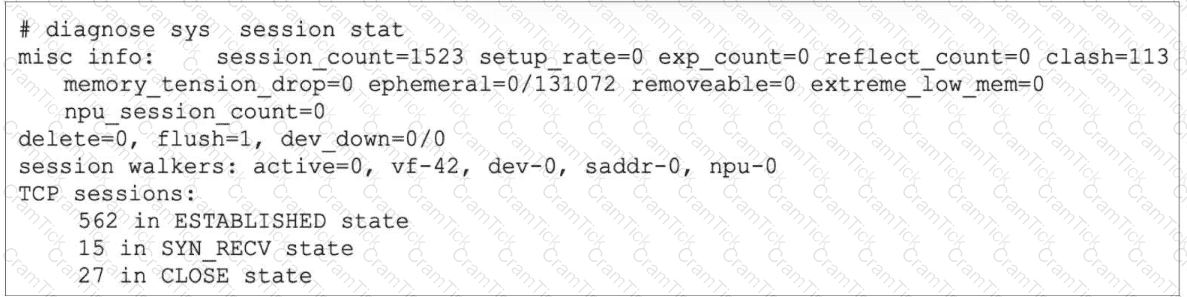
Questions 9

Refer to the exhibit.

The partial output of diagnose sys session stat command is shown.

Which statement about the output shown in the exhibit is correct?

Options:

A.

113 sessions have been dropped because of memory page exhaustion.

B.

There have been 131072 recorded ephemeral sessions but there are no current ones.

C.

562 TCP sessions have their proto_state set to 01 if there is no inspection.

D.

27 sessions have expired but are still in the session table in case any out-of-order packets arrive.

Buy Now
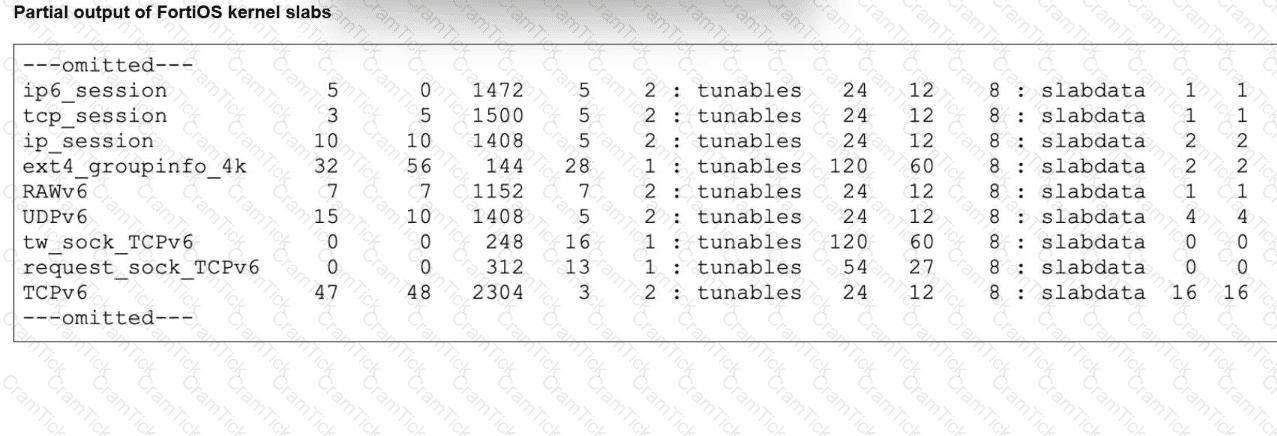
Questions 10

Refer to the exhibit.

The partial output of FortiOS kernel slabs is shown. Which statement about total slab size is true?

Options:

A.

The total slab size of the ip_session Tlab is 14080 kB and is associated with the user space.

B.

The total slab size of the tcp_session slab is 7500 kB and is associated with the kernel.

C.

The total slab size of the ip6_session slab is 1472 kB and is associated with the kernel.

D.

The total slab size of the UDPv6 slab is 14080 kB and is associated with the user space.

Buy Now
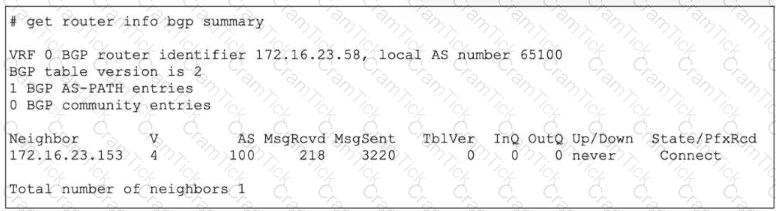
Questions 11

Refer to the exhibit.

The output of a BGP debug command is shown.

Why has the local router at 172.16.23.58 been unable to establish adjacency with its only neighbor?

Options:

A.

The neighbor router has become unreachable, which is evident by the low ratio of messages received to messages sent.

B.

The local router has not received an OPEN message from the neighbor.

C.

The local router has not received a SYN/ACK packet from the neighbor.

D.

There is no active route to the BGP neighbor.

Buy Now
Questions 12

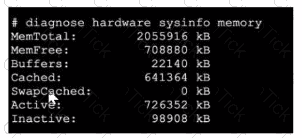
Exhibit.

Refer to the exhibit, which shows a partial output of diagnose hardware aysinfo memory.

Which two statements about the output are true? (Choose two.)

Options:

A.

There are 98908 kB of memory that will never be used.

B.

The user space has 708880 kB of physical memory that is not used by the system.

C.

The I/O cache, which has 641364 kB of memory allocated to it.

D.

The value indicated next to the inactive heading represents the currently unused cache page.

Buy Now
Questions 13

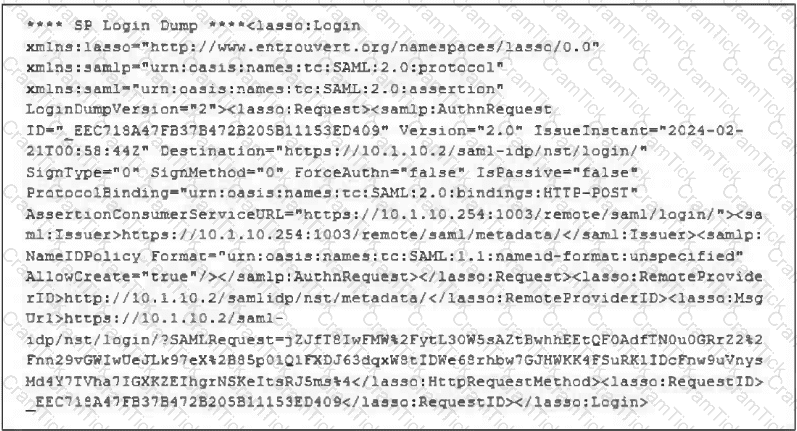
Refer to the exhibit.

The output from using the command diagnose debug application samld -1 to diagnose a SAML connection is shown. Based on this output, which two conclusions can you draw? (Choose two answers)

Options:

A.

The IdP IP address is 10.1.10.254.

B.

The SP IP address is 10.1.10.254.

C.

The SP IP address is 10.1.10.2.

D.

The IdP IP address is 10.1.10.2.

Buy Now
Questions 14

What are three key routing principles of SD-WAN? (Choose three.)

Options:

A.

SD-WAN rules are skipped if the best route to the destination is a static route.

B.

SD-WAN members are skipped if they do not have a valid route to the destination.

C.

Internet Service Database (ISDB) routes have precedence over SD-WAN rules.

D.

SD-WAN rules are skipped if the best route to the destination is not an SD-WAN member.

E.

Routes to directly connected subnets always have precedence over SD-WAN rules.

Buy Now
Questions 15

Refer to the exhibit, which shows the port1 interface configuration on FortiGate and partial session information for ICMP traffic.
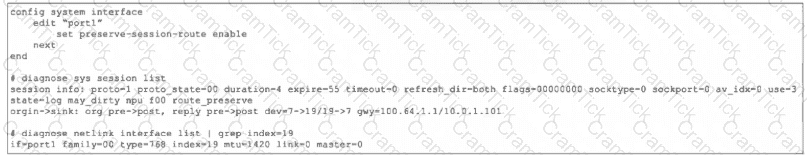
What happens to the session information if a routing change occurs that affects this session?

Options:

A.

Only the interface and gateway information for dev=7 will be removed.

B.

The session information will not change unless the current route has been removed from the routing table.

C.

The session will be flagged as dirty but no route lookups will be performed.

D.

Sessions involving port7 or port19 will not have their routing information flushed.

Buy Now
Questions 16

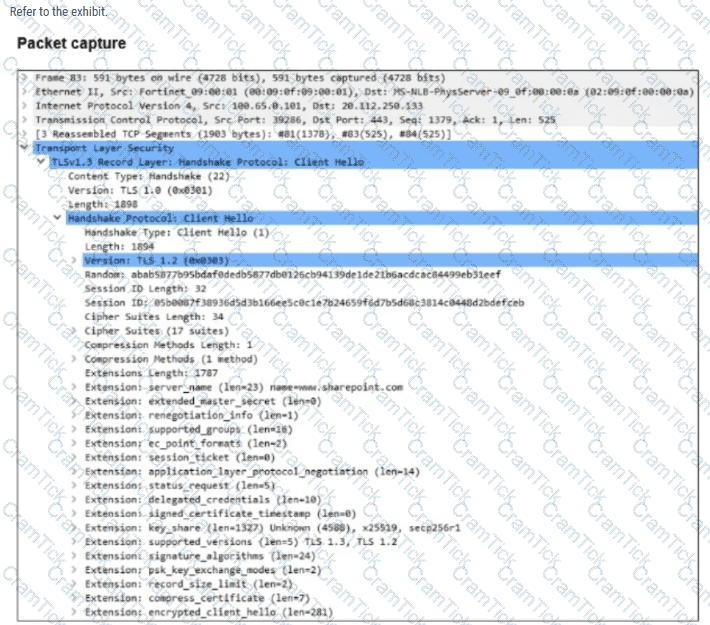
Refer to the exhibit.

The packet capture output of a ClientHello message is shown.

You are updating a firewall policy that includes SSL certificate inspection. You are capturing packets from traffic passing through this firewall policy.

Which two statements about the packet capture are correct? (Choose two.)

Options:

A.

You can effectively apply an antivirus security profile to this traffic.

B.

You can effectively apply a web filtering profile to this traffic.

C.

The subject alternative name (SAN) is necessary to apply security profiles.

D.

The client supports only TLS versions 1.2 and 1.3.

Buy Now
Questions 17

Refer to the exhibit.

The exhibit shows the output from using the command diagnose debug application samld -1 to diagnose a SAML connection.
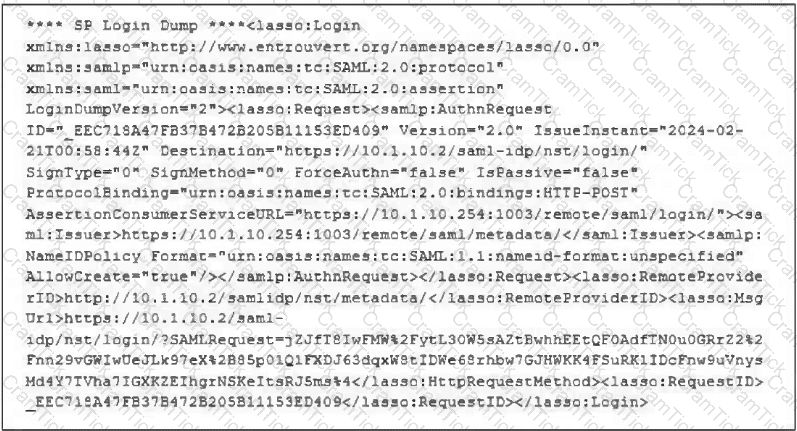
Based on this output, what can you conclude?

Options:

A.

Active Directory is used for authentication.

B.

The authentication request is for an SSL VPN connection.

C.

The IdP IP address is 10.1.10.254.

D.

The IdP IP address is 10.1.10.2.

Buy Now
Questions 18

A FortiGate administrator is troubleshooting a VPN that is failing to establish.

As a first step, the administrator is attempting to sniff the traffic using the command:

# diagnose sniffer packet any ‘’udp port 500 or udp port 4500 or esp’’ 4

After several minutes there is still no output. What is the most Likely reason for this?

Options:

A.

The VPN is configured to use IKE over TCP

B.

esp is not a valid sniffer argument.

C.

The ISP is blocking all VPN traffic.

D.

Mismatched IKE versions are detected on the VPN peers

Buy Now
Questions 19

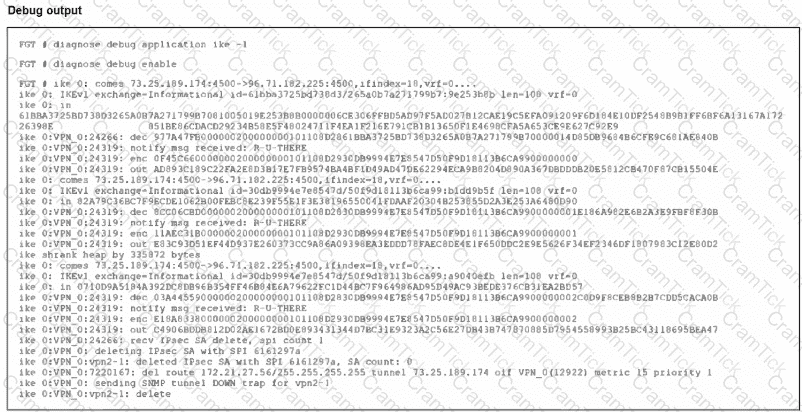
Refer to the exhibit.

An IPsec VPN tunnel is dropping, as shown by the debug output.

Analyzing the debug output, what could be causing the tunnel to go down?

Options:

A.

Phase 2 drops but Phase 1 is up.

B.

Dead Peer Detection is not receiving its acknowledge packet.

C.

The tunnel drops during rekey negotiation.

D.

The tunnel drops after the timer expires.

Buy Now
Questions 20

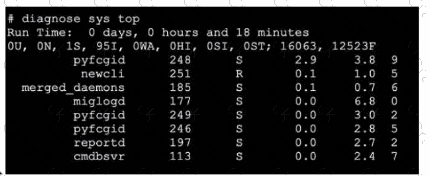
Refer to the exhibit.

Which three pieces of information does the diagnose sys top command provide? (Choose three.)

Options:

A.

The miglogd daemon is running on CPU core ID 0.

B.

The diagnose sys top command has been running for 18 minutes.

C.

The miglogd daemon would be on top of the list, if the administrator pressed m on the keyboard.

D.

The cmdbsvr process is occupying 2.4% of the total user memory space.

E.

If the neweli daemon continues to be in the R state, it will need to be manually restarted.

Buy Now
Questions 21

Refer to the exhibit, which shows the output of the command get router info bgp neighbors 100.64.2.254 advertised-routes.
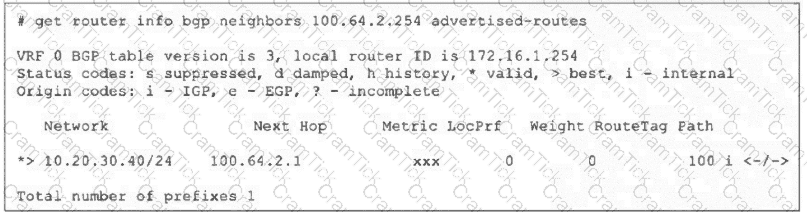
What can you conclude from the output?

Options:

A.

The BGP state of the two BGP participants is OpenConfirm.

B.

The router ID of the neighbor is 100.64.2.254.

C.

The BGP neighbor is advertising the 10.20.30.40/24 network to the local router.

D.

The local router is advertising the 10.20.30.40/24 network to its BGP neighbor.

Buy Now
Questions 22

Refer to the exhibit, which a network topology and a partial routing table.
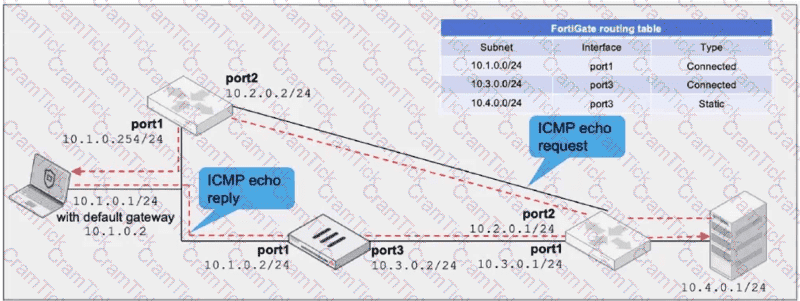
FortiGate has already been configured with a firewall policy that allows all ICMP traffic to flow from port1 to port3.

Which changes must the administrator perform to ensure the server at 10.4.0.1/24 receives the echo reply from the laptop at 10.1.0.1/24?

Options:

A.

Enable asymmetric routing under config system settings.

B.

Change the configuration from strict RPF check mode to feasible RPF check mode.

C.

A firewall policy that allows all ICMP traffic from port3 to port1.

D.

Modify the default gateway on the laptop from 10.1.0.2 to 10.2.0.2.

Buy Now
Questions 23

Which two statements about an auxiliary session ate true? (Choose two.)

Options:

A.

With the auxiliary session selling disabled, only auxiliary sessions are offloaded.

B.

With the auxiliary session setting enabled. ECMP traffic is accelerated to the NP6 processor.

C.

With the auxiliary session setting enabled. Iwo sessions are created in case of routing change.

D.

With the auxiliary session setting disabled, for each traffic path. FortiGate uses the same auxiliary session.

Buy Now
Questions 24

Which three common FortiGate-to-collector-agent connectivity issues can you identify using the FSSO real-time debug? (Choose three.)

Options:

A.

The SSL certificate used for FSSO over SSL has expired.

B.

The connection was refused. There may be a mismatch of the TCP port.

C.

FortiGate cannot reach the IP address of the collector agent.

D.

The pro-shared key does not match

E.

The group filters do not match.

Buy Now
Questions 25

During the last network migration, the IT department discovered that all-zero phase selectors in phase 2 IPsec configurations impacted network operations.

What are two valid recommendations to prevent potential invalid paths during future migrations? (Choose two.)

Options:

A.

Configure routing protocols to specify allowed subnets over the tunnel.

B.

Configure an IPsec aggregate to create redundancy between each firewall peer.

C.

Configure an IP address on the IPsec interface of each firewall to establish unique peer connections and avoid impacting network operations.

D.

Configure the VPN with the exact network segments that will be encrypted in the phase 2 selectors.

Buy Now
Questions 26

In IKEv2, which exchange establishes the first CHILD_SA?

Options:

A.

IKE_SA_INIT

B.

INFORMATIONAL

C.

CREATE_CHILD_SA

D.

IKE_AUTH

Buy Now
Questions 27

While troubleshooting a FortiGate web filter issue, users report that they cannot access any websites, even though those sites are not explicitly blocked by any web filter profiles that are applied to firewall policies.
What are the three most likely reasons for this behavior? (Choose three answers)

Options:

A.

The web filter cache has been cleared causing all websites to take longer to be rated.

B.

The SSL/TLS deep inspection was configured but the browsers do not have the FortiGate certificate installed.

C.

The webfilter-force-off setting has been enabled under config system fortiguard.

D.

The DNS server is unreachable, preventing URL resolution.

E.

The FortiGuard Web Filtering license has expired, causing FortiGate to apply the default block action.

Buy Now
Questions 28

Which exchange lakes care of DoS protection in IKEv2?

Options:

A.

Create_CHILD_SA

B.

IKE_Auth

C.

IKE_Req_INIT

D.

IKE_SA_NIT

Buy Now
Questions 29

Refer to the exhibit, which shows a partial output of the fssod daemon real-time debug command.

What two conclusions can you draw from the output? (Choose two.)

Options:

A.

The workstation with IP 10.124.2.90 will be polled frequently using TCP port 445 to see if the user is still logged on.

B.

The logon event can be seen on the collector agent installed on Windows.

C.

FSSO is using DC agent mode to detect logon events.

D.

FSSO is using agentless polling mode to detect logon events.

Buy Now
Questions 30

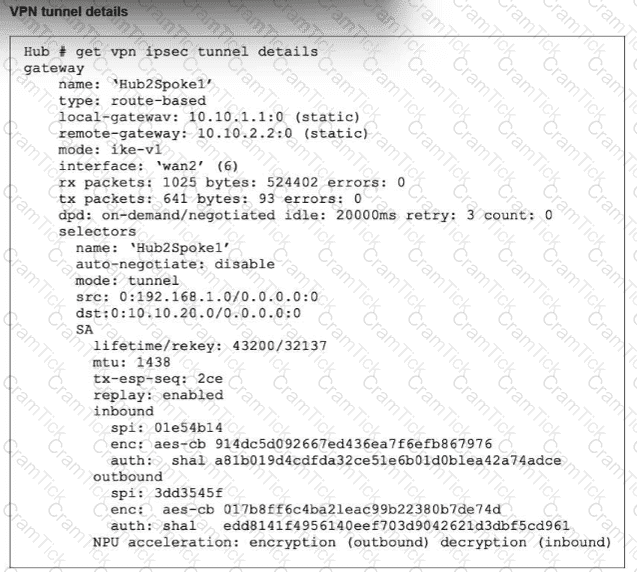
Refer to the exhibit.

Partial output of the get vpn ipsec tunnel details command is shown. Based on the output, which two statements are correct? (Choose two.)

Options:

A.

The npu_flag for this tunnel is 02.

B.

Different SPI values are a result of auto-negotiation being disabled for phase2 selectors.

C.

The npu_flag for this tunnel is 03.

D.

Anti-replay is enabled.

Buy Now
Questions 31

Which of the following regarding protocol states is true? (Choose one answer)

Options:

A.

proto_state=00 indicates that UDP traffic flows in both directions.

B.

proto_state=01 indicates an established TCP session.

C.

proto_state=10 indicates an established TCP session.

D.

proto_state=01 indicates one-way ICMP traffic.

Buy Now
Questions 32

Refer to the exhibit, which shows a truncated output of a real-time RADIUS debug.
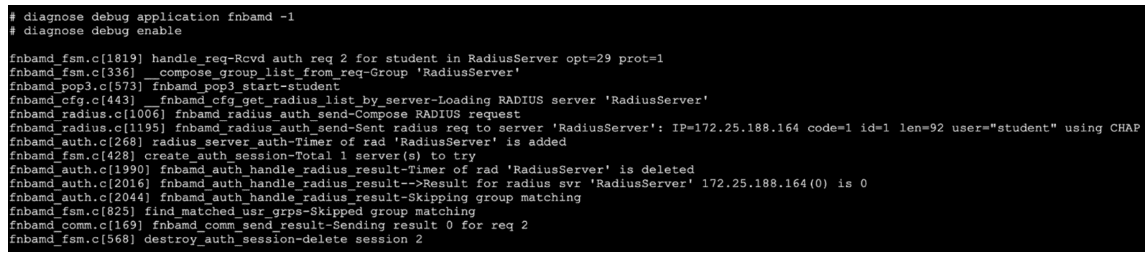
Which two statements are true? (Choose two answers)

Options:

A.

The RADIUS server queried for authentication is located at IP address 172.25.188.164.

B.

Authentication was unsuccessful.

C.

The authentication scheme used was pop3.

D.

Authentication was successful.

E.

Two-factor authentication was required.

Buy Now
Questions 33

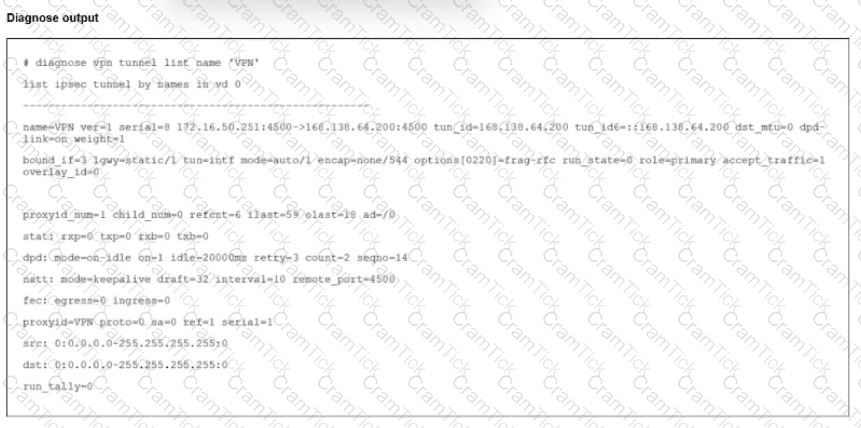
Refer to the exhibit.

The output of the command diagnose vpn tunnels liar is shown.

Which two statements accurately describe the status of the tunnel? (Choose two.)

Options:

A.

Phase 2 is down

B.

Phase 1 is down.

C.

There is currently no traffic traversing the tunnel

D.

Both Phase 1 and Phase 2 were negotiated successfully.

Buy Now
Questions 34

You want to harden the SSL/SSH inspection profile for access to HTTPS web servers.

Which two configuration changes allow you to remove vulnerabilities? (Choose two answers.)

Options:

A.

Set unsupported-ssl-version to block.

B.

Set Server certificate SNI check to Enable.

C.

Set Untrusted SSL certificates to Ignore.

D.

Set min-allowed-ssl-version to ssl-3.0.

Buy Now
Questions 35

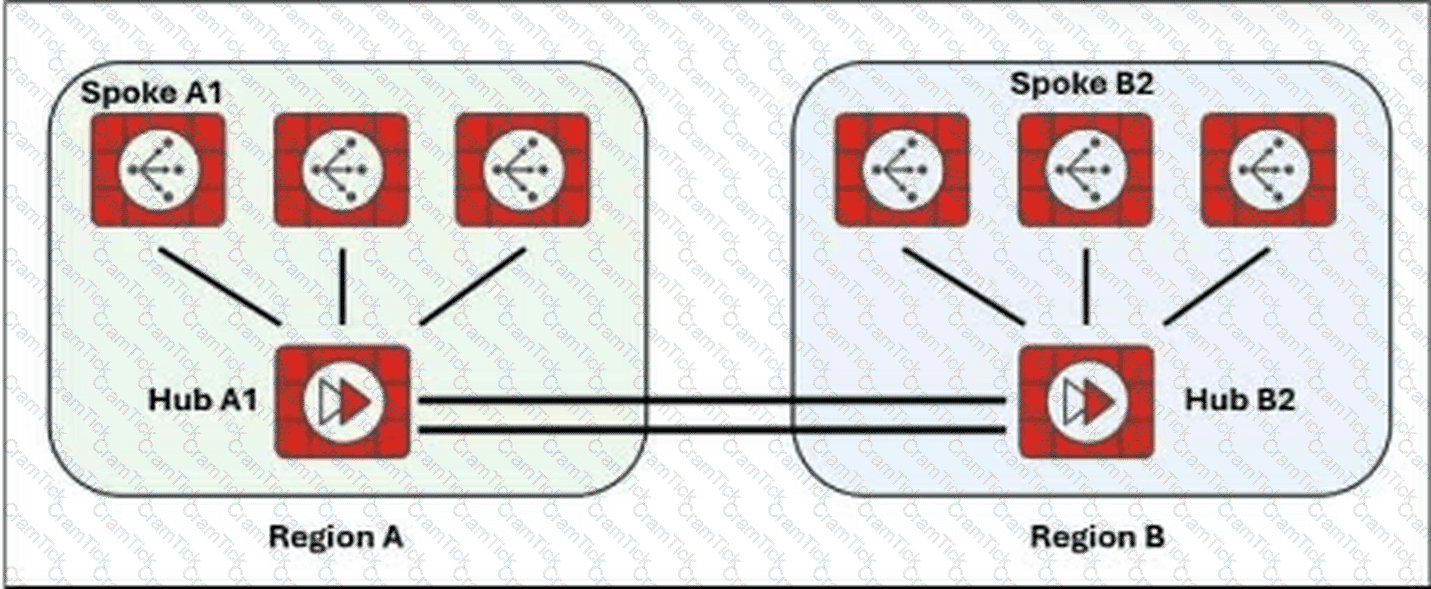
Refer to the exhibit.

Two hub-and-spoke groups are connected through redundant site-to-site IPsec VPNs between Hub 1 and Hub 2.

Which two configuration settings are required for Spoke A1 to establish an auto-discovery VPN (ADVPN) shortcut with Spoke B2? (Choose two.)

Options:

A.

On the spokes, auto-discovery-receiver must be enabled on the IPsec VPNs to the hubs.

B.

On the hubs, auto-discovery-forwarder must be enabled on the IPsec VPNs between the hubs.

C.

On the spokes, auto-discovery-sender must be enabled on the IPsec VPNs to the hubs.

D.

On the hubs, auto-discovery-receiver must be enabled on the IPsec VPNs to the spokes.

Buy Now
Questions 36

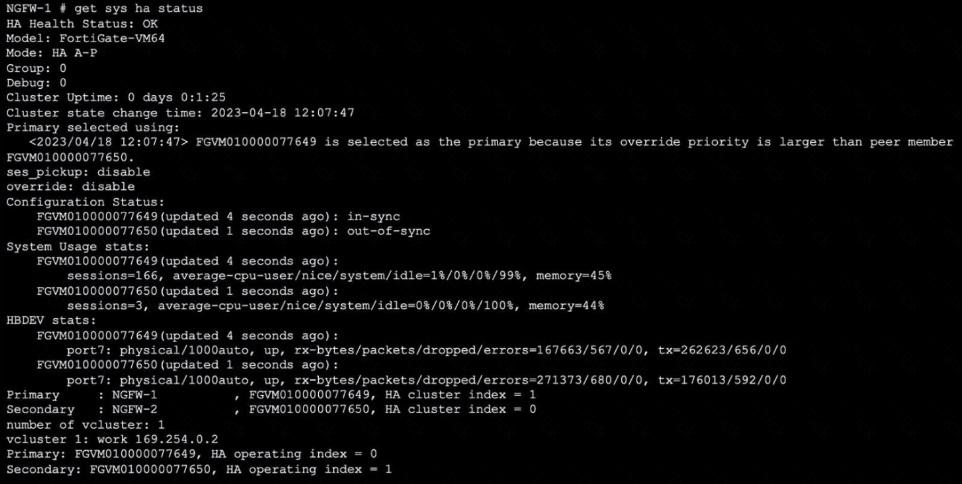
Exhibit.

Refer to the exhibit, which shows the output of get system ha status.

NGFW-1 and NGFW-2 have been up for a week.

Which two statements about the output are true? (Choose two.)

Options:

A.

If a configuration change is made to the primary FortiGate at this time, the secondary will initiate a synchronization reset.

B.

If port 7 becomes disconnected on the secondary, both FortiGate devices will elect itself as primary.

C.

If FGVM...649 is rebooted. FGVM...650 will become the primary and retain that role, even after FGVM...649 rejoins the cluster.

D.

If no action is taken, the primary FortiGate will leave the cluster because of the current sync status.

Buy Now
Questions 37

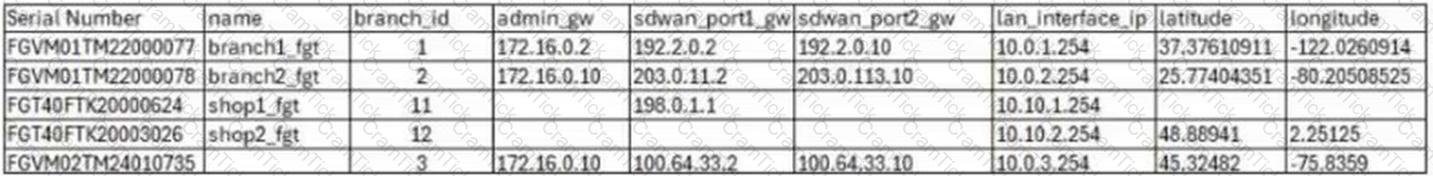
Refer to the exhibit.

Original video exhibit showing a FortiManager ZTP CSV file with device serial numbers, names, branch IDs, gateways, and metadata columns.

For your zero-touch provisioning (ZTP) deployment, you review the CSV file shown in the exhibit and note that it is missing important information.

Which two elements must you change before you can import it into FortiManager? (Choose two.)

Options:

A.

You must define a value for each device and each user-defined metadata variable.

B.

You must define a name for each device.

C.

You must define a value for each device and each metadata variable that defines an IP address.

D.

You must associate a device blueprint with each device.

Buy Now
Questions 38

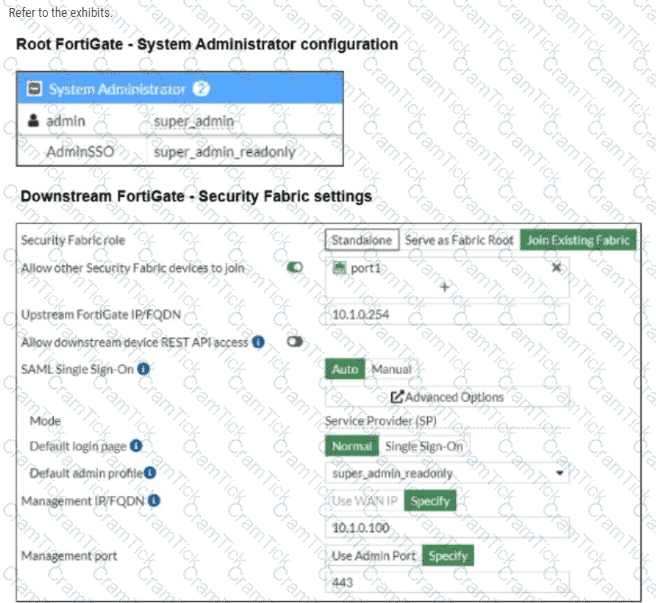
Refer to the exhibits.

The system administrator settings configured on the root FortiGate and the Security Fabric settings configured on a downstream FortiGate are shown.

When prompted to sign in with Security Fabric to the downstream FortiGate, a user enters the single sign-on (SSO) provider credentials.

What happens next for the user?

Options:

A.

The user is redirected to the root FortiGate.

B.

The user accesses the downstream FortiGate with super_admin_readonly privileges.

C.

The user accesses the root FortiGate with AdminSSO privileges.

D.

The user receives an authentication failure message.

Buy Now
Questions 39

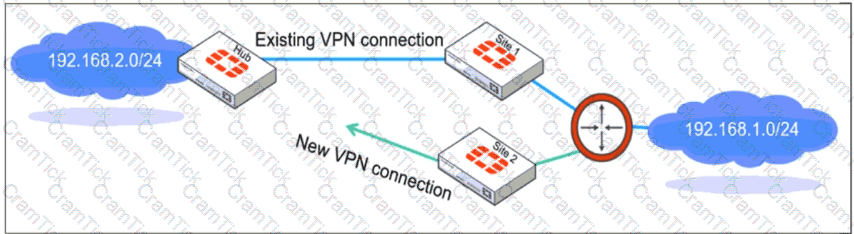
Refer to the exhibit.

The network diagram shows the addition of Site 2 with an overlapping network segment to the existing IPsec VPN connection between the hub and Site 1.

Which IPsec phase 2 configuration must you make on the FortiGate hub to enable equal-cost multipath (ECMP) routing when multiple remote sites connect with overlapping subnets?

Options:

A.

Set route-overlap to either use-new or use-old.

B.

Set multipath to enable.

C.

Set route-overlap to allow.

D.

Set net-device to ecmp.

Buy Now
Questions 40

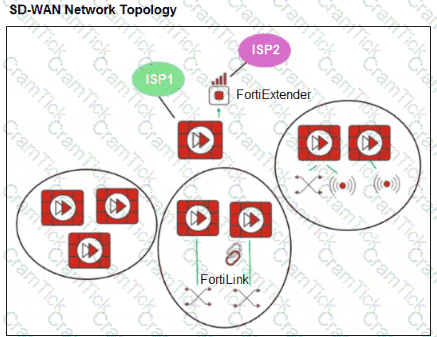
Refer to the exhibit.

You want to configure SD-WAN on a network, as shown in the exhibit. The network contains many FortiGate devices. Some are used as next-generation firewalls (NGFWs), and some are deployed with extensions such as FortiSwitch, FortiAP, or FortiExtender.

Which factor should you consider when planning the deployment? (Choose one answer.)

Options:

A.

You can build an SD-WAN topology that includes all devices. The hubs must be devices without extensions.

B.

You should exclude FortiGate devices with FortiLink connections from the SD-WAN topology.

C.

You should build multiple SD-WAN topologies. Each topology should contain only one type of extension.

D.

You can build an SD-WAN topology that includes all devices. The hubs can be FortiGate devices with FortiExtender.

Buy Now
Questions 41

Refer to the exhibit, which shows the output of get router info ospf neighbor.
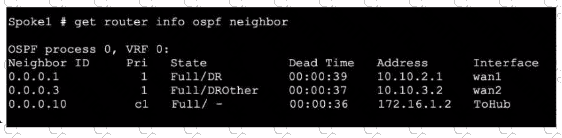
What can you conclude from the command output?

Options:

A.

The network type connecting the local Fortigate and OSPF neighbor 0.0.0.10 is point-to-point.

B.

All neighbors are in area 0.0.0.0.

C.

The local FortiGate is the BDR.

D.

The local FortiGate is not a DROther.

Buy Now
Questions 42

You configure the overlay tunnels for an SD-WAN hub-and-spoke topology defined with IPsec tunnels, BGP on loopback, and dynamic BGP.

Which two are recommended IPsec settings for this topology? (Choose two answers.)

Options:

A.

On the hub, set the tunnel type to static.

B.

On the hub, set the parameter mode-cfg to enable.

C.

On the spoke, set the parameter net-device to enable.

D.

On the spoke, configure the parameter localid.

Buy Now
Questions 43

Refer to the exhibit, which shows one way communication of the downstream FortiGate with the upstream FortiGate within a Security Fabric.
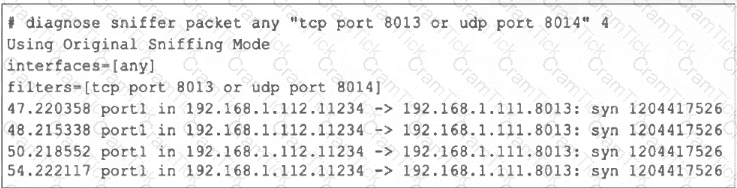
What three actions must you take to ensure successful communication? (Choose three.)

Options:

A.

You must authorize the downstream FortiGate on the root FortiGate.

B.

FortiGate must not be in NAT mode.

C.

Ensure TCP port 8013 is not blocked along the way.

D.

You must enable Security Fabric/Fortitelemetry on the receiving interface of the upstream FortiGate.

E.

Ensure the port for Neighbor Discovery has been changed.

Buy Now
Questions 44

Refer to the exhibit.

The output of a BGO debug command is shown.
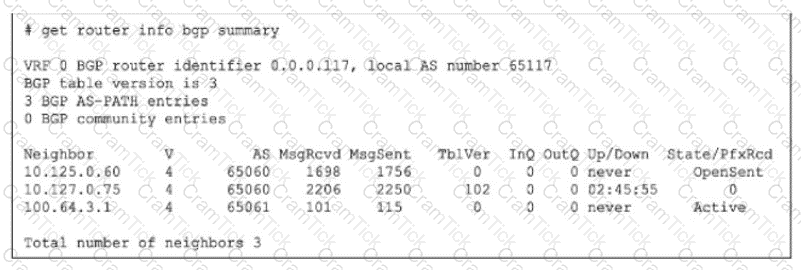
What is the most likely reason that the local FortiGate is not receiving any prefixes from its neighbors?

Options:

A.

The local router is waiting for the keepalive message from the router 10.125.0.60.

B.

None of the three neighbors has successfully established the TCP three-way handshake with the local router.

C.

The router 100.64.3.1 is waiting for the OPEN message from the local router.

D.

The RIB-OUT configuration for router 10.127.0.75 prevents any route advertisement to the local router.

Buy Now
Questions 45

An administrator wants to capture encrypted phase 2 traffic between two FotiGate devices using the built-in sniffer.

If the administrator knows that there Is no NAT device located between both FortiGate devices, which command should the administrator run?

Options:

A.

diagnose sniffer packet any ' udp port 500 '

B.

diagnose sniffer packet any ' lp proto 50 '

C.

diagnose sniffer packet any ' udp port 4500 '

D.

diagnose sniffer packet any ' ah '

Buy Now
Questions 46

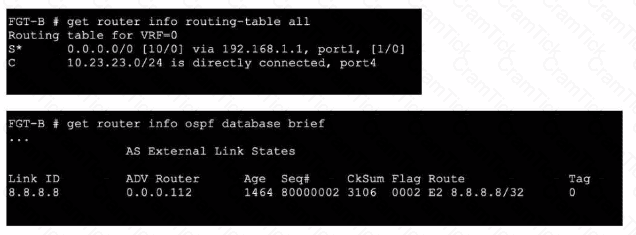
Refer to the exhibits.

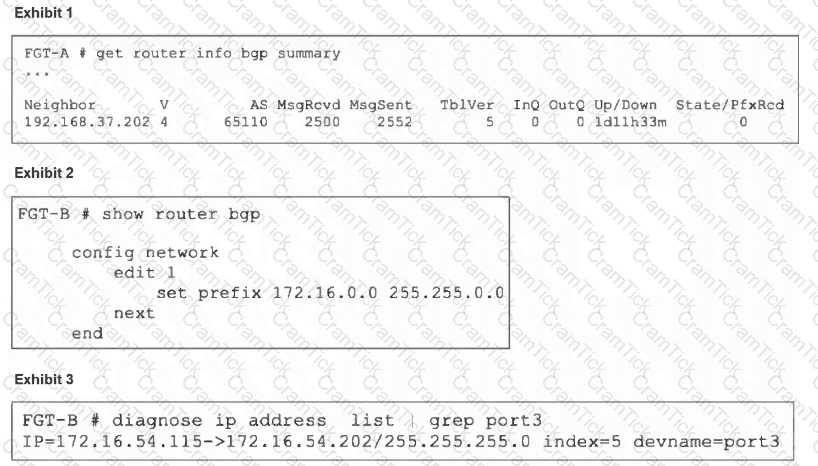
An administrator Is expecting to receive advertised route 8.8.8.8/32 from FGT-A. On FGT-B, they confirm that the route is being advertised and received, however, the route is not being injected into the routing table. What is the most likely cause of this issue?

Options:

A.

A batter route to the 8.8.8.8/32 network exists in the routing table.

B.

FGT-B is configured with a prefix list denying the 8.8.8.8/32 network to be injected into the routing table.

C.

The administrator has misconfigured redistribution of routes on FGT-A.

D.

FGT-B is configured with a distribution list denying the 8.8.8.8/32 network to be injected into the routing table.

Buy Now
Questions 47

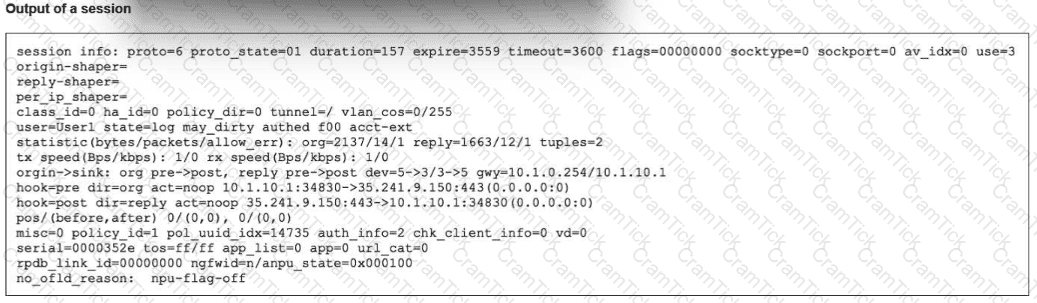
Refer to the exhibit.

The exhibit shows the output of a session. Which two statements are correct? (Choose two.)

Options:

A.

The session did not match a firewall policy.

B.

The gateway to the destination is 10.1.10.1.

C.

The session was initiated from an authenticated user.

D.

The TCP session has been successfully established.

Buy Now
Questions 48

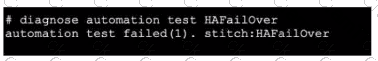
Exhibit.

Refer to the exhibit, which shows the output of diagnose automation test.

What can you observe from the output? (Choose two.)

Options:

A.

The automation stitch test is not being logged.

B.

The automation stitch test failed but the HA failover was successful.

C.

An HA failover occurred.

D.

The test was unsuccessful.

Buy Now
Questions 49

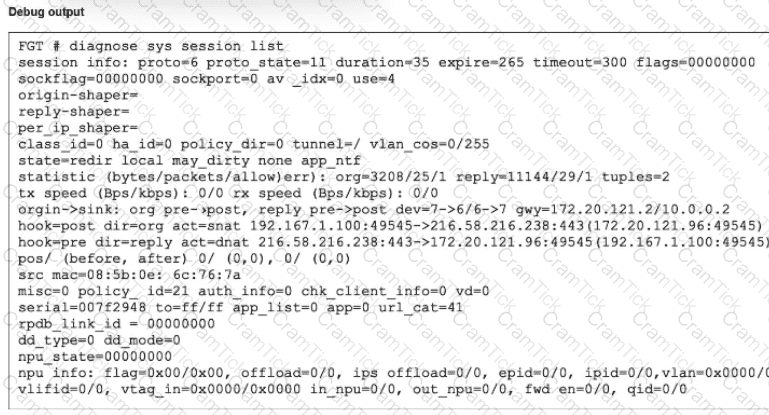
Refer to the exhibit.

Which Iwo statements about FortiGate behavior relating to this session are correct? (Choose two.)

Options:

A.

FortiGate is performing a security profile inspection using the CPU.

B.

FortiGate redirected the client to trio captive portal to authenticate so that a correct policy match could be made

C.

FortiGate either initiated the session or the session terminates at FortiGate.

D.

FortiGate forwarded this session without any inspection.

Buy Now
Questions 50

Which statement about parallel path processing is correct (PPP)?

Options:

A.

PPP chooses from a group of parallel options lo identity the optimal path tor processing a packet.

B.

Only FortiGate hardware configurations affect the path that a packet takes.

C.

PPP does not apply to packets that are part of an already established session.

D.

Software configuration has no impact on PPP.

Buy Now
Questions 51

Refer to the exhibits.

An administrator is attempting to advertise the network configured on port3. However, FGT-A is not receiving the prefix.

Which two actions can the administrator take to fix this problem? (Choose two.)

Options:

A.

Modify the prefix using the network command from 172.16.0.0/16 to 172.16.54.0/24.

B.

Manually add the BGP route on FGT-A.

C.

Restart BGP using a soft reset to force both peers to exchange their complete BGP routing tables.

D.

Use the set network-import-check disable command.

Buy Now
Questions 52

Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate.

Which action will FortiGate take when using the default settings for SSL certificate inspection?

Options:

A.

FortiGate uses the SNI from the user ' s web browser.

B.

FortiGate closes the connection because this represents an invalid SSL/TLS configuration.

C.

FortiGate uses the first entry listed in the SAN field in the server certificate.

D.

FortiGate uses the CN information from the Subject field in the server certificate.

Buy Now
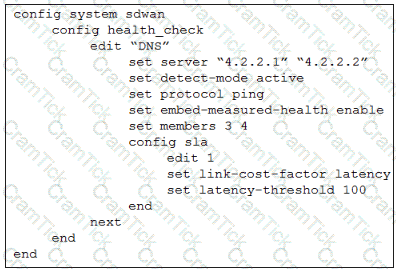
Questions 53

Refer to the exhibit.

The health-check configuration on a FortiGate device used as a spoke is shown.

You notice that the hub FortiGate does not prioritize the traffic as expected.

Which two configuration elements should you check on the hub? (Choose two.)
Options:

A.

The performance SLA uses the same criteria.

B.

The performance SLA has the parameter priority-out-sla configured.

C.

The performance SLA uses the same members.

D.

The performance SLA is configured with set embedded-measure accept.

Buy Now
Exam Code: NSE7_FSN_AR-7.6
Exam Name: Fortinet NSE 7 - Secure Networking 7.6 Architect
Last Update: Nov 17, 2026
Questions: 177
NSE7_FSN_AR-7.6 pdf

NSE7_FSN_AR-7.6 PDF

$22.5  $89.99
NSE7_FSN_AR-7.6 Engine

NSE7_FSN_AR-7.6 Testing Engine

$26.25  $104.99
NSE7_FSN_AR-7.6 PDF + Engine

NSE7_FSN_AR-7.6 PDF + Testing Engine

$35  $139.99