Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: fifty75ct

NSE6_FMG_AD-7.6 Fortinet NSE 6 - FortiManager 7.6 Administrator Questions and Answers

Questions 4

While attempting to push a NetFlow configuration script through the FortiManager policy package: an administrator encounters an error stating that an object is unrecognized in line 4.
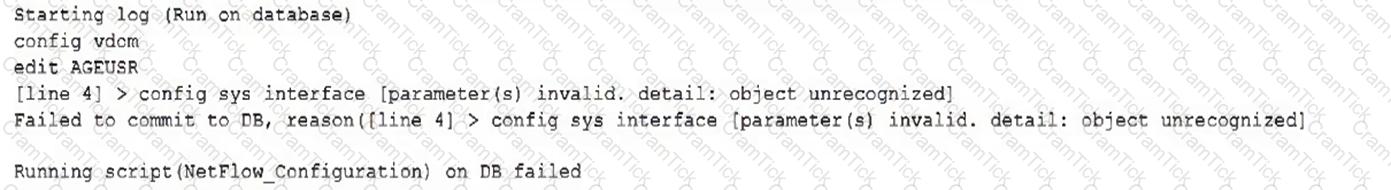
What must the administrator do to successfully apply the NetFlow configuration script and avoid the object unrecognized error?

Options:

A.

Make sure the user running the script has full access to the VDOM—AGEUSR.

B.

Run the script on the device database.

C.

Use metadata variables if they use VDOMs in the script.

D.

Create a normalized interface on the policy layer before running the script.

Buy Now
Questions 5

What allows FortiManager to run CLI scripts on FortiGate devices without prompting for SSH authentication each time?

Options:

A.

FortiGate devices using the legacy login method.

B.

The secure management tunnel between FortiManager and FortiGate devices.

C.

The script using the Remote FortiGate Directly via CLI option.

D.

The script on the FortiManager device database.

Buy Now
Questions 6

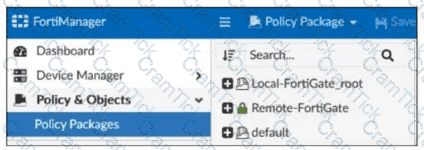
Refer to the exhibit.

Which two statements about the configuration shown in the exhibit are true? Choose two answers.

Options:

A.

An administrator can lock the Local-FortiGate_root policy package.

B.

The administrator created a snapshot of the Remote-FortiGate policy package.

C.

The FortiManager ADOM workspace mode is set to normal.

D.

The FortiManager is in workflow mode.

Buy Now
Questions 7

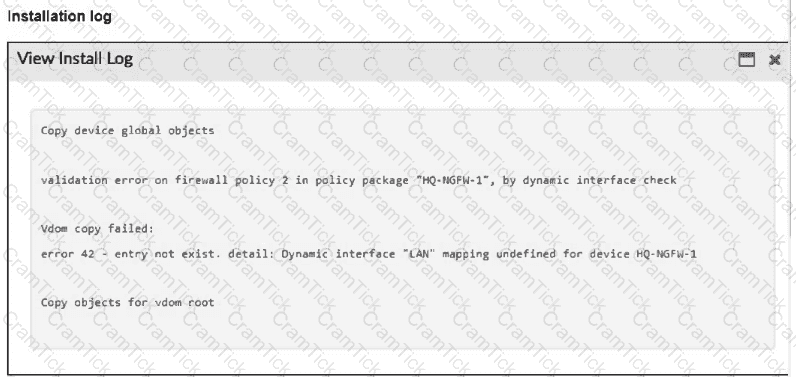
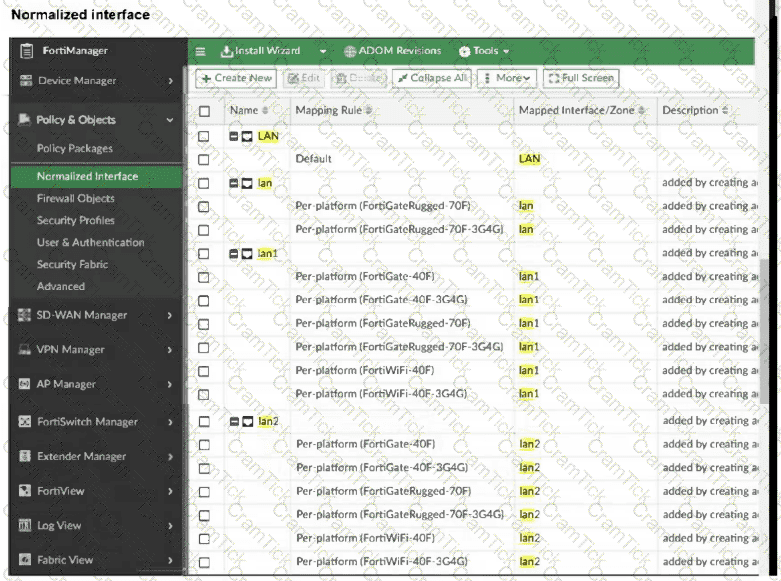
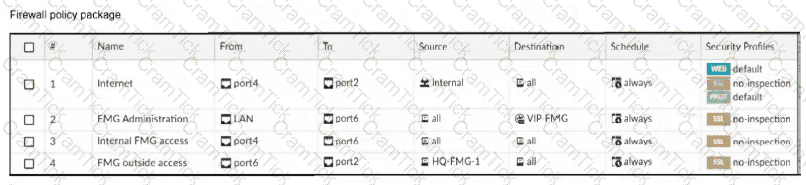
Refer to the exhibits.

An administrator must replace the source LAN interface in policy ID 2 on their FortiGateRugged-70F.

However, when they try to install the policy package, they receive the error shown in the exhibit.

What should the administrator do to resolve the error?

Options:

A.

Use the API to assign a system template interface for FortiGateRugged-70F model.

B.

Use a metadata variable to dynamically assign an interface when this error occurs.

C.

Create a per-device mapping for the LAN interface.

D.

Replace LAN with lan1, which is supported by FortiGateRugged-70F models.

Buy Now
Questions 8

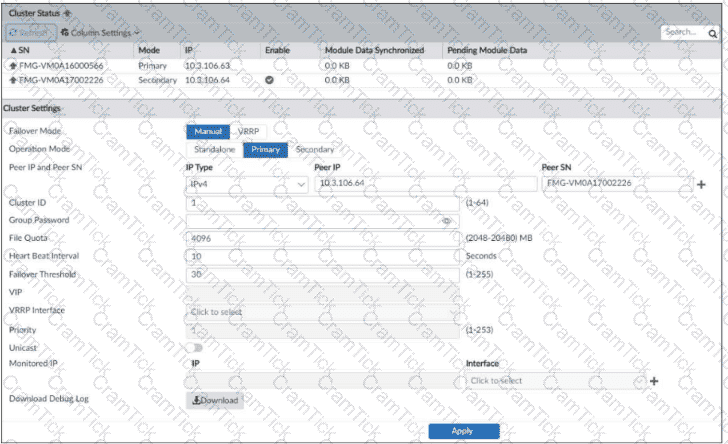
Refer to the exhibit.

Which statement about the environment shown in the exhibit is true? Choose one answer

Options:

A.

You must restart the secondary device if you promote it to primary.

B.

No FortiGuard packages have been synchronized between the cluster members.

C.

A failover will take place after five minutes without receiving heartbeat packets.

D.

FortiAnalyzer features are not enabled on this FortiManager device.

Buy Now
Questions 9

Refer to the following configuration. FortiManager # config system global global# set workspace-mode normal global# end FortiManager # What are two results from the configuration shown in the exhibit? Choose two answers

Options:

A.

The same administrator can lock more than one ADOM at the same time.

B.

Multiple administrators can lock and work on separate ADOMs at the same time.

C.

All changes must be approved before they can be installed on a device.

D.

Concurrent read-write access to an ADOM is disabled.

Buy Now
Questions 10

A service provider administrator has assigned a global policy package to a managed customer ADOM named My_ADOM. The customer administrator has access only to My_ADOM.

How can the customer administrator edit the global header policy of the global policy package?

Options:

A.

The customer administrator can edit the header policy by using workspace mode on the global ADOM.

B.

The customer administrator can edit the header policy by using workflow mode on the global ADOM and My_ADOM.

C.

The service provider administrator can unlock the global policy from the global ADOM to authorize changes to the customer administrator.

D.

The customer administrator cannot edit the global header policy; only the service provider administrator can make changes from the global ADOM.

Buy Now
Questions 11

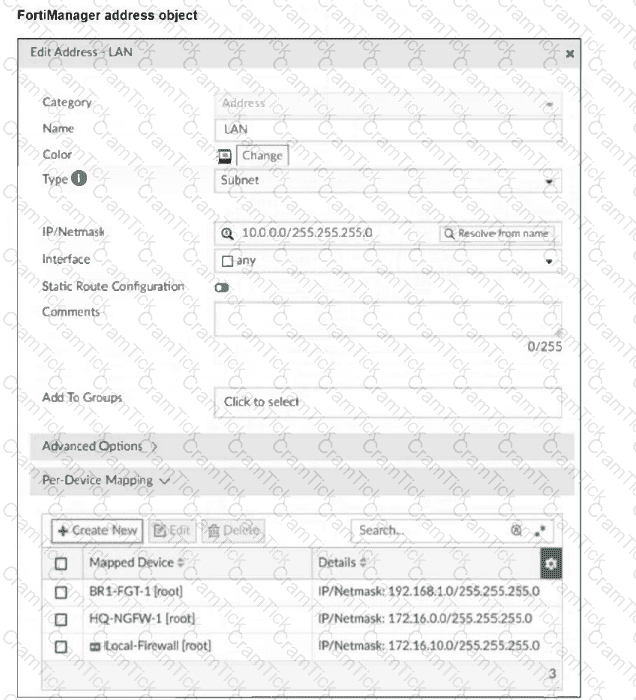
Refer to the exhibits.

Which IP/netmask will be present in the LAN firewall address object on the Remote-Firewall?

Options:

A.

172.16.0.0/255.255.255.0

B.

10.0.0.0/255.255.255.0

C.

192.168.1.0/255.255.255.0

D.

172.16.10.0/255.255.255.0

Buy Now
Questions 12

What is the purpose of ADOM revisions?

Options:

A.

ADOM revisions find unused, duplicate, and unnecessary firewall policies and objects.

B.

ADOM revisions show specific changes in a policy package when it is installed.

C.

ADOM revisions compare previous snapshots of the Policy Package and ADOM-level objects with the device-level database.

D.

ADOM revisions save the current state of all policy packages and objects for an ADOM.

Buy Now
Questions 13

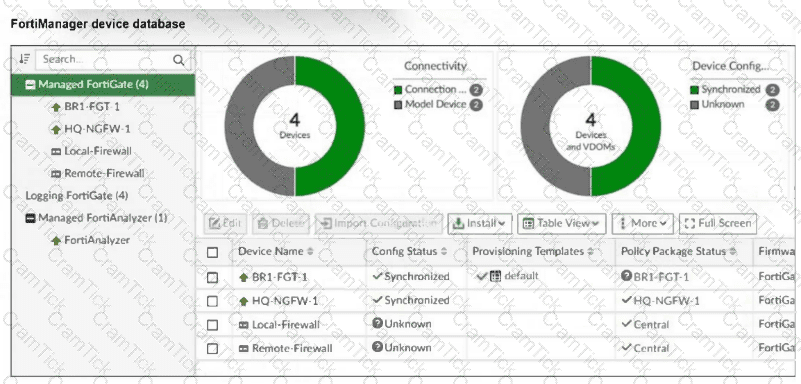
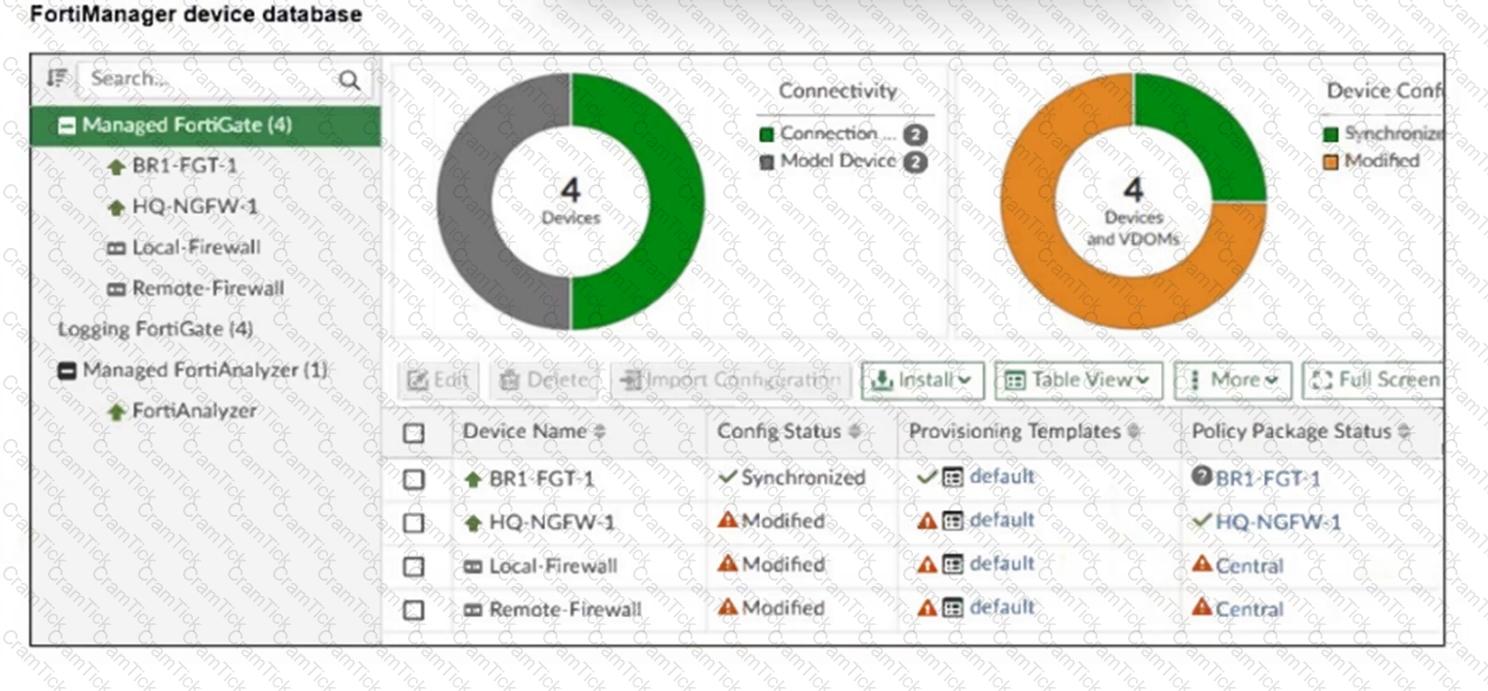
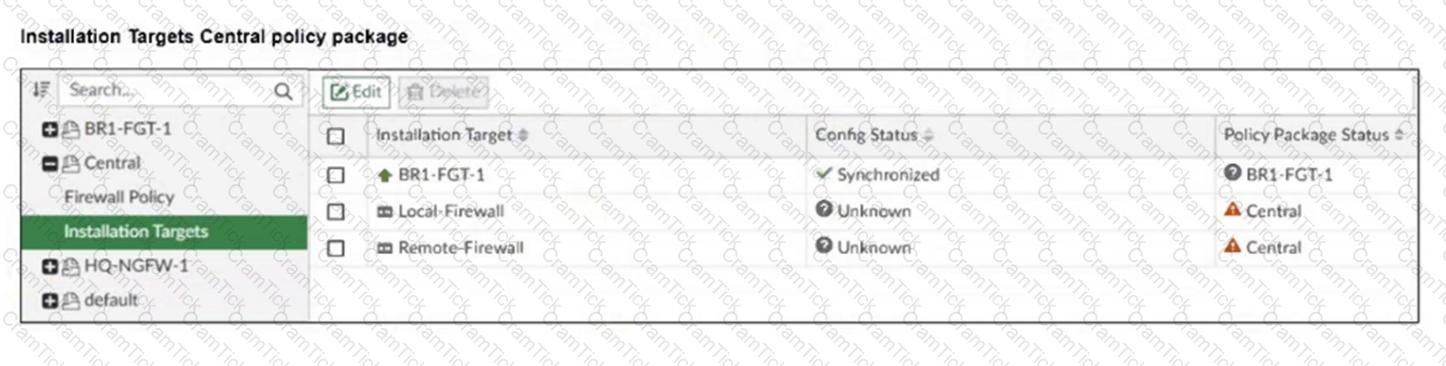
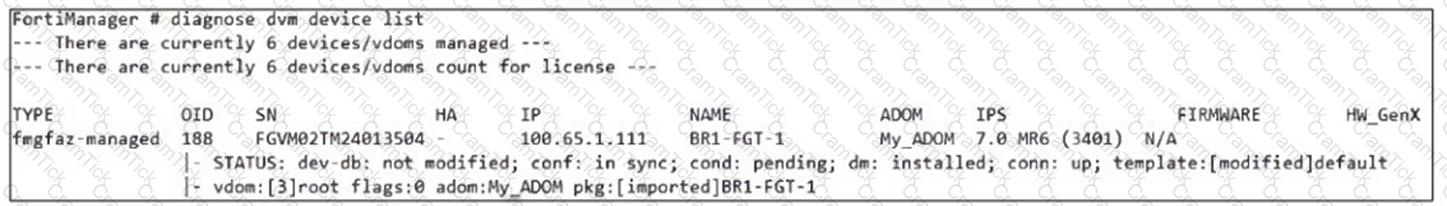
Refer to the exhibits.

An administrator has been asked to install the same policies from a central policy package onto the BR1-FGT-1 firewall.

The administrator added BR1-FGT-1 as a target in the central policy package installation.

What should the administrator do when reinstalling the central policy package on the BR1-FGT-1 firewall?

Options:

A.

Assign only one policy package to the firewall because FortiManager does not allow more than one policy package assigned per device at the same time.

B.

Import the policy package to change the unknown status and synchronize the policy package.

C.

Use the install wizard to install the central policy package on the BR1-FGT-1 firewall.

D.

First resolve the modified status in the configuration and provisioning templates to allow a smooth installation.

Buy Now
Questions 14

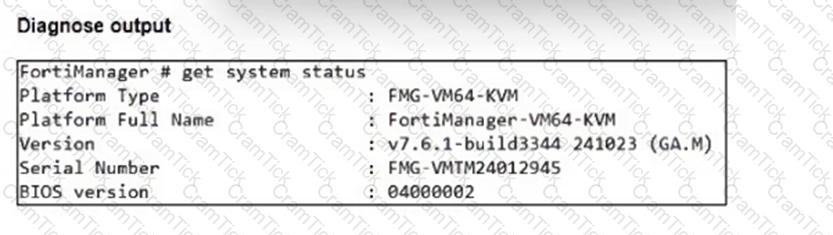
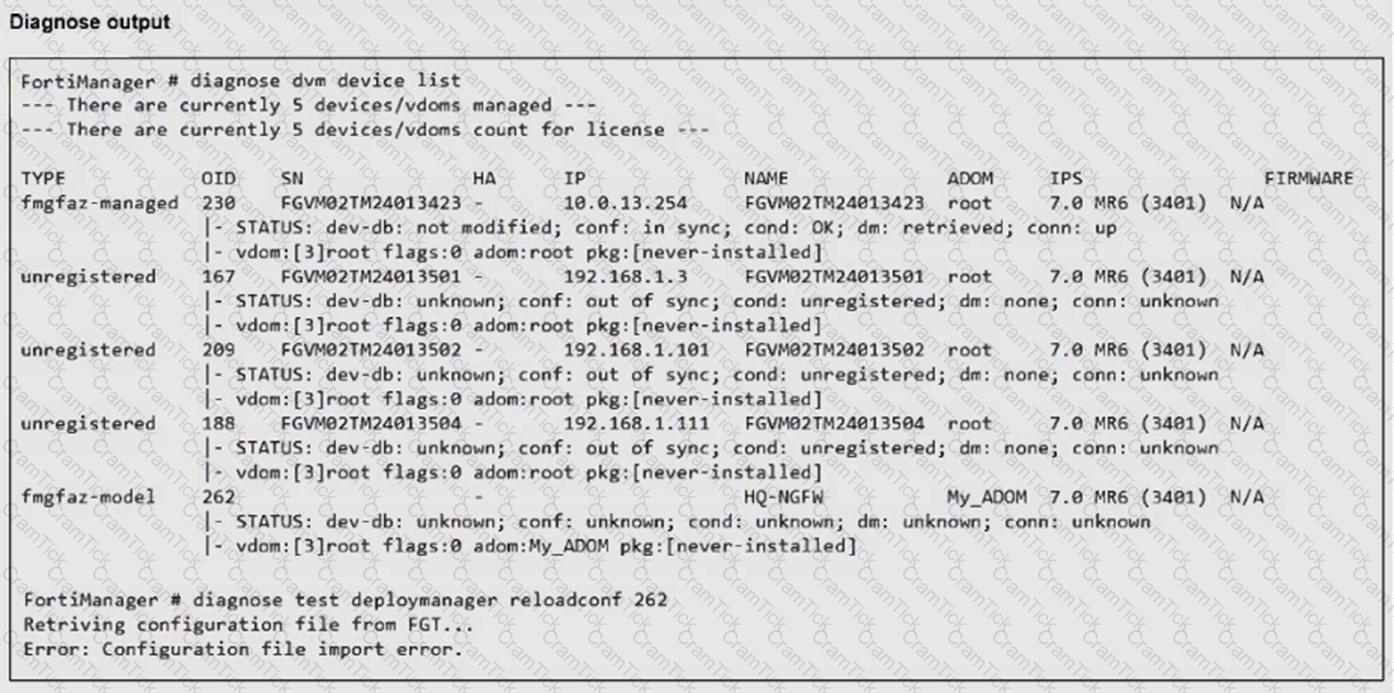
Refer to the exhibits.

An administrator runs the reload failure command diagnose test deploymanager reloadconf 262 on FortiManager.

Why does the administrator receive an error message?

Options:

A.

The administrator must use the FortiGate name instead of the ID number.

B.

The administrator just recently added FortiGate HQ-NGFW as a model device.

C.

FortiManager requires the FortiGate serial number instead of the ID number.

D.

FortiManager does not support FortiOS version 7.0.

Buy Now
Questions 15

An administrator configures a new BGP peer in the FortiManager device-level database of FortiGate. They reinstall the policy package to the managed FortiGate device without any errors. However, when the administrator logs in to FortiGate, they do not see the BGP configuration changes.

What is the most likely reason why FortiManager did not push the BGP peer changes to FortiGate?

Options:

A.

The administrator must run a sanity check on FortiManager to make sure the database is not corrupted.

B.

Fortigate has a BGP template assigned on the FortiManager database.

C.

The administrator must use the Install Wizard and select Install device settings only to push BGP settings

D.

The FortiGate firmware version is different from the FortiManager ADOM version.

Buy Now
Questions 16

Which FortiGate configuration settings is part of an ADOM-level database on FortiManager?

Options:

A.

NSX-T service template

B.

Security template

C.

Routing

D.

SNMP

Buy Now
Questions 17

Refer to the exhibit.

Which two statements about the output are true? (Choose two.)

Options:

A.

The latest revision history for the managed FortiGate does not match the device-level database.

B.

Configuration changes have been installed on FortiGate, updating policy and device-level database.

C.

The latest revision history for the managed FortiGate does match the FortiManager policy database.

D.

The system template default will override device-level database configurations.

Buy Now
Questions 18

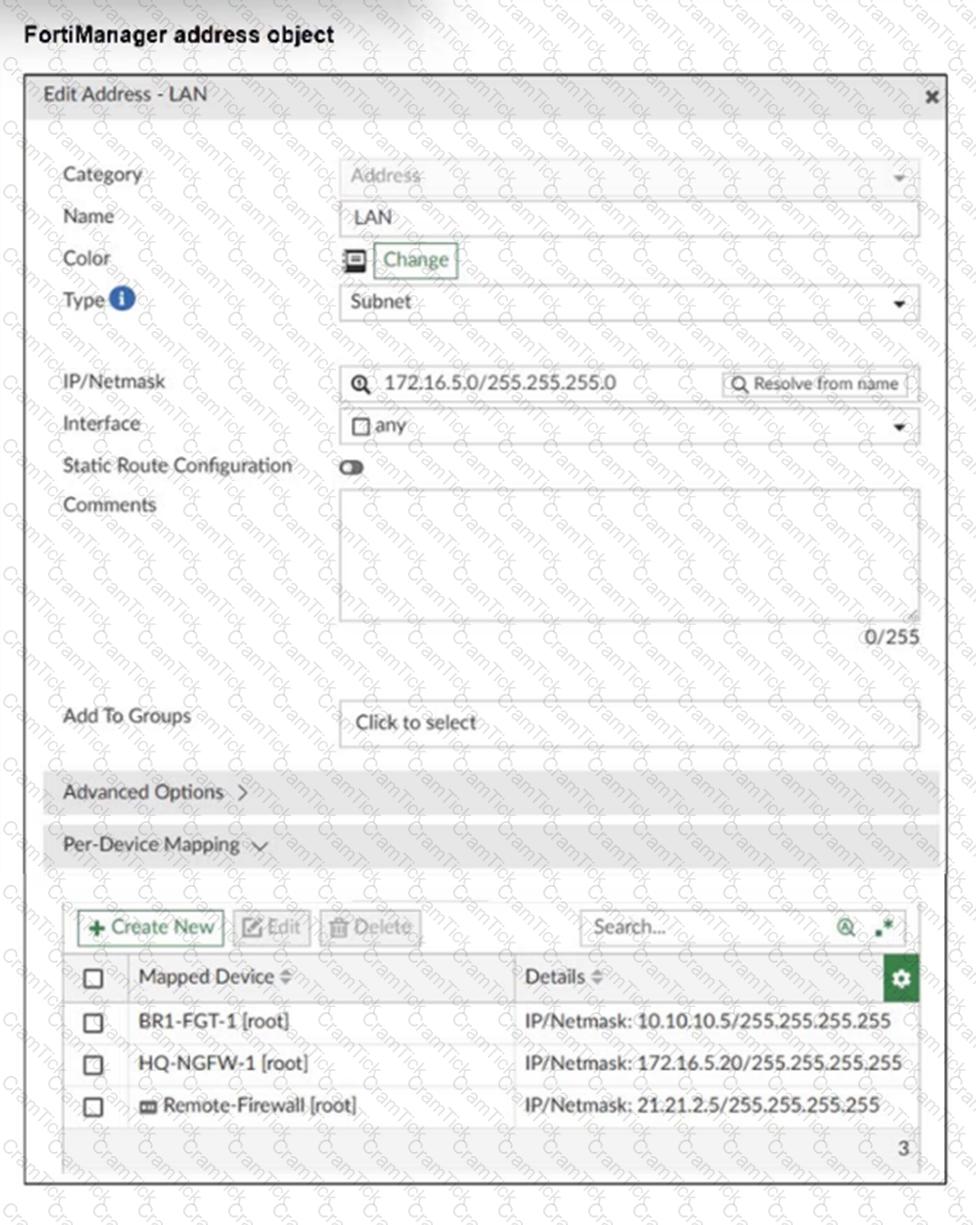
Refer to the exhibit.

An administrator has created a firewall address object that is used in multiple policy packages for multiple FortiGate devices in an ADOM.

After the installation operation is performed, which IP/netmask will be installed on Remote-Firewall [VDOM1] for the LAN firewall address object?

Options:

A.

21.21.2.5/255.255.255.255

B.

172.16.5.20/255.255.255.255

C.

172.16.5.0/255.255.255.0

D.

10.10.10.5/255.255.255.255

Buy Now
Questions 19

An administrator has a FortiGate-HQ device with VDOMs—root, HR and Facilities, currently managed under the FortiManager ADOM—Site1. They try to move VDOM HR to the FortiManager ADOM—Site2, but it does not work.

Why is the administrator not able to move FortiGate-HQ VDOM HR to FortiManager ADOM—Site2?
Options:

A.

The FortiGate-HQ must be managed under the FortiManager ADOM—root to allow moving its VDOMs to different ADOMs.

B.

The administrator must have full access in the device layer of FortiGate-HQ VDOM-root before they can VDOMs to different ADOMs.

C.

FortiManager must be in ADOM normal mode, which does not allow VDOMs to be managed separately.

D.

The administrator must delete the FortiGate-HQ device from FortiManager and add it again using the Add Device wizard before moving the VDOM.

Buy Now
Exam Code: NSE6_FMG_AD-7.6
Exam Name: Fortinet NSE 6 - FortiManager 7.6 Administrator
Last Update: Oct 3, 2026
Questions: 65
NSE6_FMG_AD-7.6 pdf

NSE6_FMG_AD-7.6 PDF

$21.25  $84.99
NSE6_FMG_AD-7.6 Engine

NSE6_FMG_AD-7.6 Testing Engine

$25  $99.99
NSE6_FMG_AD-7.6 PDF + Engine

NSE6_FMG_AD-7.6 PDF + Testing Engine

$33.75  $134.99