Fortinet NSE 6 - FortiManager 7.6 Administrator
Last Update Sep 23, 2026
Total Questions : 65
Why Choose CramTick
Last Update Sep 23, 2026
Total Questions : 65
Last Update Sep 23, 2026
Total Questions : 65
Customers Passed
Fortinet NSE6_FMG_AD-7.6
Average Score In Real
Exam At Testing Centre
Questions came word by
word from this dump

Try a free demo of our Fortinet NSE6_FMG_AD-7.6 PDF and practice exam software before the purchase to get a closer look at practice questions and answers.

We provide up to 3 months of free after-purchase updates so that you get Fortinet NSE6_FMG_AD-7.6 practice questions of today and not yesterday.

We have a long list of satisfied customers from multiple countries. Our Fortinet NSE6_FMG_AD-7.6 practice questions will certainly assist you to get passing marks on the first attempt.

CramTick offers Fortinet NSE6_FMG_AD-7.6 PDF questions, and web-based and desktop practice tests that are consistently updated.

CramTick has a support team to answer your queries 24/7. Contact us if you face login issues, payment, and download issues. We will entertain you as soon as possible.

Thousands of customers passed the Fortinet Fortinet NSE 6 - FortiManager 7.6 Administrator exam by using our product. We ensure that upon using our exam products, you are satisfied.
An administrator configures a new BGP peer in the FortiManager device-level database of FortiGate. They reinstall the policy package to the managed FortiGate device without any errors. However, when the administrator logs in to FortiGate, they do not see the BGP configuration changes.
What is the most likely reason why FortiManager did not push the BGP peer changes to FortiGate?
Refer to the exhibits.
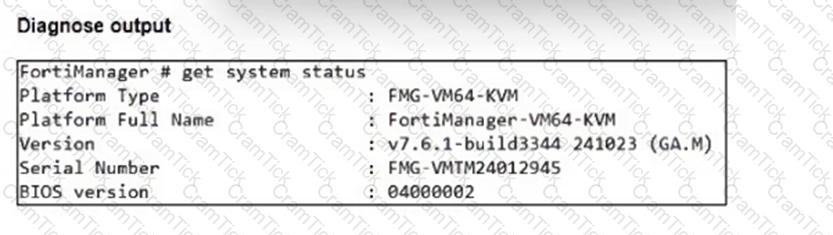
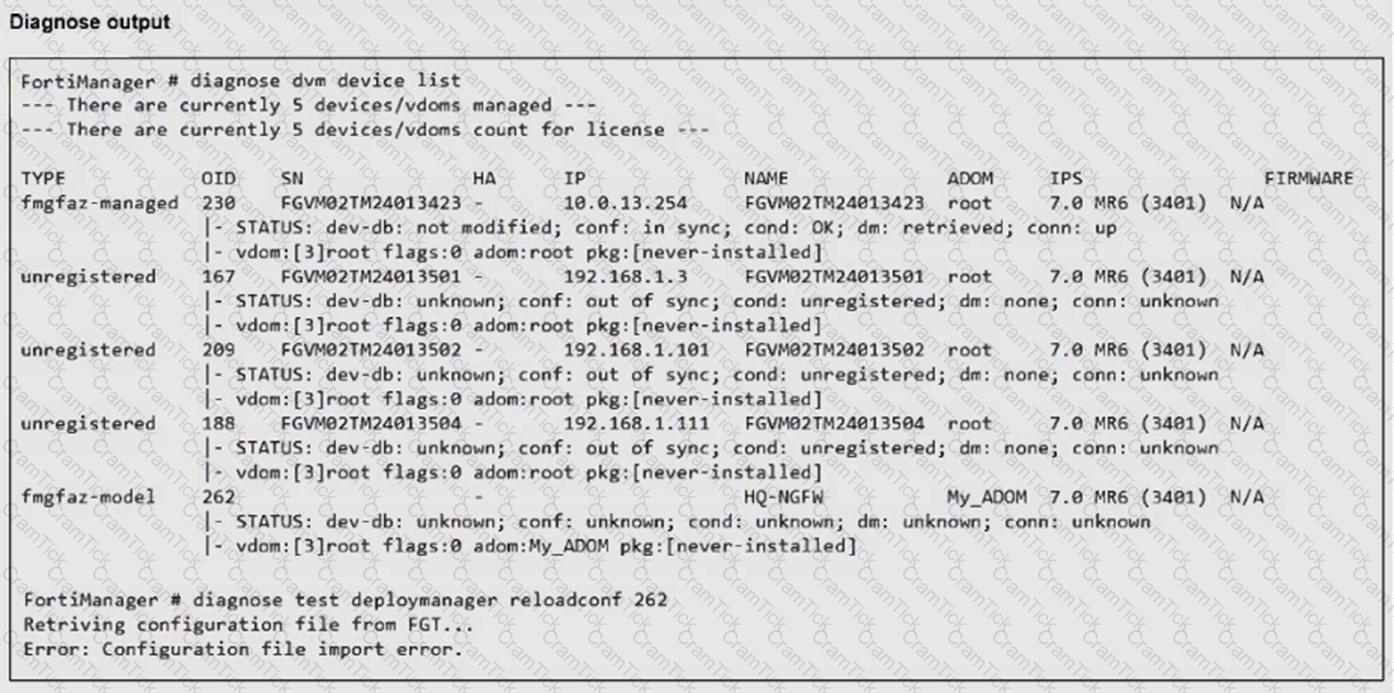
An administrator runs the reload failure command diagnose test deploymanager reloadconf 262 on FortiManager.
Why does the administrator receive an error message?
Refer to the exhibits.
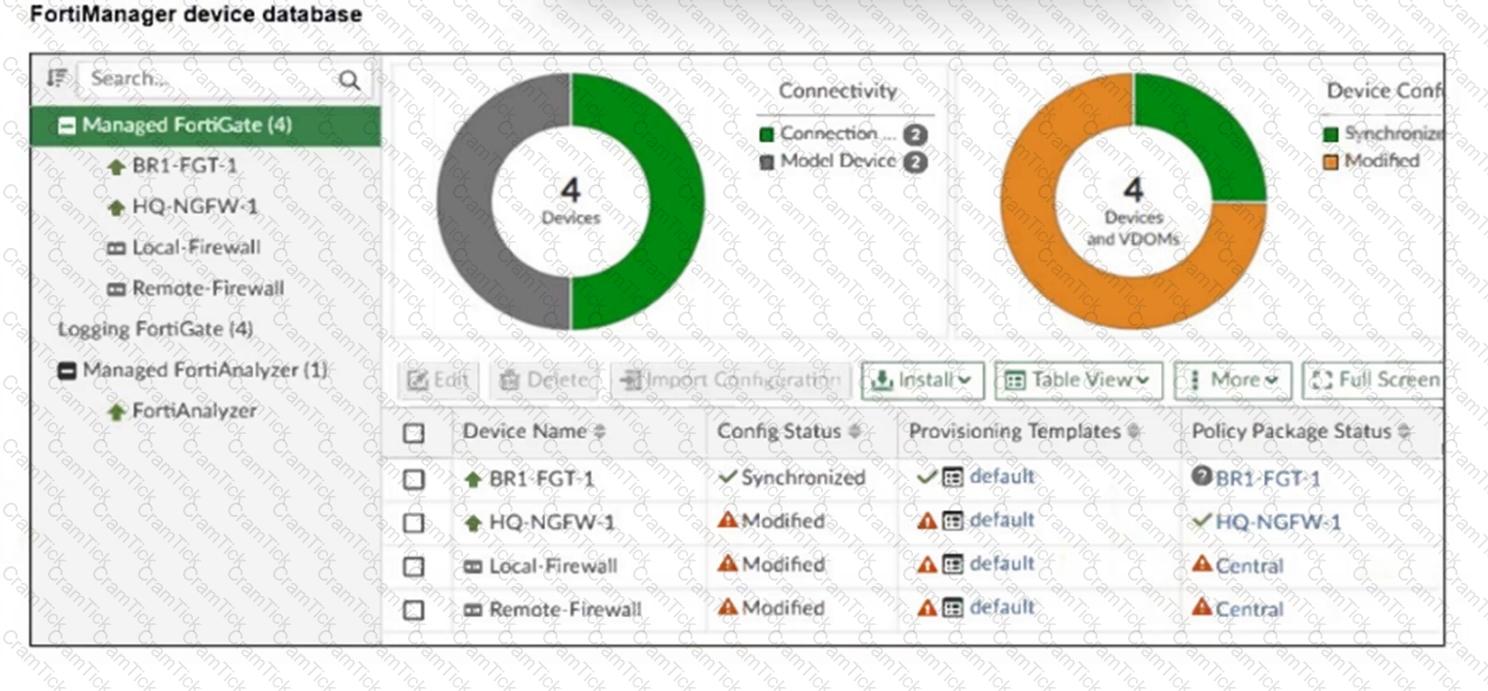
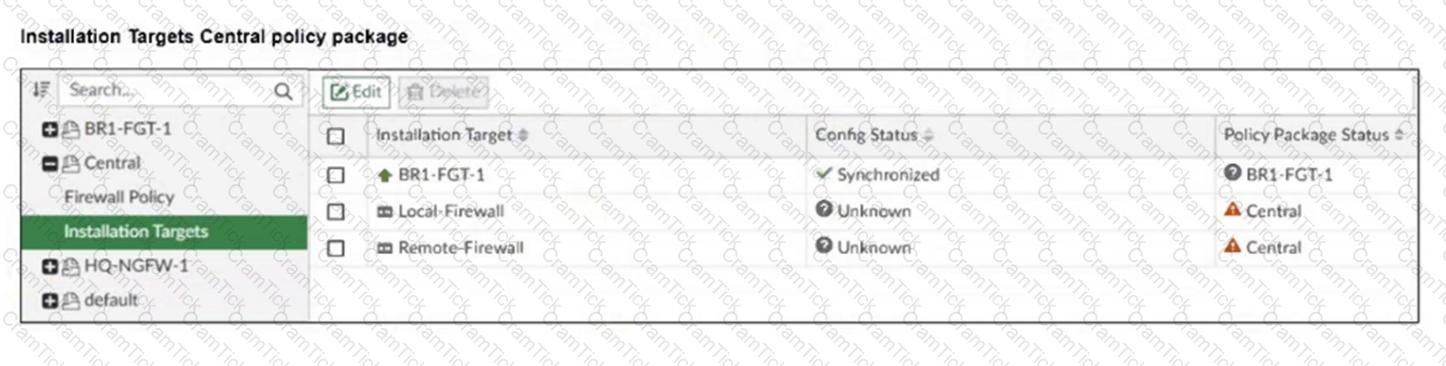
An administrator has been asked to install the same policies from a central policy package onto the BR1-FGT-1 firewall.
The administrator added BR1-FGT-1 as a target in the central policy package installation.
What should the administrator do when reinstalling the central policy package on the BR1-FGT-1 firewall?
TESTED 23 Sep 2026