CompTIA Cybersecurity Analyst CySA+ V4 (New Version)
Last Update Sep 4, 2026
Total Questions : 82
Why Choose CramTick
Last Update Sep 4, 2026
Total Questions : 82
Last Update Sep 4, 2026
Total Questions : 82
Customers Passed
CompTIA CS0-004
Average Score In Real
Exam At Testing Centre
Questions came word by
word from this dump

Try a free demo of our CompTIA CS0-004 PDF and practice exam software before the purchase to get a closer look at practice questions and answers.

We provide up to 3 months of free after-purchase updates so that you get CompTIA CS0-004 practice questions of today and not yesterday.

We have a long list of satisfied customers from multiple countries. Our CompTIA CS0-004 practice questions will certainly assist you to get passing marks on the first attempt.

CramTick offers CompTIA CS0-004 PDF questions, and web-based and desktop practice tests that are consistently updated.

CramTick has a support team to answer your queries 24/7. Contact us if you face login issues, payment, and download issues. We will entertain you as soon as possible.

Thousands of customers passed the CompTIA CompTIA Cybersecurity Analyst CySA+ V4 (New Version) exam by using our product. We ensure that upon using our exam products, you are satisfied.
Which of the following occurs during the analysis phase of the incident response process?
A vulnerability analyst conducts a security assessment on the Remote Desktop Protocol (RDP) security posture within the environment.
The analyst issues the following command for the assessment: nmap -p 3389 --script rdp* 10.0.0.0/24 The analyst receives responses, which are divided into one of the two categories, from 13 out of the 254 hosts:
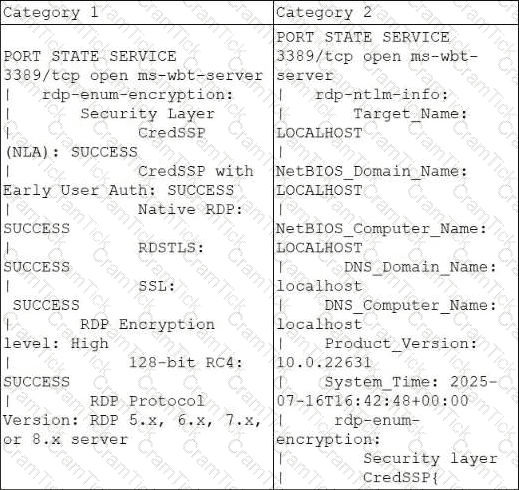
Which of the following conclusions can the analyst make about the output on Category 2?
A security analyst analyzes the output of a web application access log for a company based in the United States.
Given the following output:
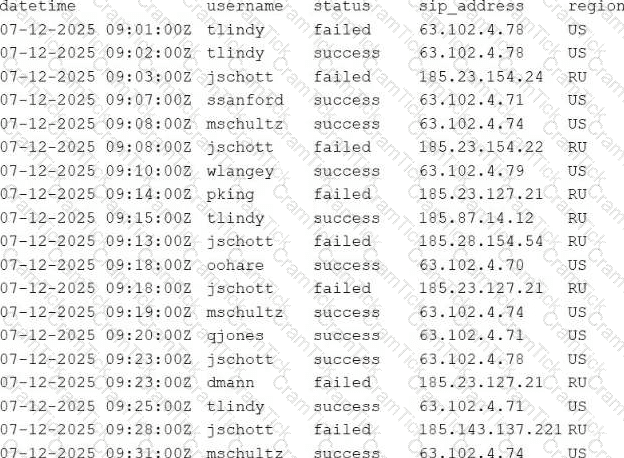
Which of the following users should be investigated first?
TESTED 04 Sep 2026