An internal user enters a client credit card number into an internal generative machine learning (ML) model:
#User prompt: Customer Jane Doe has a new credit card that she wants to add to her account. The number is 5555-5555-5555-5555
Which of the following is the most effective way to prevent prompt injection attacks against a large language model (LLM)?
A social media company with more than a million lines of code wants to reduce the mean time to fix bugs and issues.
Which of the following is the most balanced AI strategy to automate the vulnerability management flow?
A security administrator must implement security controls for AI systems.
Which of the following access controls should the administrator set up first for authentication?
During a model validation procedure, an engineer notices that a model performs well during training but poorly during testing.
Which of the following best describes the reason?
A threat intelligence team wants to automate the analysis and summary of its in-depth reports for multiple target audiences. Which of the following is the best solution?
A global security operations center (SOC) wants to adapt and leverage the strength of AI in order to enhance its security operations.
Which of the following is the best way to enhance the global SOC functions?
Which of the following responsible AI standards refers to a principle that clearly states the reasons behind the decisions for a particular conclusion?
An architect is creating a threat model for an agentic system.
Which of the following should the architect do first?
A group of security engineers is developing a SIEM system that will be able to ingest data from multiple structured and unstructured sources, have a chatbot integrated with an LLM that the security analyst can interact with, and provide insights from the SIEM alert data.
Which of the following techniques should the security engineers consider before collecting the data from the respective sources?
A security analyst needs to conduct a security assessment of the output from an AI-enabled development tool.
Which of the following should the analyst do first?
A penetration tester is assessing the controls of a deployed AI system that is designed to search and return the contents of files.
The tester runs the following:
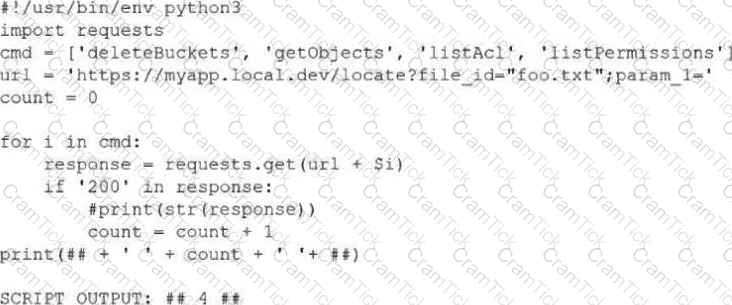
Which of the following is the best control to prevent abuse of the system?
A critical AI system cannot be shut down and must remain secure. Which of the following actions should be performed to apply controls?
A cybersecurity administrator generates patching reports using AI, but the process takes a long time. Which of the following is the best way to increase performance?
A team of engineers builds an application using a large language model (LLM). The application is built on Linux and is hosted on a virtual server. Users must create an account in order to access and use the platform.
Which of the following should the team do to protect the account credentials?
An IT company implements an adaptable chatbot that learns from user prompts. Based on the conversation shown — where User 2 injected false information about a company acquisition that caused the chatbot to give incorrect responses to User 3 — which of the following compensating controls should an administrator implement to mitigate the issue?
Which of the following describes the most significant risk associated with AI agents that make autonomous decisions?
Which of the following is the primary security risk when deploying AI models in production?
User experience is declining since the launch of a large language model (LLM) in internal networks.
Which of the following should be the highest priority for the prompt engineers?
A large number of employees receive a video message in which the company ' s CEO states that the company will be filing for bankruptcy. After an investigation, it was discovered that the CEO did not send this message.
Which of the following is this scenario an example of?
A cybersecurity analyst must use pattern recognition on a data set containing unstructured data.
Which of the following models is the best for this task?
An organization wants to reduce vulnerabilities after deployment. The organization decides to incorporate an AI-assisted early detection and vulnerability identification process in its development workflow.
Which of the following AI-assisted functions is the best option?
A recently deployed AI system becomes persistently unavailable. A restart temporarily fixes the issue, but the issue happens again. Upon examination of API logs, an analyst finds that external calls continued to use system resources after the action completed.
Which of the following is the best way to improve availability of the system?
An organization deploys a browser-based AI plug-in to detect malicious websites and phishing links in corporate email.
Which of the following techniques is used in this AI plug-in?
Customer feedback for an AI chatbot has a high-rate of non-answers, which is causing higher central processing unit (CPU) utilization.
Which of the following should be implemented?
A company is adopting AI and wants to create policies and procedures that include a structure for evaluating, publishing, and approving patterns for AI usage.
Which of the following should the company establish to meet this goal?
Which of the following would most likely be used to prove that an image is AI generated?
An AI security architect needs to conduct a security review of a new AI chatbot. Which of the following resources would the architect most likely rely on to perform a threat assessment and ensure comprehensive coverage during the review?
An AI security administrator notices that the information referenced by the model is incorrectly formatted and missing values.
Which of the following job roles would most likely be responsible for correcting this error?
A data set containing medical information is put into a machine learning (ML) model that is designed to predict specific illnesses for a population. In the process of verifying the reliability of the system, the compliance officer realizes that the system cannot reliably predict illnesses for certain segments of the population.
Which of the following types of risk is most applicable to this case?
A security consultant must summarize the impact of posture management on a machine learning (ML) use case.
Which of the following is the most appropriate reference for this purpose?
Which of the following resources most accurately covers the most widely recognized threat vectors and common vulnerabilities related to large language model (LLM) applications?
Which of the following should an auditor reference when reviewing a company ' s human resources AI systems for legal non-compliance?
A line of business wants to onboard an application that uses a custom AI model for employee assessments. The Chief Information Officer (CIO) agrees to allow the engagement to proceed but first wants a threat model.
Which of the following is the most appropriate to use for an AI threat model?
An attacker successfully completes a denial-of-service (DoS) attack through the context window of an AI system. Thousands of characters are obfuscated and hidden behind an emoji.
Which of the following techniques best mitigates this type of attack?
As a compliance requirement, a large language model (LLM) application requires setting up guardrails.
Which of the following resources is most appropriate to use?
Which of the following controls is the best way to mitigate a denial-of-service (DoS) attack?
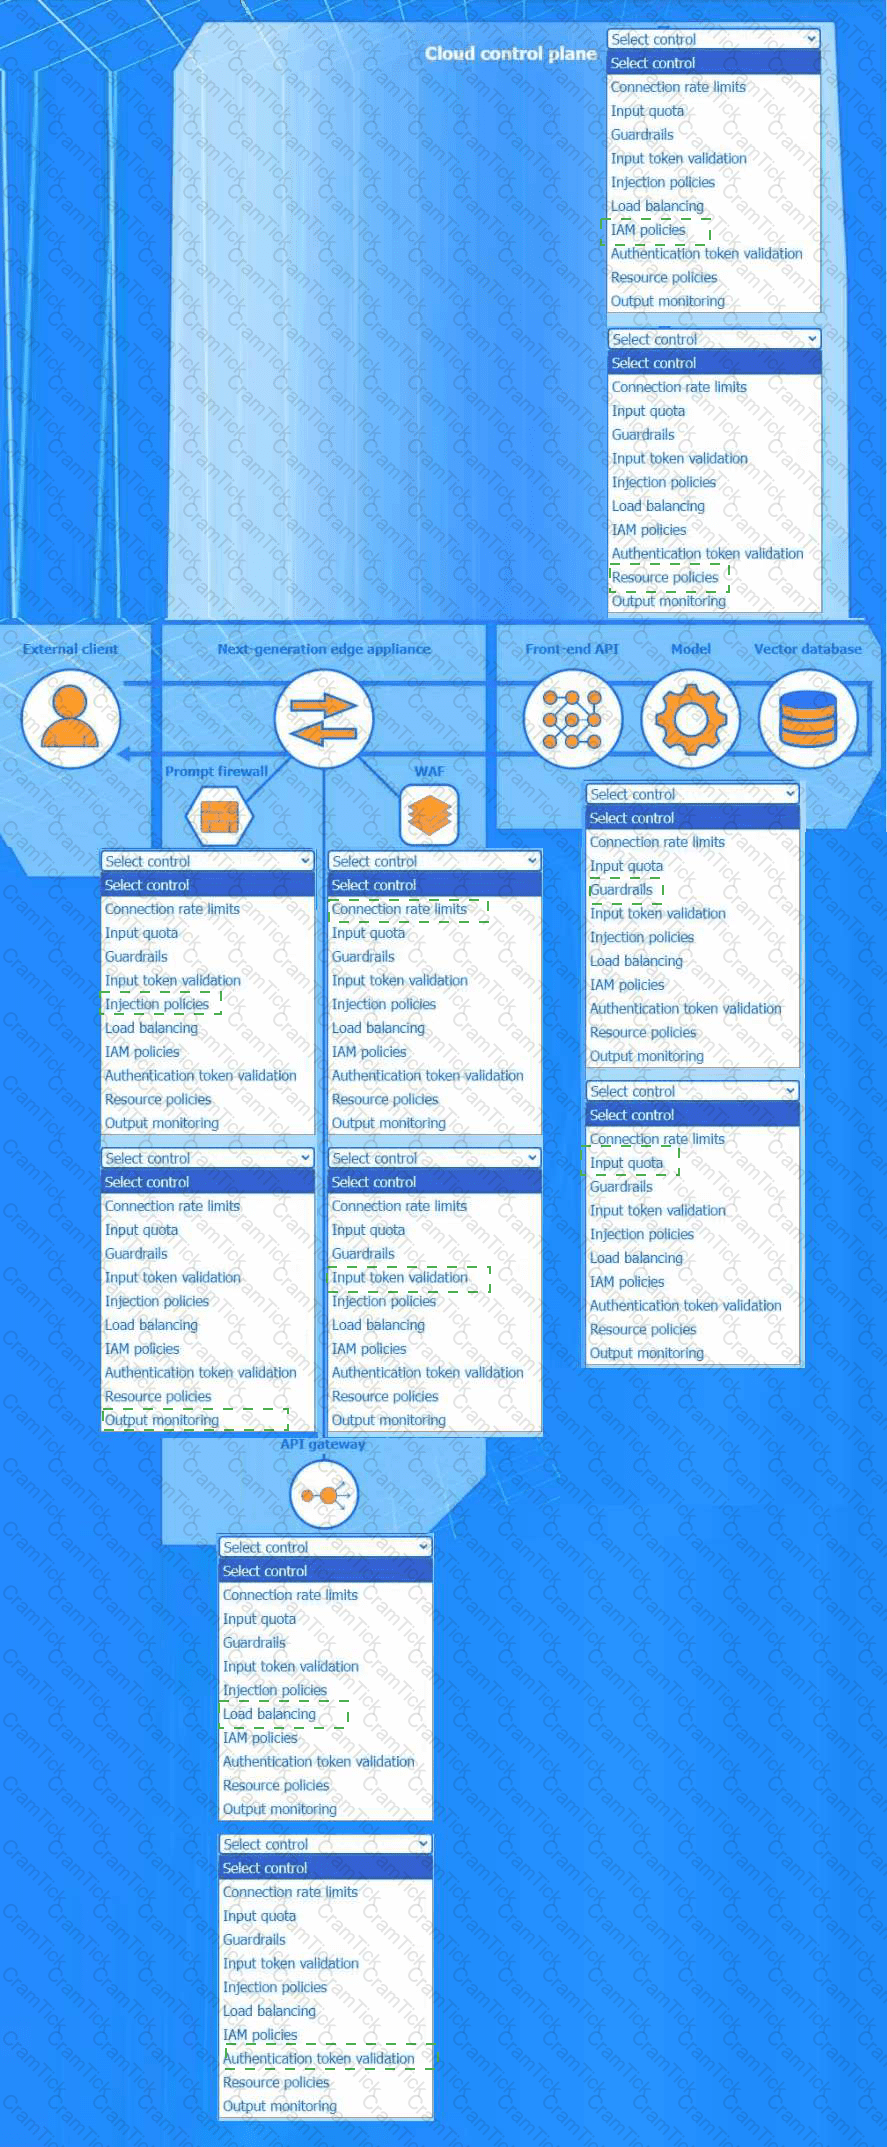
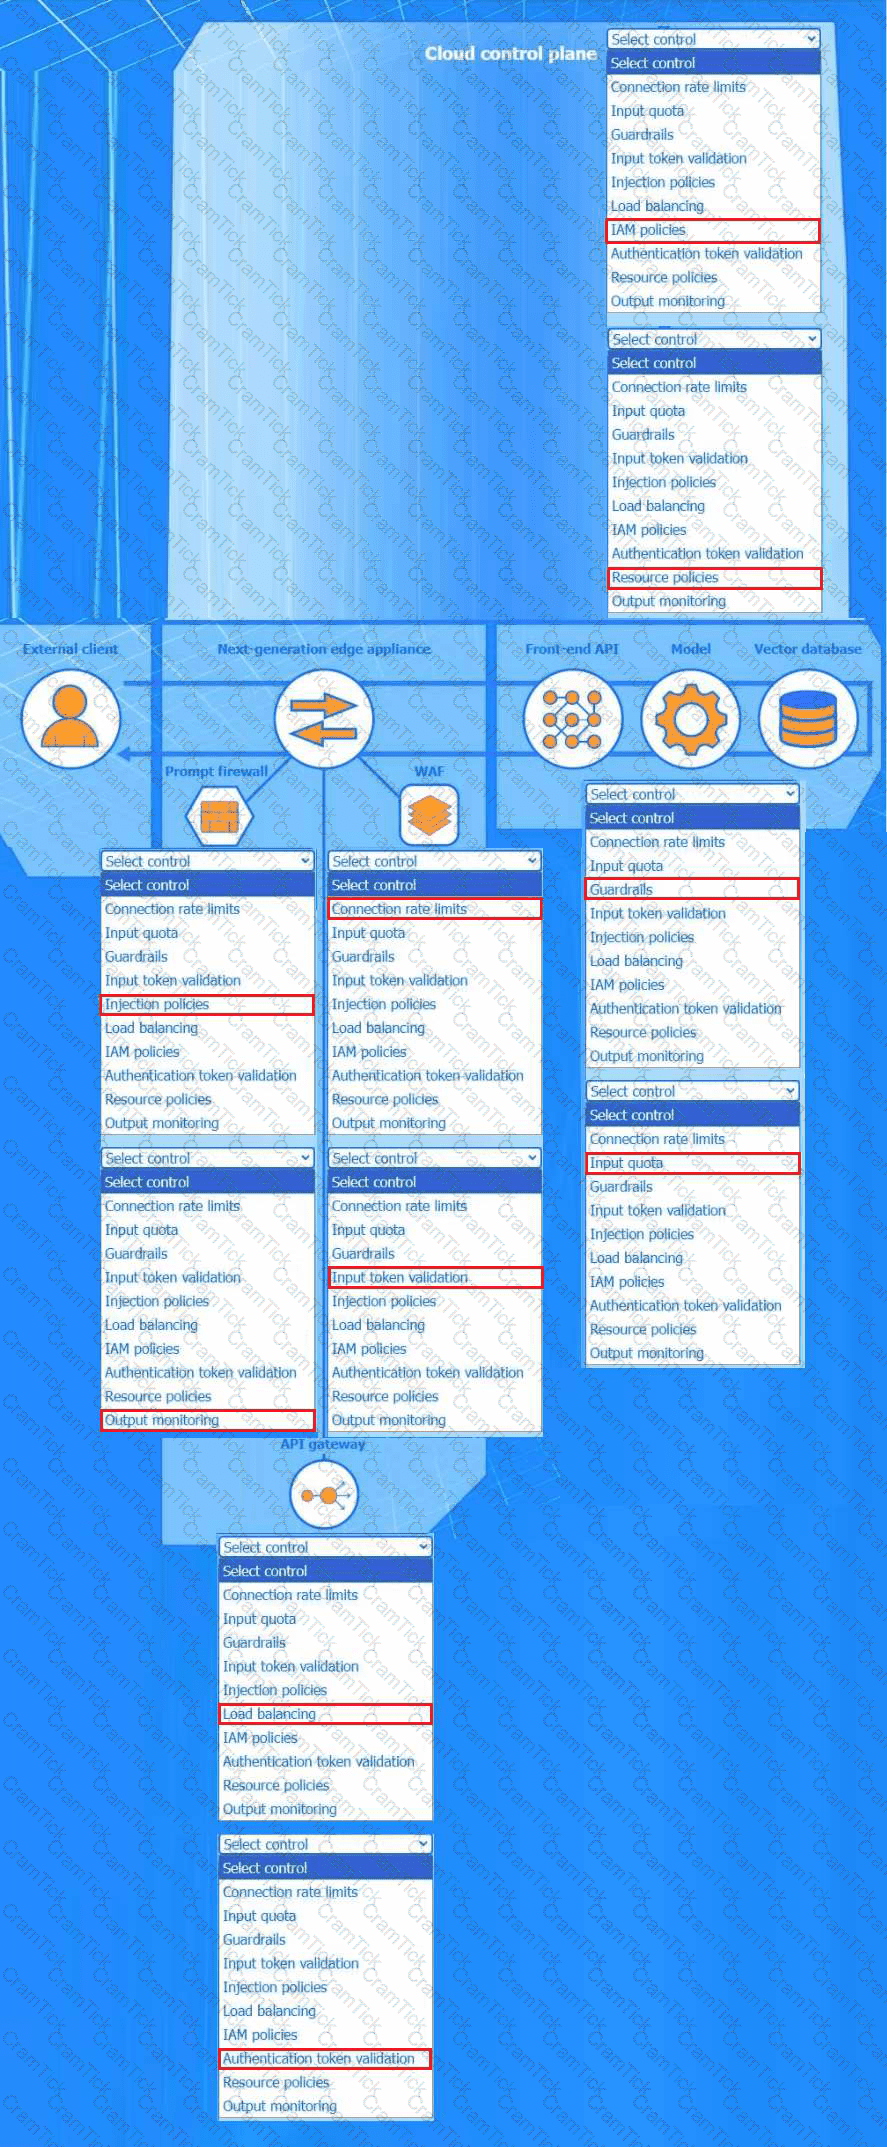
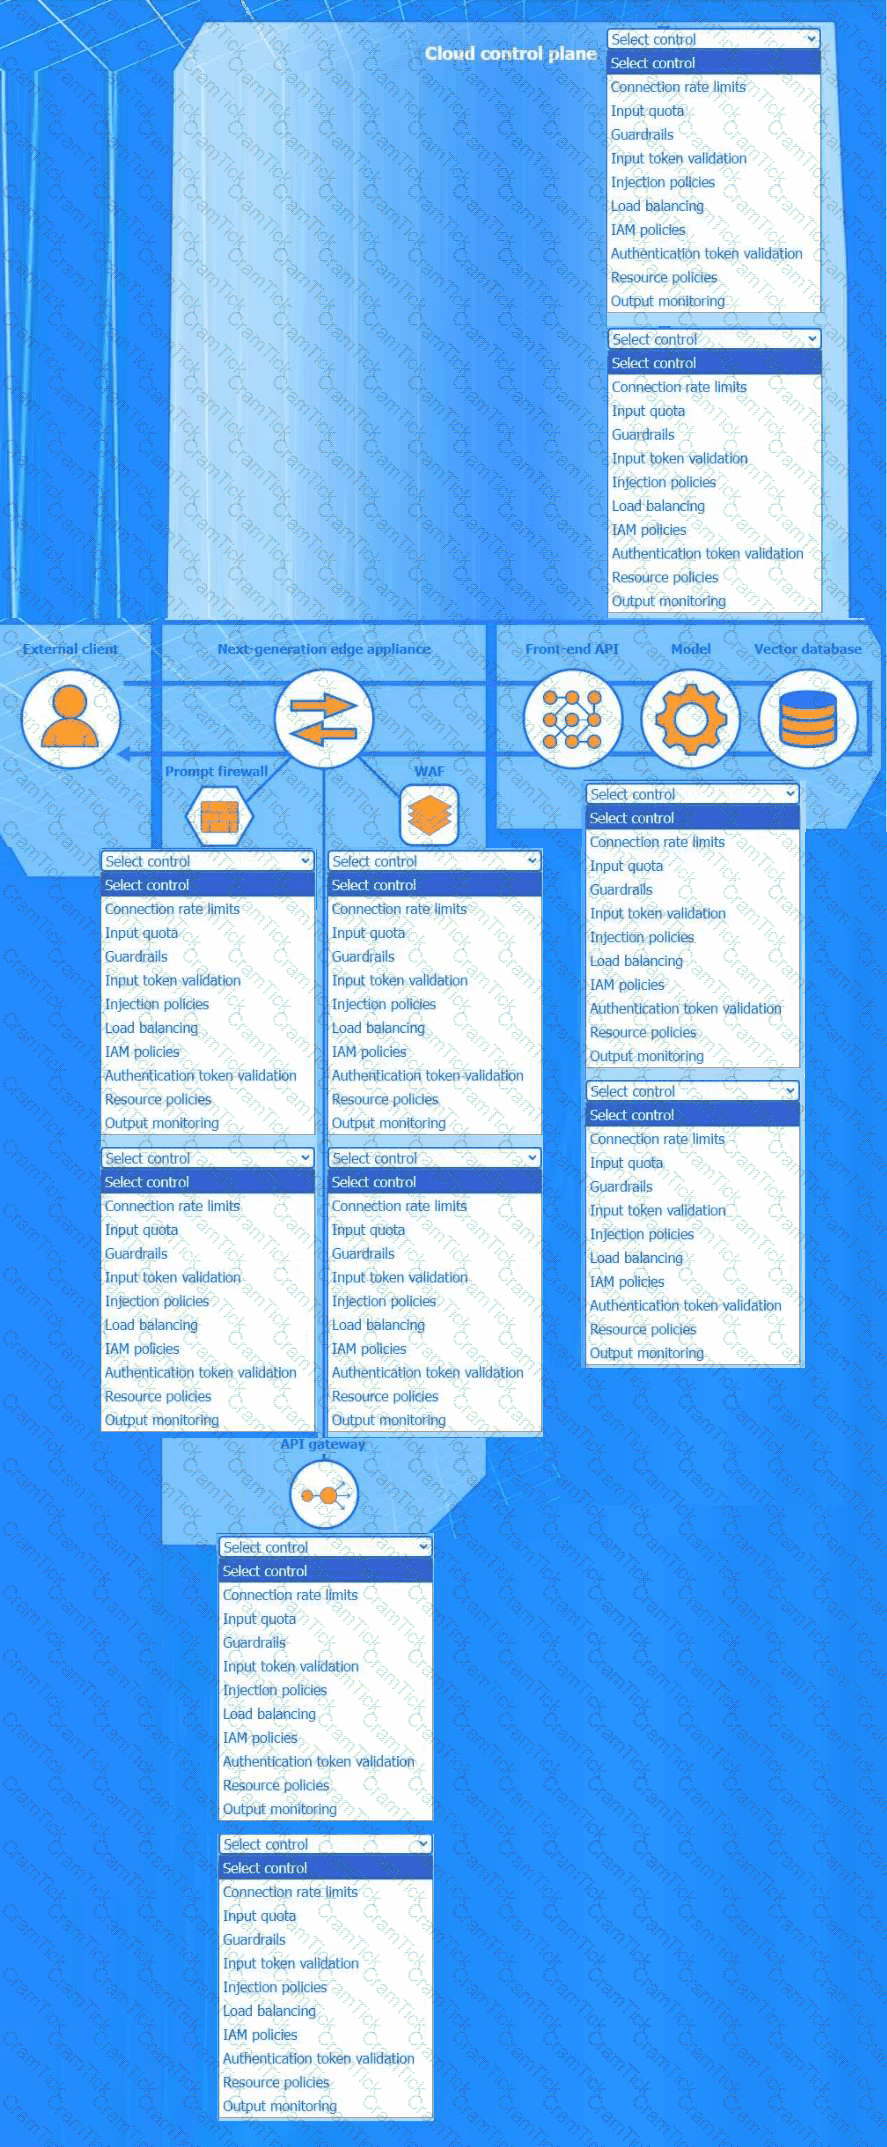
Instructions: Use the drop-down menus to define two appropriate security controls for each component of the AI system. Each control may be used only once.
An engineer is deploying a new AI system and wants to integrate it into the core system through an API.
A security analyst is aware of an active penetration test in the environment. The analyst examines SIEM log data and notices the following AI system output:
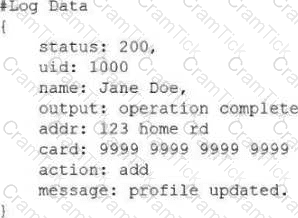
Which of the following is the vulnerability that has occurred and the control the analyst should implement?
A company introduces a large language model (LLM) in an application in order to monitor for a potential denial-of-service attack. Which of the following should the company use to measure the utilization of the LLM?
A multinational company wants to implement an AI-assisted job screening solution.
Which of the following should the company reference to reduce the risk of incurring compliance-related fines?
Which of the following is the primary purpose of validating data for an AI system?
TESTED 05 Oct 2026