Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: fifty75ct

NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Questions 4

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

Options:

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN

B.

IGMP reports on the VLAN are forwarded to all switch ports.

C.

The setting can only be enabled using the FortiSwitch CLI.

D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.

Buy Now
Questions 5

An administrator needs to deploy managed FortiSwitch devices in a remote location where multiple VLANs must be utilized to segment devices. No Layer 3 switch or router is present. The the only WAN connectivity is the router provided by the ISP connected to the public internet.

Which two items will the administrator need to use? (Choose two.)

Options:

A.

A FortiSwitch interface connected to the ISP router configured with fortilink-13-mode enabled.

B.

FortiSwitch and FortiGate devices configured with VXLAN interfaces.

C.

FortiSwitch devices configured with NAT disabled.

D.

FortiSwitch devices that have the required internal hardware for this configuration.

E.

FortiSwitch and FortiGate devices configured with IPsec interfaces.

Buy Now
Questions 6

What happens if FortiSwitch fails to discover either FortiEdge Cloud or a FortiGate with FortiLink?

Options:

A.

It switches to FortiLink mode by default.

B.

It remains in local management mode.

C.

It requires manual reimaging.

D.

It disables auto-network.

Buy Now
Questions 7

What can an administrator do to maintain a FortiGate-compatible FortiSwitch configuration when changing the management mode from standalone to FortiLinK?

Options:

A.

Use a migration tool based on Python script to convert the configuration.

B.

Enable the FortiLink setting on FortiSwitch before the authorization process.

C.

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

D.

Register FortiSwitch to FortiSwitch Cloud to save a copy before managing with FortiGate.

Buy Now
Questions 8

Which statement about the quarantine VLAN on FortiSwitch is true?

Options:

A.

Quarantine VLAN has no DHCP server

B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.

C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.

D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.

Buy Now
Questions 9

Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)

Options:

A.

Configure a native VLAN on the FortiLink

B.

Assign an IP address and subnet mask to FortiSwitch VLANs

C.

Only assign one native VLAN on a port

D.

Assign untagged VLANs using FortiGate CLI

Buy Now
Questions 10

Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?

Options:

A.

SPAN

B.

Sniffer profile

C.

sFlow

D.

TCP dump

Buy Now
Questions 11

On supported FortiSwitch models, which access control list (ACL) stage is recommended for applying actions before the switch performs any layer 2 or layer 3 processing? (Choose one answer)

Options:

A.

Ingress

B.

Forwarding

C.

Egress

D.

Prelookup

Buy Now
Questions 12

How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?

Options:

A.

Only high-end FortiSwitch models support ACL.

B.

ACL can be used only at the prelookup stage in the traffic processing pipeline.

C.

Classifiers enable matching traffic based only on the VLAN ID.

D.

FortiSwitch checks ACL policies only from top to bottom.

Buy Now
Questions 13

(Full question statement start from here)

You are deploying a FortiSwitch virtual stack in a network that contains Cisco devices. You want the Cisco devices toautomatically discover the FortiSwitch devices and exchange device information. Which two protocols must be enabled on the FortiSwitch devices to achieve this? (Choose two answers)

Options:

A.

Unidirectional Link Detection

B.

Cisco Discovery Protocol

C.

Link Layer Discovery Protocol

D.

LLDP – Media Endpoint Discovery

Buy Now
Questions 14

Which LLDP-MED Type-Length-Values does FortiSwitch collect from endpoints to track network devices and determine their characteristics?

Options:

A.

Network policy

B.

Power management

C.

Location

D.

Inventory management

Buy Now
Questions 15

Which QoS mechanism maps packets with specific CoS or DSCP markings to an egress queue?

Options:

A.

Queuing for egress traffic

B.

Classification for ingress traffic

C.

Rate limiting for egress traffic

D.

Marking for ingress traffic

Buy Now
Questions 16

(Full question statement start from here)

What is one key advantage of using a sniffer profile on FortiSwitch compared to using the sniffer command? (Choose one answer)

Options:

A.

It allows packet capture on all switch ports without limitations.

B.

It eliminates the need to use access control lists (ACLs) or port mirroring for analysis.

C.

It automatically filters irrelevant traffic types.

D.

It automatically decrypts SSL/TLS traffic for full packet inspection.

Buy Now
Questions 17

How does FortiGate handle configuration of flow tracking sampling if you export the settings to a managed FortiSwitch stack with sampling mode set to perimeter is true?

Options:

A.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces.

B.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces, except ICL and ISL interfaces.

C.

FortiGate configures and enables flow sampling on FortiSwitch but does not change existing sampling settings of interfaces.

D.

FortiGate configures and enables egress sampling on all management interfaces.

Buy Now
Questions 18

You need to deploy routing on a standalone FortiSwitch and want to maximize routing performance. Which type of routing is best for this deployment? (Choose one answer)

Options:

A.

Hardware-based routing because it relies on ASIC for faster performance1

B.

Software-based routing because it bypasses the CPU to increase routing speed

C.

Hardware-based routing because the routing is performed directly by the kernel

D.

Software-based routing because it is preferred for high-speed backbone networks

Buy Now
Questions 19

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

Options:

A.

Use a migration tool based on python script to convert the configuration

B.

Enable the Forti-link setting on FortiSwitch before the authorization process

C.

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.

D.

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.

Buy Now
Questions 20

To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?

Options:

A.

Network policy

B.

Inventory management

C.

Location

D.

Power management

Buy Now
Questions 21

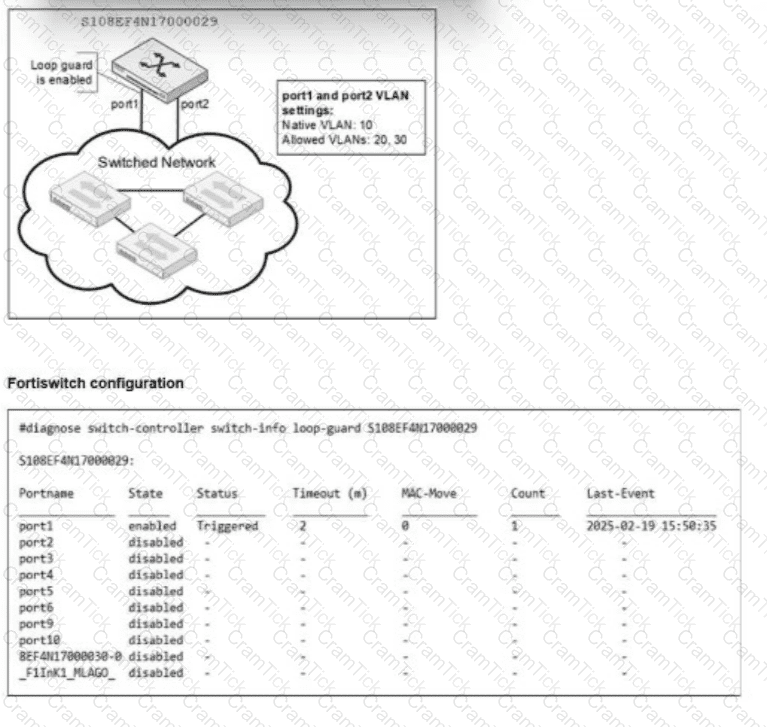
Refer to the exhibits.

You are reviewing a FortiSwitch configuration where port1 and port2 are connected to a switched network. Loop guard is enabled on port1.

The CLI output shows that the port1 status is triggered due to loop guard. Which two conditions could have caused this shutdown? (Choose two.)

Options:

A.

A loop guard frame sent from port1 is received on port2.

B.

A loop guard frame sent from port1 is received back on port1.

C.

Loop guard is triggered because port2 did not send any bridge protocol data units (BPDU).

D.

Loop guard is triggered because the port detected excessive traffic.

Buy Now
Questions 22

What type of multimode transceiver can be used to split a 40G port?

Options:

A.

QSFP+ transceiver

B.

SFP transceiver

C.

QSFP transceiver

D.

SFP+ transceiver

Buy Now
Questions 23

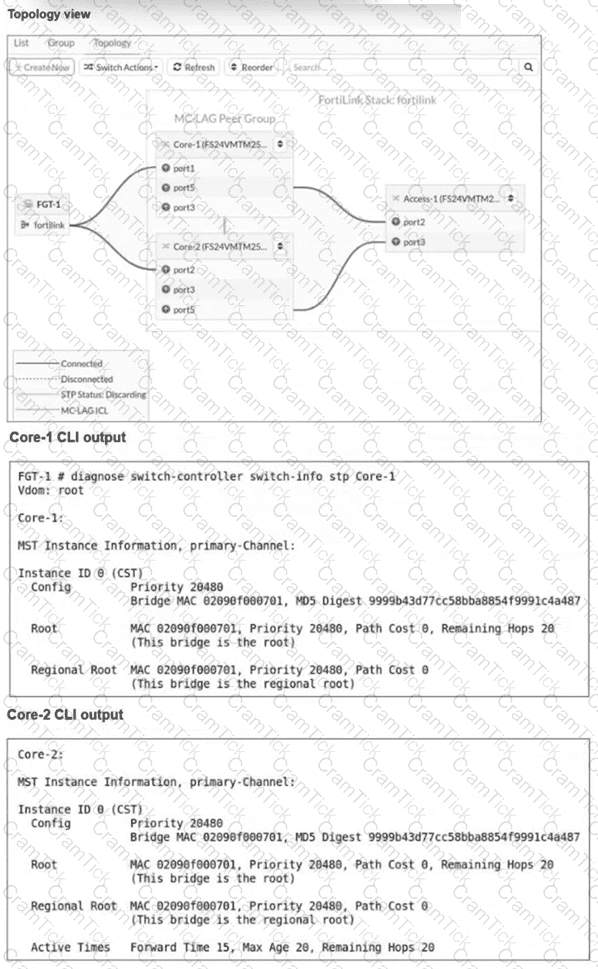
Refer to the exhibits.

An administrator has deployed two FortiSwitch devices, Core-1 and Core-2, as multichassis link aggregation group (MCLAG) peers. These switches are connected to FortiGate for FortiLink and to an access switch (Access-1) using an inter-switch link (ISL). After configuration, the administrator notices that both Core-1 and Core-2 are claiming to be the root bridge in the Multiple Spanning Tree Protocol (MSTP) topology. What explains this behavior? (Choose one answer)

Options:

A.

FortiGate participates in MSTP and causes both switches to assume the root bridge role.

B.

The ISL was not configured correctly, leading to MSTP inconsistency.

C.

Both switches share the same bridge ID because MCLAG treats them as one logical switch.

D.

MCLAG automatically disables STP on all peer switches.

Buy Now
Questions 24

Which two types of Layer 3 interfaces can participate in dynamic routing on FortiSwitch? (Choose two.)

Options:

A.

Detected management interfaces

B.

Loopback interfaces

C.

Switch virtual interfaces

D.

Physical interfaces

Buy Now
Questions 25

Exhibit.

port1 and port2 are the only ports configured with the same native VLAN 10.

What are two reasons that can trigger port1 to shut down? (Choose two.)

Options:

A.

port1 was shut down by loop guard protection.

B.

STP triggered a loop and applied loop guard protection on port1.

C.

An endpoint sent a BPDU on port1 that it received from another interface.

D.

Loop guard frame sourced from port1 was received on port1.

Buy Now
Questions 26

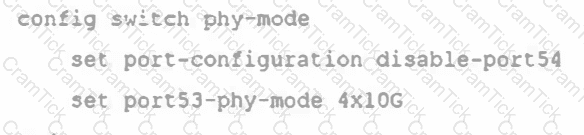
Exhibit.

What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces.

B.

The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.

C.

The port full speed prior the split was 100G SFP+

D.

The split port can be assigned to native VLAN

Buy Now
Questions 27

You are configuring FortiSwitch to perform layer 3 inter-VLAN routing while managed by FortiGate over FortiLink. On supported hardware models, FortiSwitch can offload routing decisions for better performance.1How does FortiSwitch perform routing between VLANs? (Choose one answer)

Options:

A.

By using a hardware forwarding table (FIB) programmed into ASIC.

B.

By supporting only dynamic routing protocols in hardware.

C.

By disabling routing when managed by FortiGate.

D.

By relying entirely on the CPU in software.

Buy Now
Questions 28

Which statement about the use of the switch port analyzer (SPAN) packet capture method is true?

Options:

A.

Mirrored traffic can be sent across multiple switches.

B.

SPAN can be configured only on a standalone FortiSwitch.

C.

Traffic on the management interface can be mirrored and captured by the monitoring device.

D.

The monitoring device must be connected to the same switch where the traffic is being mirrored

Buy Now
Questions 29

Which statement about the configuration of VLANs on a managed FortiSwitch port is true?

Options:

A.

Untagged VLANs must be part of the allowed VLANs: ingress and egress.

B.

FortiSwitch VLAN interfaces are created only when FortiSwitch is managed by Forti-Gate.

C.

The native VLAN is implicitly part of the allowed VLAN on the port.

D.

Allowed VLANS expand the collision domain to the port.

Buy Now
Questions 30

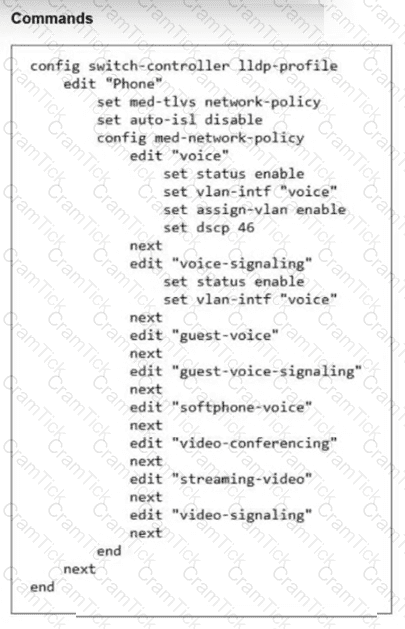
Refer to the exhibit.

The LLDP profile shown in the exhibit was configured to detect IP phones and automatically assign them to the appropriate VLAN. You apply this LLDP profile on a FortiSwitch port. Which configuration should you enable on the FortiSwitch profile to collect detailed information about all the connected IP phones? (Choose one answer)

Options:

A.

Create a new LLDP profile to handle different LLDP-MED TLVs.

B.

Configure a dedicated voice VLAN with DSCP 46.

C.

Enable LLDP-MED inventory management TLVs.

D.

Enable auto-isl.

Buy Now
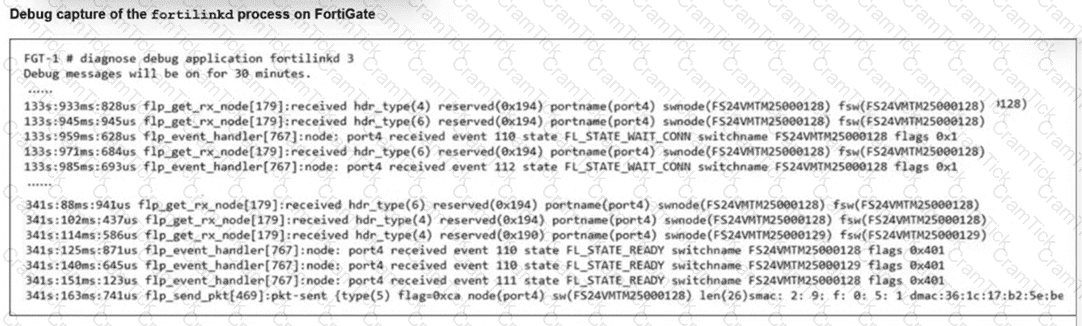
Questions 31

Refer to the exhibit.

A periodic heartbeat message sent from a managed FortiSwitch and corresponding acknowledgments from FortiGate is shown. What does this behavior indicate? (Choose one answer)

Options:

A.

The FortiLink connection between FortiGate and FortiSwitch is healthy and active.

B.

FortiGate is unable to establish a FortiLink session with FortiSwitch.

C.

FortiSwitch is expecting an authorization from FortiGate.

D.

FortiSwitch has not been authorized yet.

Buy Now
Questions 32

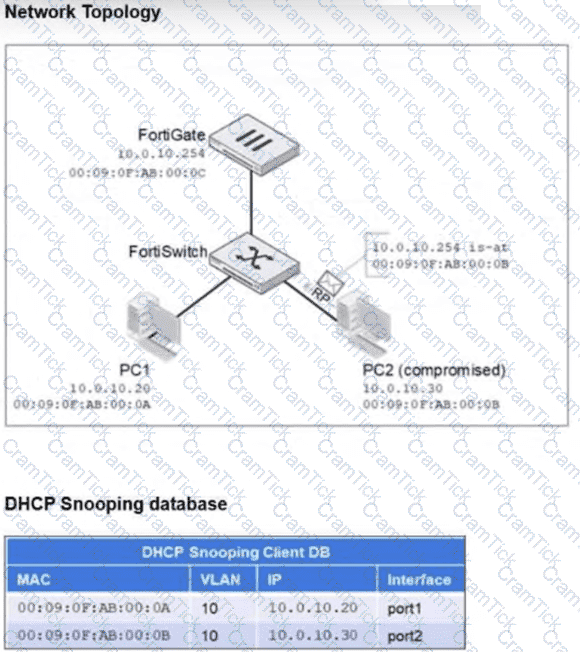
Refer to the exhibits.

All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)

Options:

A.

Forward the ARP replies because there are no IPSG bindings blocking them.

B.

Accept the ARP replies because the VLAN has DAI enabled and FortiGate is a trusted DHCP server.

C.

Forward the ARP replies to all VLAN 10 ports because DAI is only active on trusted ports.

D.

Drop the ARP replies because they fail DAI validation against the DHCP snooping database.

Buy Now
Questions 33

Refer to the configuration:

Which two conditions does FortiSwitch need to meet to successfully configure the options shown in the exhibit above? (Choose two.)
Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces

B.

FortiSwitch would need to be rebooted.

C.

The split port can be assigned to a native VLAN.

D.

The Dort full speed prior to the split was 100G QSFP+.

Buy Now
Questions 34

How is traffic routed on FortiSwitch?

Options:

A.

Hardware-based routing on FortiSwitch is handled by the CPU.

B.

FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).

C.

ASIC hardware routing can only handle dynamic routing, if supported.

D.

Layer 3 routing can be configured on FortiSwitch, while managed by FortiGate.

Buy Now
Exam Code: NSE5_FSW_AD-7.6
Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Last Update: Oct 3, 2026
Questions: 114
NSE5_FSW_AD-7.6 pdf

NSE5_FSW_AD-7.6 PDF

$21.25  $84.99
NSE5_FSW_AD-7.6 Engine

NSE5_FSW_AD-7.6 Testing Engine

$25  $99.99
NSE5_FSW_AD-7.6 PDF + Engine

NSE5_FSW_AD-7.6 PDF + Testing Engine

$33.75  $134.99