Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: fifty75ct

NSE6_FNC_AD-7.6 Fortinet NSE 6 - FortiNAC-F 7.6 Administrator Questions and Answers

Questions 4

When managing multiple FortiNAC-F CAs with a FortiNAC-F Manager, how is endpoint information updated in the FortiNAC-F Manager database?

Options:

A.

Endpoint information is pulled from the managed CAs by the FortiNAC-F Manager at a set interval.

B.

Endpoint information is updated in real time when a host status changes.

C.

Endpoint information is updated when an administrator synchronizes with each CA.

D.

Endpoint information is pushed to the FortiNAC-F Manager based on an administratively configured scheduled task.

Buy Now
Questions 5

Which two actions must the administrator perform to allow FortiNAC-F to process incoming syslog messages from an unknown vendor? (Choose two answers)

Options:

A.

The device must be added as a server in the Host view

B.

The device sending the messages must be modeled in the Network Inventory view

C.

The device must be added as a log receiver in FortiNAC-F

D.

The device must have an event parser created for it

Buy Now
Questions 6

An administrator is configuring FortiNAC-F to manage FortiGate VPN users. As part of the configuration, the administrator must configure a few FortiGate firewall policies. What is the purpose of the FortiGate firewall policy that applies to clients not yet authorized by FortiNAC-F? (Choose one answer)

Options:

A.

To allow access to only the production DNS server

B.

To allow access to only the production DNS server

C.

To allow access to only the FortiNAC-F VPN interface

D.

To allow access to only the FortiGate VPN interface

Buy Now
Questions 7

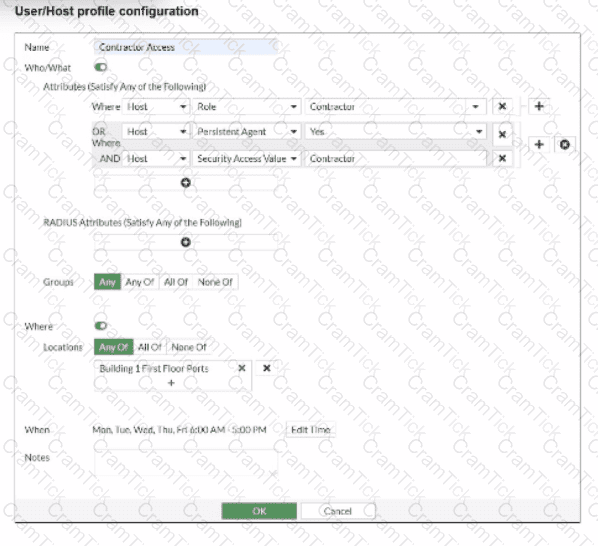
Refer to the exhibit.

If a host is connected to a port in the Building 1 First Floor Ports group, what must also be true to match this user/host profile?

Options:

A.

The host must have a role value of contractor, an installed persistent agent or a security access value of contractor, and be connected between 6 AM and 5 PM.

B.

The host must have a role value of contractor or an installed persistent agent, a security access value of contractor, and be connected between 9 AM and 5 PM.

C.

The host must have a role value of contractor or an installed persistent agent or a security access value of contractor, and be connected between 6 AM and 5 PM.

D.

The host must have a role value of contractor or an installed persistent agent and a security access value of contractor, and be connected between 6 AM and 5 PM.

Buy Now
Questions 8

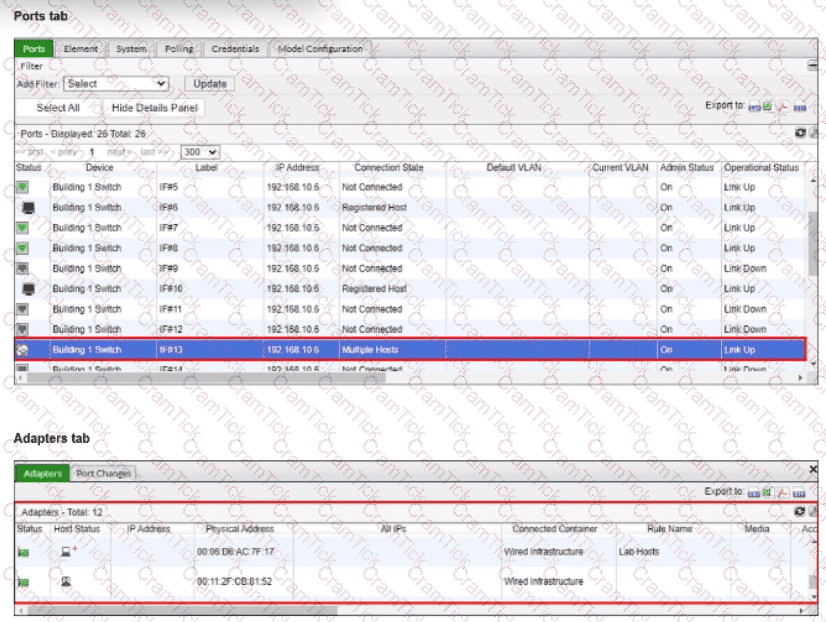
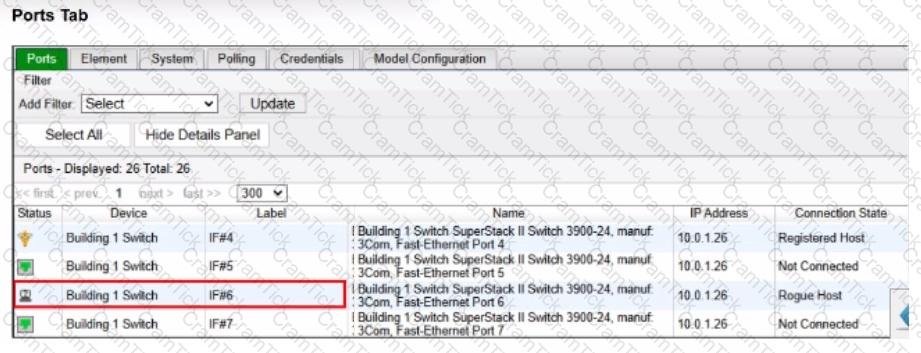
Refer to the exhibits.

What would happen if the highlighted port with connected hosts was placed in both the Forced Registration and Forced Remediation port groups?

Options:

A.

Both types of enforcement would be applied

B.

Enforcement would be applied only to rogue hosts

C.

Multiple enforcement groups could not contain the same port.

D.

Only the higher ranked enforcement group would be applied.

Buy Now
Questions 9

When configuring isolation networks in the configuration wizard, why does a layer 3 network typo allow for mora than ono DHCP scope for each isolation network typo?

Options:

A.

The layer 3 network type allows for one scope for each possible host status.

B.

Configuring more than one DHCP scope allows for DHCP server redundancy

C.

There can be more than one isolation network of each type

D.

Any scopes beyond the first scope are used if the initial scope runs out of IP addresses.

Buy Now
Questions 10

A user was attempting to register their host through the registration captive portal. After successfully registering, the host remained in the registration VLAN. Which two conditions would cause this behavior? (Choose two.)

Options:

A.

The wrong agent s installed.

B.

There is no agent installed on the host.

C.

The port default VLAN is the same as the Registration VLAN.

D.

There is another unregistered host on the same port

Buy Now
Questions 11

Which two statements are true about integrating a third-party device using SNMP traps from that device as input to generate an event? (Choose two.)

Options:

A.

The sending device must be modeled in the inventory topology.

B.

The sending device must support SNMPv3.

C.

set allowaccess snmp must be configured using the CLI on the FortiNAC-F receiving interface.

D.

The IP address OID and MAC address OID must be configured in the trap MIB file.

Buy Now
Questions 12

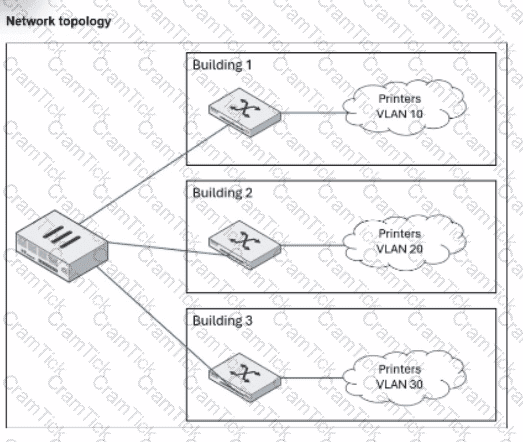
Refer to the exhibit.

An administrator wants to use FortiNAC-F to automatically provision printers throughout their organization. Each building uses its own local VLAN for printers.

Which FortiNAC-F feature would allow this to be accomplished with a single network access policy?

Options:

A.

Dynamic host groups

B.

Logical networks

C.

Device profiling rules

D.

Preferred VLAN designations

Buy Now
Questions 13

When configuring FortiNAC-F to manage FortiGate VPN users, an endpoint compliance policy must be created for the integration.

Why is the endpoint compliance policy necessary for this type of integration?

Options:

A.

To designate the required agent type

B.

To validate the VPN user credentials

C.

To confirm the installed endpoint certificate

D.

To validate the VPN client being used

Buy Now
Questions 14

An administrator wants to build a security rule that will quarantine contractors who attempt to access specific websites.

In addition to a user host profile, which Iwo components must the administrator configure to create the security rule? (Choose two.)

Options:

A.

Methods

B.

Action

C.

Endpoint compliance policy

D.

Trigger

E.

Security String

Buy Now
Questions 15

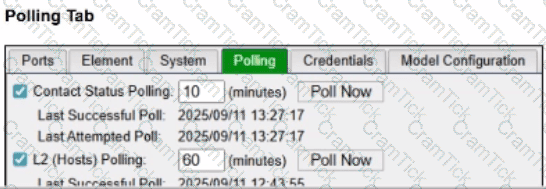
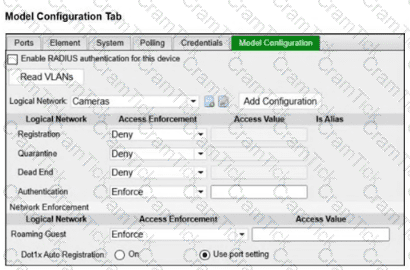
Refer to the exhibits.

An administrator is troubleshooting visibility issues on a modeled switch The switch is configured to use link traps and to provision hosts based on network access policies. The administrator is seeing hosts on ports with no hosts connected and not seeing hosts on ports where hosts are known to be connected.

What is the most likely cause?

Options:

A.

The logical networks are set to deny.

B.

The host has uninstalled the FortiNAC-F agent.

C.

The switch cannot be contacted by FortiNAC-F

D.

The credentials are incorrect.

Buy Now
Questions 16

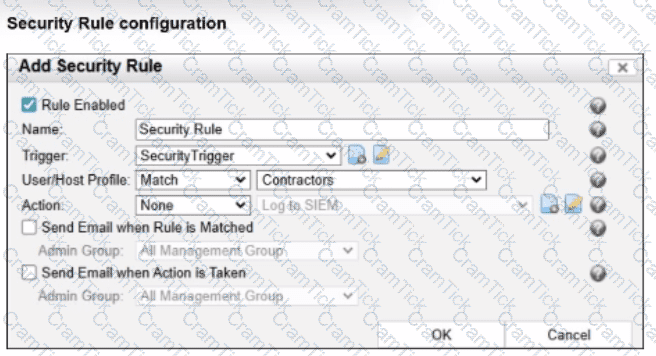
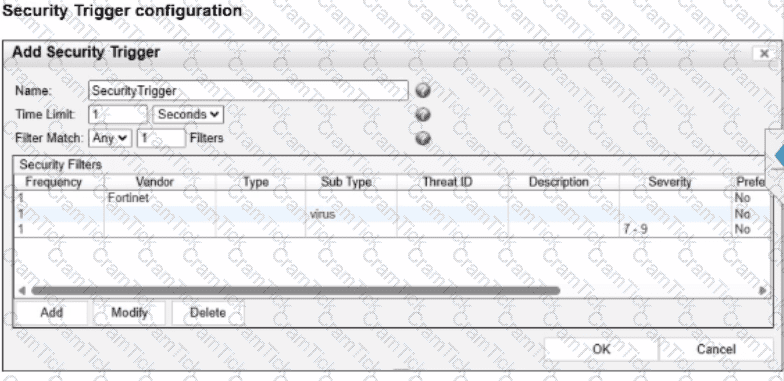
Refer to the exhibits.

Given the current configuration, what would happen if a contractor triggered two of the defined security filters?

Options:

A.

Two security events would be generated, but no security alarm would be generated

B.

A security alarm and two security events would be generated.

C.

Three security events and one security alarm would be generated.

D.

A security event and a security alarm would be generated.

Buy Now
Questions 17

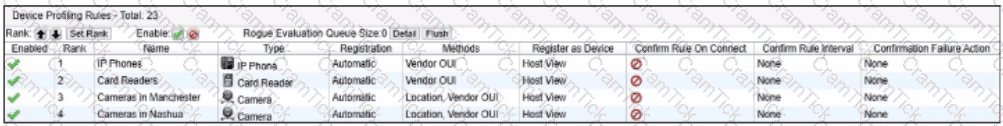
Refer to the exhibit.

Which devices are automatically evaluated by these device profiling rules?

Options:

A.

Rogue devices, only when they are initially added to the database

B.

Known trusted devices, each time they connect

C.

All hosts, each time they connect

D.

Rogue devices, each time they change location

Buy Now
Questions 18

When creating a device profiling rule, what are two advantages of registering the device in the host view? (Choose two.)
Options:

A.

The devices can be managed as a generic SNMP device.

B.

The devices will have connection logs.

C.

The devices can be associated with a user.

D.

The devices can be polled for connection status.

Buy Now
Exam Code: NSE6_FNC_AD-7.6
Exam Name: Fortinet NSE 6 - FortiNAC-F 7.6 Administrator
Last Update: Oct 5, 2026
Questions: 60
NSE6_FNC_AD-7.6 pdf

NSE6_FNC_AD-7.6 PDF

$21.25  $84.99
NSE6_FNC_AD-7.6 Engine

NSE6_FNC_AD-7.6 Testing Engine

$25  $99.99
NSE6_FNC_AD-7.6 PDF + Engine

NSE6_FNC_AD-7.6 PDF + Testing Engine

$33.75  $134.99