Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 8
You need to prevent HTTP connections to the rg1lod28681041n1 Azure Storage account.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 2
You need to add the network interface of a virtual machine named VM1 to an application security group named ASG1.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 7
You need to collect all the audit failure data from the security log of a virtual machine named VM1 to an Azure Storage account. To complete this task, sign in to the Azure portal.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 5
You need to ensure that only devices connected to a 131-107.0.0/16 subnet can access data in the rg1lod28681041 Azure Storage account.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 6
You need to email an alert to a user named adminl@contoso.com if the average CPU usage of a virtual machine named VM1 is greater than 70 percent for a period of 15 minutes.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 9
You need to ensure that the rg1lod28681041n1 Azure Storage account is encrypted by using a key stored in the KeyVault28681041 Azure key vault.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 1
You need to configure Azure to allow RDP connections from the Internet to a virtual machine named VM1. The solution must minimize the attack surface of VM1.
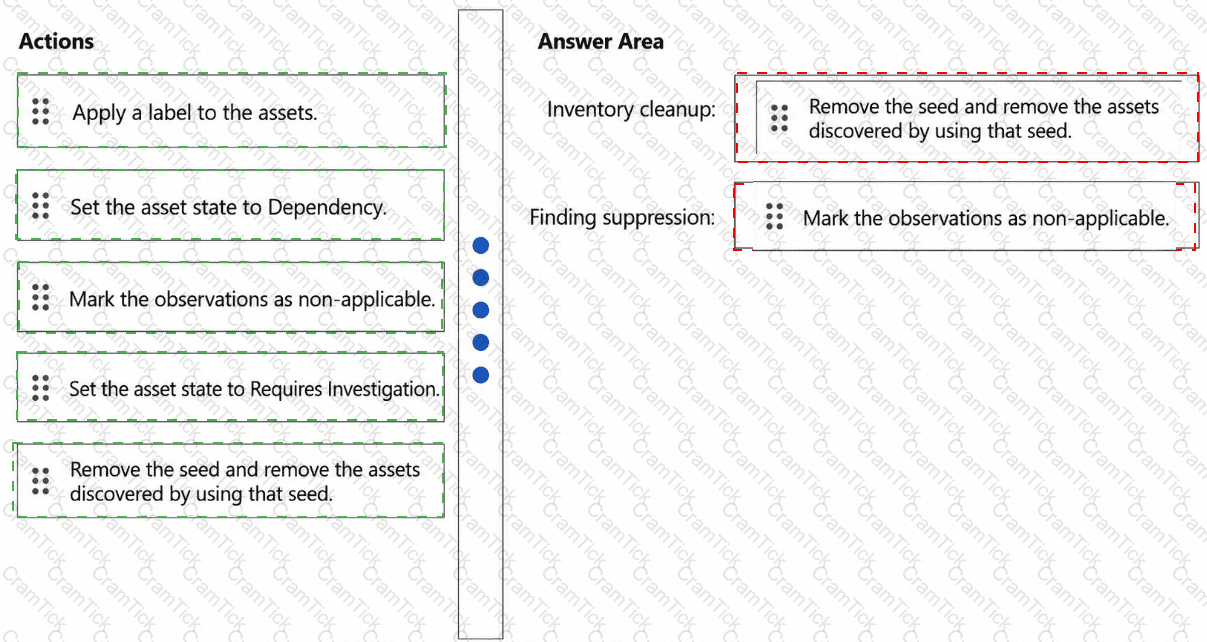
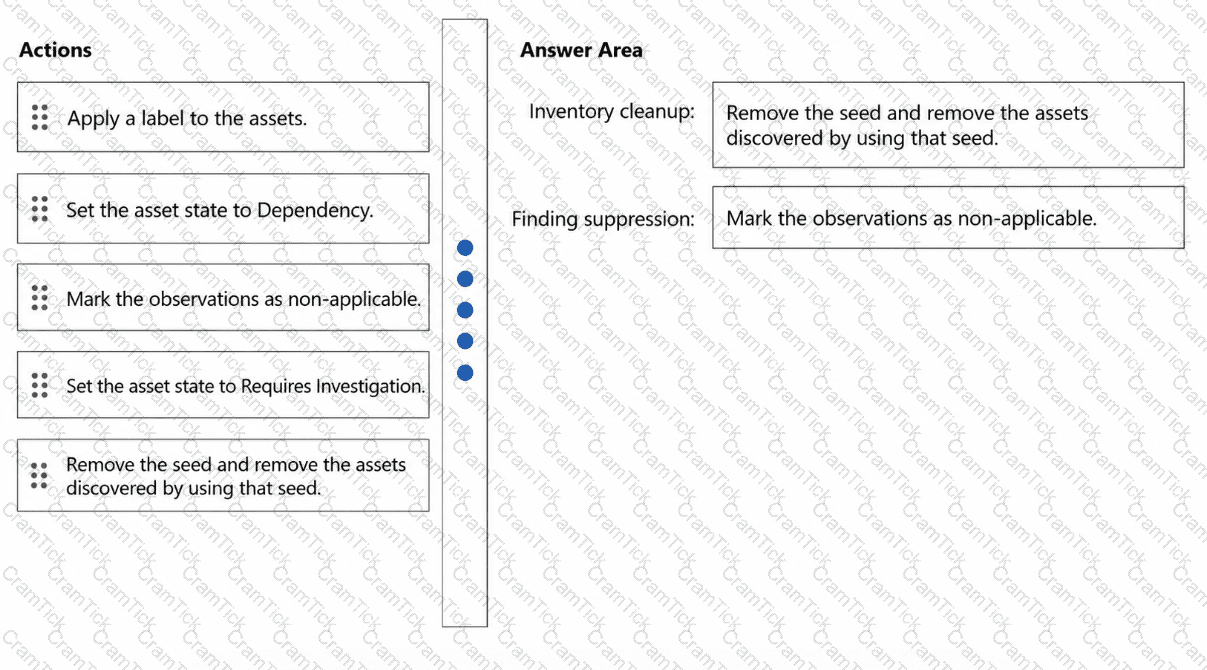
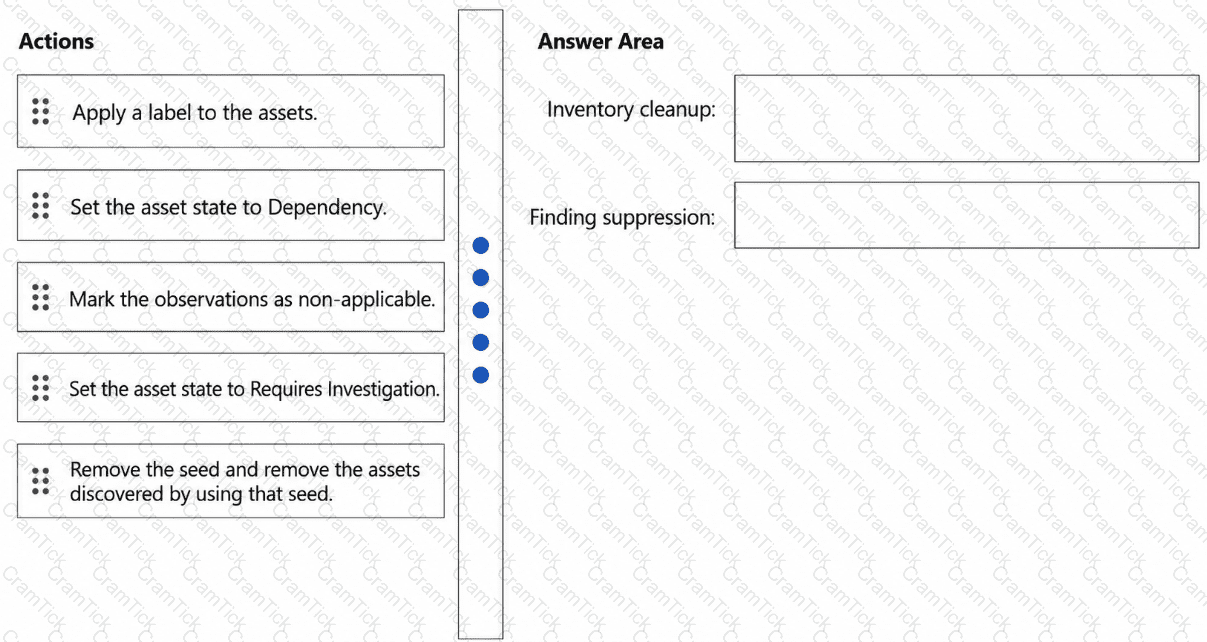
You have a Microsoft Defender External Attack Surface Management (Defender EASM) resource for a company named Contoso. Ltd.
You need to update the Defender EASM workflow to meet the following requirements:
•Assets from a business domain that Contoso no longer owns must be removed from inventory.
•Findings that do NOT apply to confirmed inventory must NOT affect reported counts.
What should you do for each requirement? To answer, drag the appropriate actions to the correct requirements. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
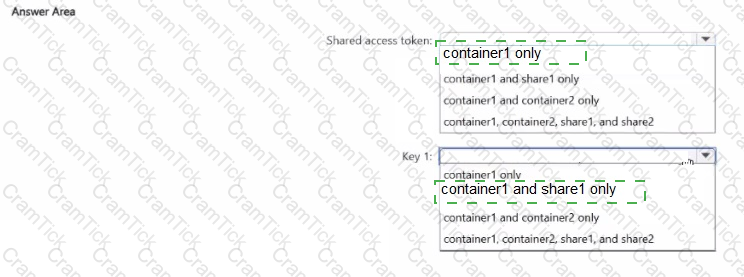
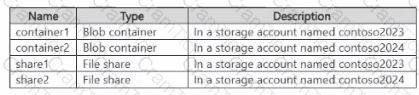
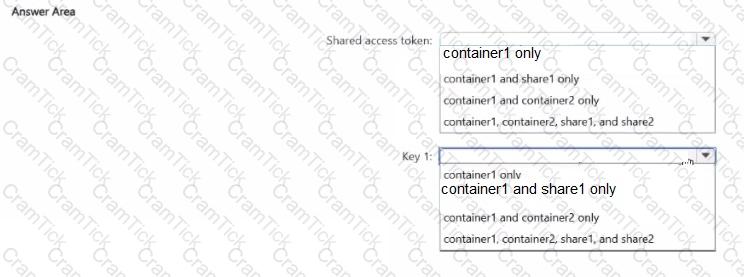
You have an Azure subscription that contains the resources shown in the following table.
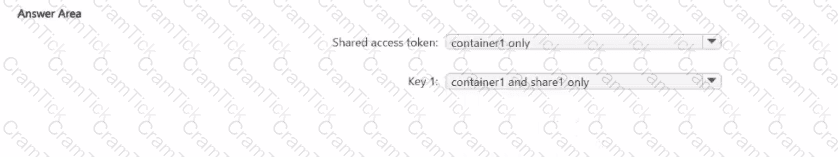
You create a shared access token as shown in the following exhibit.
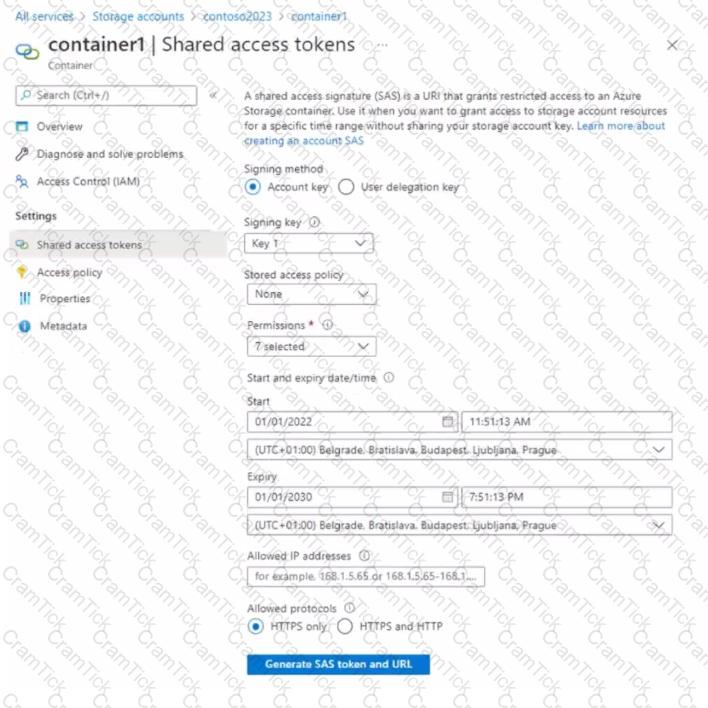
Which resources can you access by using the shared access token and Key 1? To answer, select the appropriate options in the answer area.
NOTE: Each correct answer is worth one point.
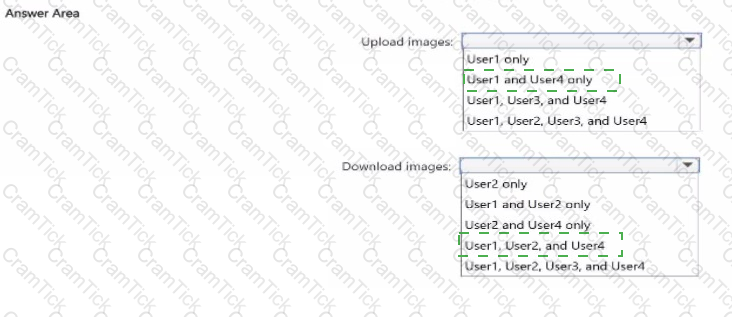
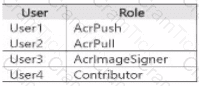
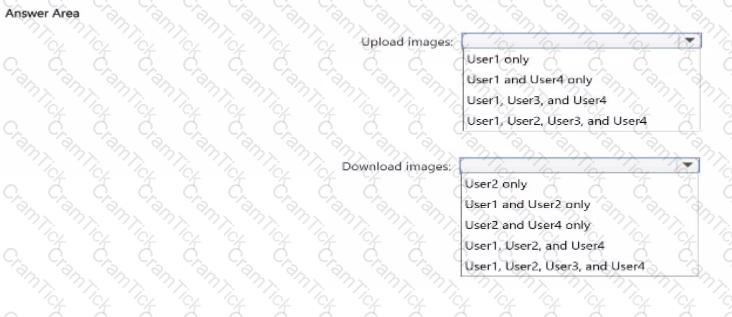
You have an Azure Container Registry named Registry1-
You add role assignments for Registry1 as shown in the following table.
You have an Azure subscription that contains the following servers:
•200 virtual machines that run either Windows Server or Ubuntu Server
•50 Azure Arc enabled servers
You use Azure Policy to manage compliance across all the servers.
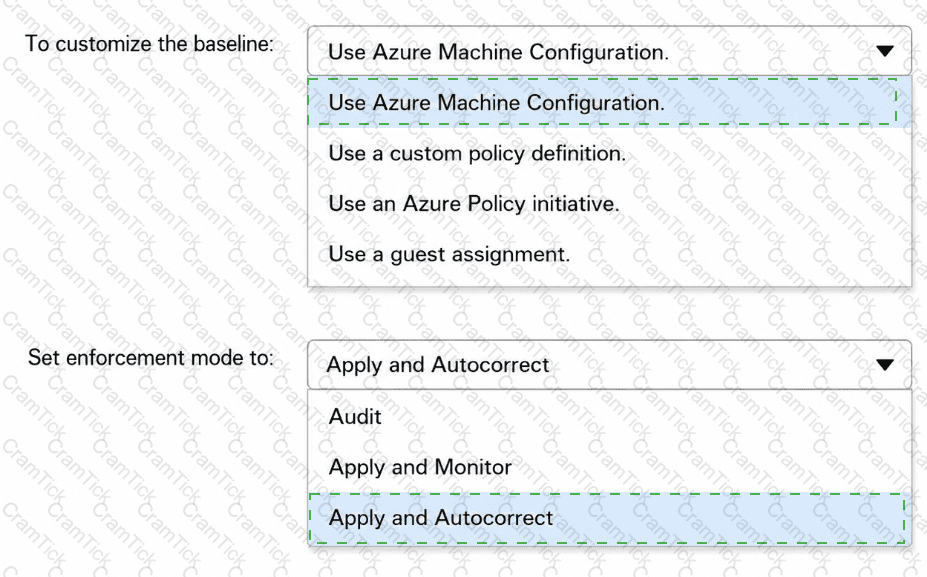
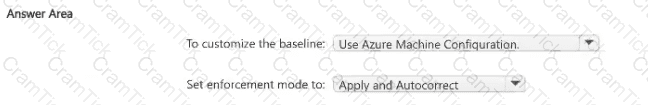
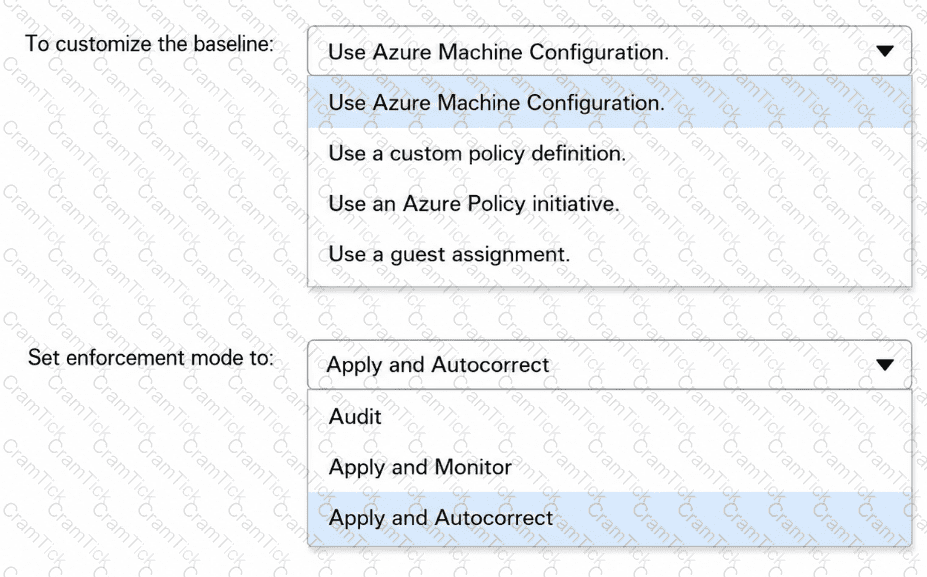
You need to enforce an organization-specific security baseline. The solution must meet the following requirements:
•Customize a built-in security baseline.
•Ensure that configuration changes to the servers are enforced automatically after the security baseline is deployed.
♦Minimize administrative effort.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
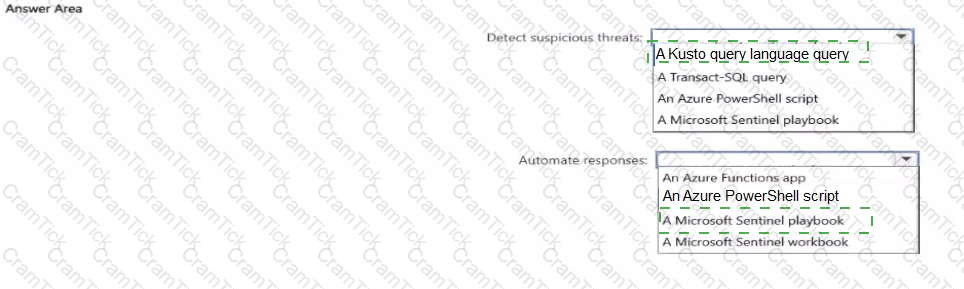
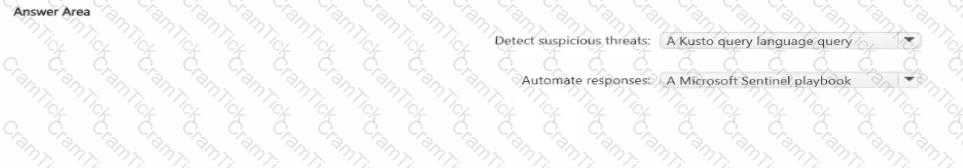
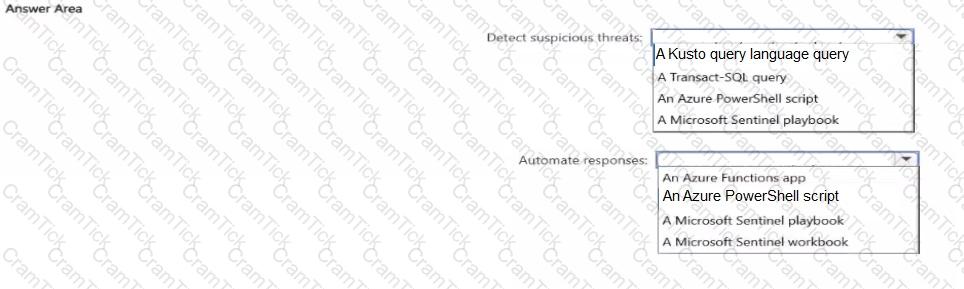
You plan to use Microsoft Sentinel to create an analytic rule that will detect suspicious threats and automate responses. Which components are required for the rule ' lo answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription. All users have Microsoft Exchange Online mailboxes.
You use Microsoft Entra Agent ID to register and manage AI agents.
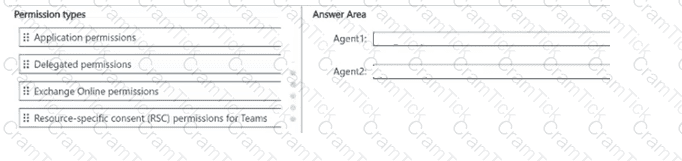
The developers at your company create the following two agents:
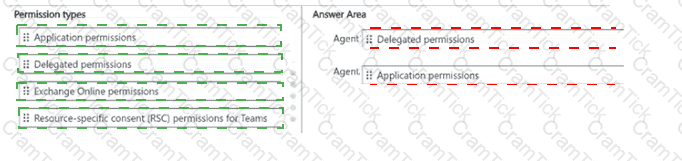
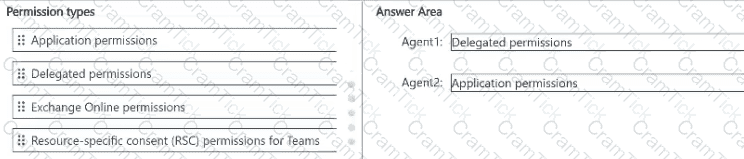
•Agent 1: An interactive agent that helps users summarize their own Exchange Online email
•Agent2: An autonomous agent that sends nightly updates to a Microsoft Teams channel
You need to grant each agent access to Microsoft Graph. The solution must minimize the access scope, while meeting each agent ' s operating model.
Which type of permission should you assign to each agent? To answer, drag the appropriate permission types to the correct agents. Each permission type may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You are configuring a new Microsoft Sentinel workspace named Workspace1.
You have an external IT Service Management (ITSM) system that is NOT supported by any Microsoft Sentinel solutions in Azure Marketplace.
You need to ensure that Workspace1 creates service tickets in the ITSM system for all new security incidents.
What should you create?
You have a Microsoft Entra tenant that contains a group named Group1.
You plan to target Group1 to use the Microsoft Authenticator authentication method.
You need to ensure that the members in Group1 can use the Authenticator app as their primary authentication method.
What should you do?
You have an Azure subscription that is protected by using Microsoft Defender for Cloud.
You plan to upgrade from Foundational Cloud Security Posture Management (CSPM) to Defender CSPM.
Which security policy will be deployed to the subscription automatically?
An application run2 on VM1 and VM2. The application is being migrated from storage account key authentication to Microsoft Entra authentication.
You review the current configuration and identify the following:
• VM1 and VM2 each have a system-assigned managed identity.
• Each application instance requests tokens by using only the local system-assigned managed identity.
• Network access to storage 1 from VMI and VM2 is allowed.
• No Azure RBAC data roles are assigned to the managed identities on storage1.
You need to enable the application on VM1 and VM2 to read and write blob data in storage1 by using Microsoft Entra authentication without changing how the application requests tokens.
Solution: You create a private endpoint for the blob service of storage1.
Does this meet the goal?
You have an Azure virtual network that contains 100 virtual machines and an Azure Firewall instance named FW1.
All the traffic from the virtual machines is routed through FW1.
You need to ensure that FW1 allows access to only a URL of updates contoso.com and blocks all other outbound traffic.
What should you use?
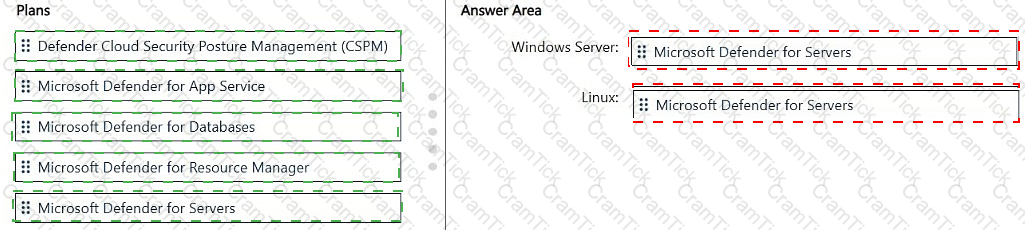
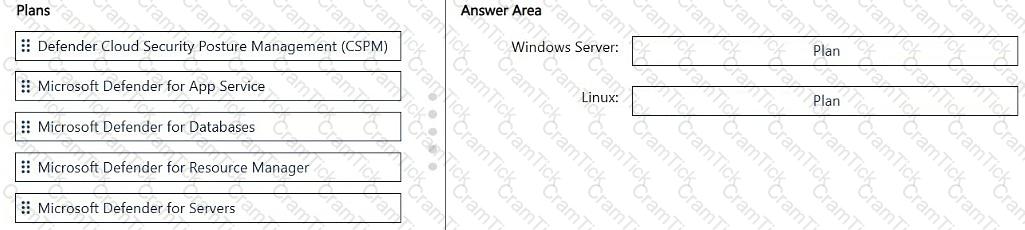
You have an Azure subscription named Sub1. Sub1 contains 60 virtual machines that run either Window Server or Linux.
All the Windows Server virtual machines host line-of-business (LOB) applications and all the Linux virtual machines host backend databases.
You need to enable malware protection for the virtual machines.
Which Microsoft Defender for Cloud plan should you enable for each type of virtual machine? To answer, drag the appropriate plans to the correct virtual machine types. Each plan may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
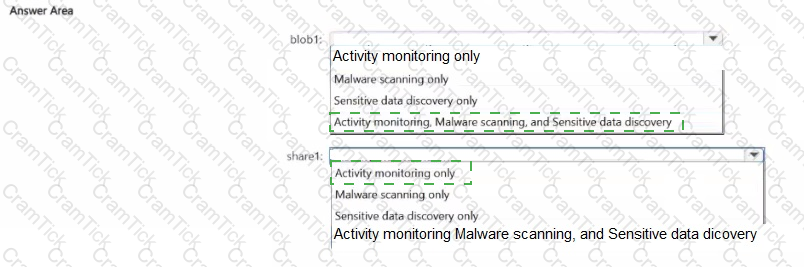
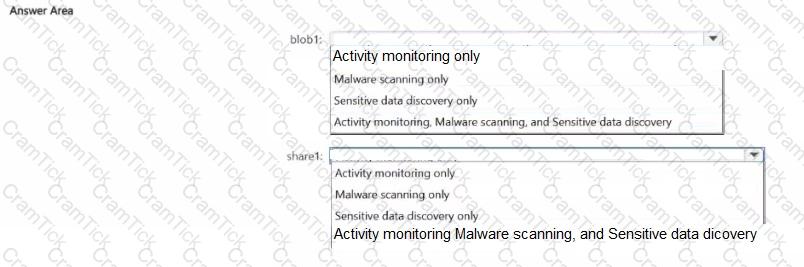
You have an Azure subscription that contains a storage account named storage1.
The storage1 account contains an Azure Blob Storage container named blob1 and an Azure Files share named share1.
You plan to enable Microsoft Defender for Storage on storage 1.
You need to identify which Defender for Storage features can be used for blob1 and share1.
Which Defender for Storage features can be used? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
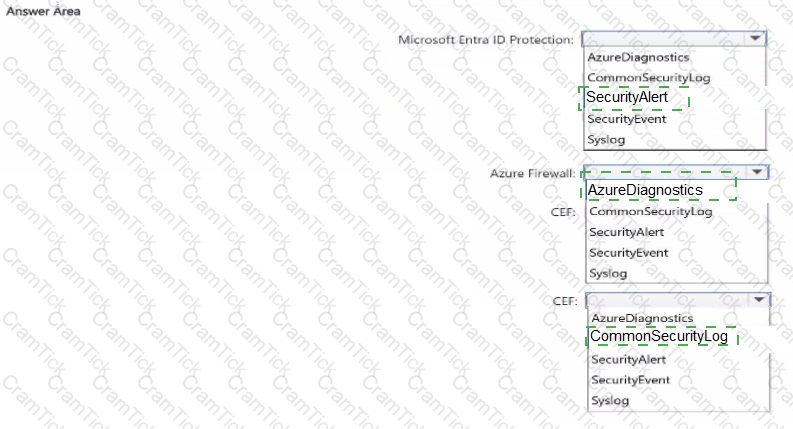
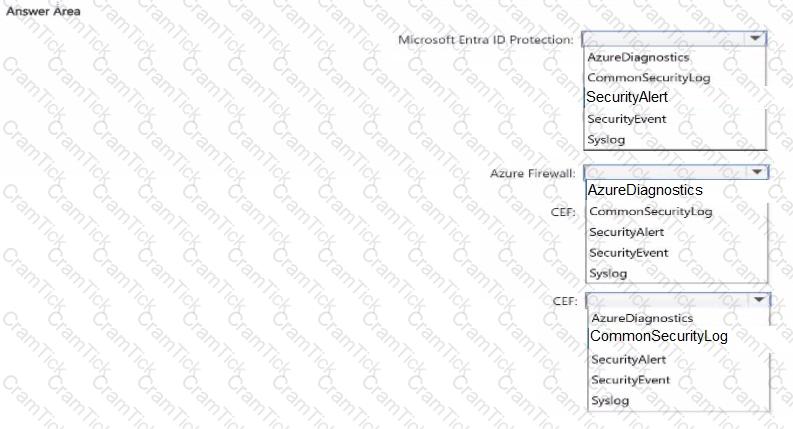
You have a Microsoft Sentinel workspace that has the following data connectors:
• Microsoft Entra ID Protection
• Azure Firewall
• Common Event Formal (CEF)
You need to ensure that data is being ingested from each connector.
From the Logs query window, which table should you query for each connector? To answer, select the appropriate options in the answer area.
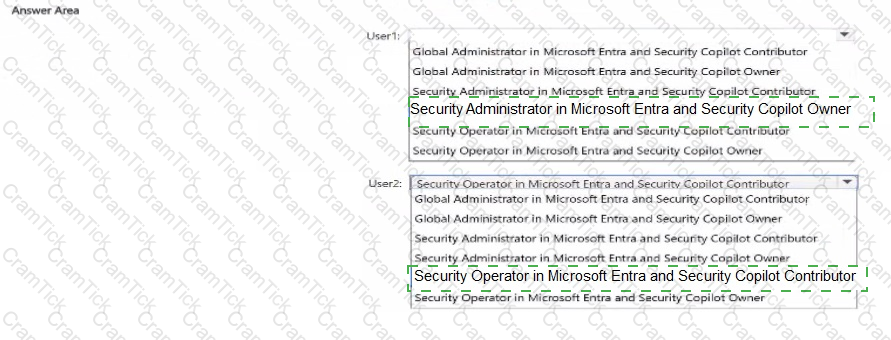
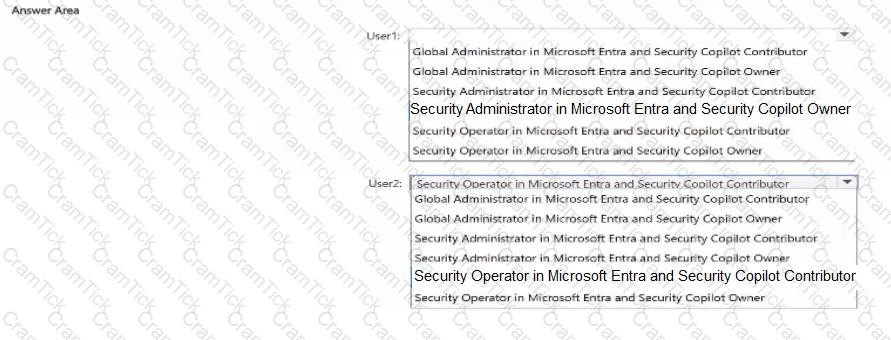
You have a Microsoft 365 tenant that uses Microsoft Security Copilot and Microsoft Defender XDR.
Access to Microsoft Defender XDR is managed by using Microsoft entra global roles.
The Phishing triage Agent is available in Microsoft Defender. The required agent prerequisites and approvals are complete
Two users will perform the following tasks:
• User1 will enable and manage the Phishing Triage Agent settings.
• User2 will use Security Copilot in Microsoft Defender XDR to manage phishing incidents identified by the agent.
You need to assign the least-privileged built in Microsoft Entra role and Security Copilot role combination to each us Which roles should you assign to each user? To answer, select the appropriate options in the answer area.
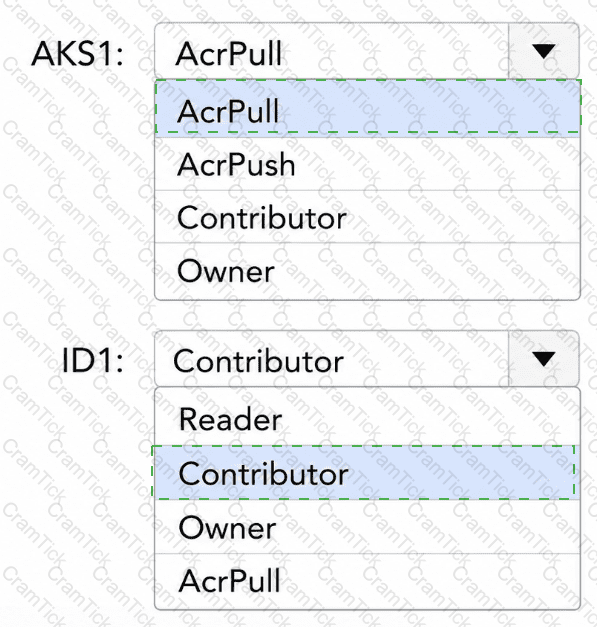
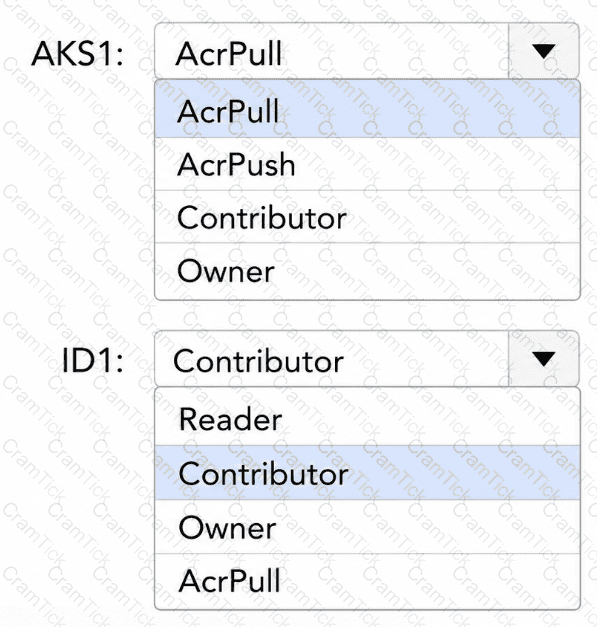
You need to configure the AKS1 and ID 1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note. This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem
After you answer a question in this section, you will NOT be able to return. As a result these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution You create a hunting query.
Does this meet the goal?
You need to configure Microsoft Sentinel to meet the technical requirements.
To what should you set Analytics retention for DnsEvents?
You need to delegate a user to implement the planned change for Defender for Cloud. The solution must follow the principle of least privilege.
Which user should you choose?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You add each virtual machine to a role on storage1.
Does this meet the goal?
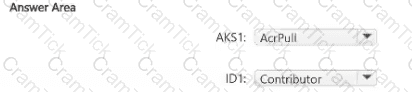
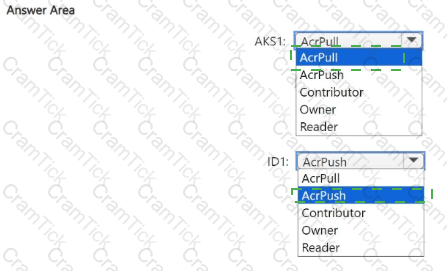
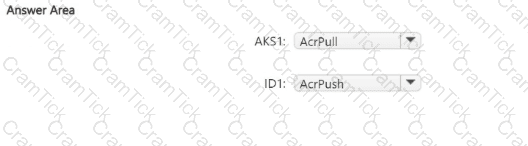
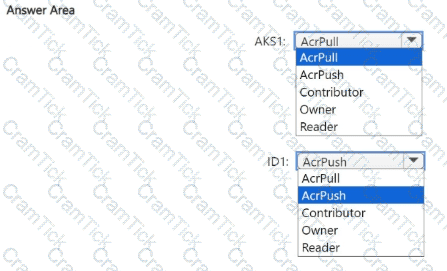
You need to configure the AKS1 and ID1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to delegate a user to implement the planned change for Defender for Cloud. The solution must follow the principle of least privilege.
Which user should you choose?
You need to implement the planned change for WAF1. The solution must minimize administrative effort.
What should you do?
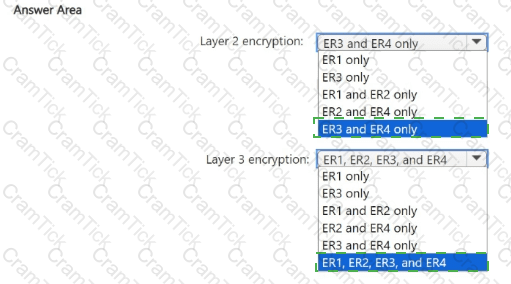
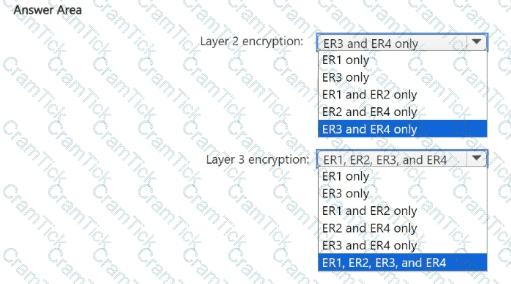
You need to recommend an encryption solution for the planned ExpressRoute implementation. The solution must meet the technical requirements.
Which ExpressRoute circuit should you recommend for each type of encryption? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to implement the function apps to meet the technical requirements.
Which apps should you include in the implementation?
You need to implement the planned change for VM1 to access storage1. The solution must meet the technical requirements.
What should you do first?
You need to implement the planned change for storage2. The solution must meet the technical requirements for storage encryption.
What should you do?
TESTED 14 Oct 2026