Pre-Winter Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cramtick70

SPLK-5002 Splunk Certified Cybersecurity Defense Engineer Questions and Answers

Questions 4

When setting Common Information Model (CIM) accelerations, which parameter should be defined to set how far back in time (specified as a relative time string) the Splunk platform creates its column stores?

Options:

A.

Max summarization search time

B.

Backfill range

C.

Accelerate until maximum time

D.

Summary range

Buy Now
Questions 5

When creating detections, which of the following sequences would result in the most performant SPL query?

Options:

A.

Define base query, combine/summarize data, minimize data, execute calculations, format the data

B.

Define base query, minimize data, combine/summarize data, execute calculations, format the data

C.

Define base query, minimize data, combine/summarize data, format the data, execute calculations

D.

Define base query, minimize data, format the data, combine/summarize data, execute calculations

Buy Now
Questions 6

When developing security metrics, why would a Key Performance Indicator (KPI) that focuses on total perimeter firewall blocks be an ineffective metric?

Options:

A.

This a Key Result Indicator, not a KPI. It is a metric that is measuring the results of the perimeter firewall ' s actions, not the performance of the firewall.

B.

Perimeter firewalls are exposed on the internet directly and thus subject to automated scanners and attack tools.

C.

The metric is too high level, it should be broken down by the type of block. For example, blocks of remote systems that have repeated failed connections to services that do not exist.

D.

Perimeter firewalls should be measured on both the number of connections that they permit as well as the number they block.

Buy Now
Questions 7

For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?

Options:

A.

The data model ' s constraint macro.

B.

The data model ' s index list.

C.

The data model ' s root expression.

D.

The data model ' s dataset hierarchy.

Buy Now
Questions 8

While working with the SOC analysts to review current contextualization processes, a request for automation has been raised by the SOC team. They are asking for a new automation that will check a potentially malicious URL against a remote URL filtering list. Which of the following options will work for them?

Options:

A.

Neither Adaptive Action or Input Playbook

B.

Adaptive Response Action or Input Playbook

C.

Adaptive Response Action

D.

Input Playbook

Buy Now
Questions 9

Which Splunk feature makes SPL searches shorter and reusable by inserting it into search strings?

Options:

A.

Knowledge objects

B.

Commands

C.

Lookups

D.

Macros

Buy Now
Questions 10

Which stats event field created by an adaptive response action allows for troubleshooting the correlation search that created the notable event?

Options:

A.

orig_sid

B.

risk_sid

C.

search_sid

D.

result_sid

Buy Now
Questions 11

What should a security engineer prioritize when building a new security process?

Options:

A.

Integrating it with legacy systems

B.

Ensuring it aligns with compliance requirements

C.

Automating all workflows within the process

D.

Reducing the overall number of employees required

Buy Now
Questions 12

An engineer has been asked to build a new dashboard after an increase in login failures across the organization ' s Microsoft Azure domain. They need to construct a search to only display failed logins for their Azure Active Directory users and create a visualization that will help quickly identify failed logins that originate outside of North America. Which search and visualization type combination will achieve this?

Options:

A.

Azure sign-in search/visualization combination using a Cluster Map but not the required failed-login condition

B.

Azure sign-in search using the alternative geographic visualization shown as a Choropleth Map

C.

Azure sign-in search using the alternative failure/geographic combination shown as a Choropleth Map

D.

Azure AD failed-login search using geographic coordinates with a Cluster Map

Buy Now
Questions 13

Based on the provided screenshot, different machines or accounts have been associated with chosen threat objects. Which two Enterprise Security frameworks are responsible for programmatically associating this information?

Options:

A.

Threat Intelligence, Risk

B.

Risk, Assets & Identities

C.

Risk, Incident Review

D.

Threat Intelligence, Assets & Identities

Buy Now
Questions 14

When creating a case in Splunk SOAR, which action should be taken to correlate various findings (risk notables) to ensure all are actioned?

Options:

A.

Search Splunk Enterprise Security for similar or duplicate events based on the threat_object field in a risk notable.

B.

Search Splunk Enterprise Security for all related events based on key fields in a notable and select how to process the results to decide which events to merge into the current investigation.

C.

Search Splunk Enterprise Security for similar or duplicate events based on the risk_object field in a risk notable.

D.

Search Splunk Enterprise Security for all related events based on key fields in a risk notable and select how to process the results to decide which events to merge into the current investigation.

Buy Now
Questions 15

A cyber defense engineer plays a role in maintaining a secure SOAR Cloud configuration. Which network security statement is correct about SOAR Cloud?

Options:

A.

Splunk Cloud initiates an outbound SSL connection to both the Automation Broker and managed endpoints.

B.

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

C.

The Automation Broker initiates an inbound SSL connection to Splunk Cloud, and also initiates an outbound connection to the managed endpoints.

D.

The Automation Broker initiates an outbound SSL connection to Splunk Cloud, and the managed endpoint initiates an outbound connection to the Automation Broker.

Buy Now
Questions 16

An automation engineer for the Wonderland SOC has configured a new asset and is getting an HTTP 403 response code. Which of the following is a possible cause of the error code?

Options:

A.

The endpoint that the asset is configured for does not exist.

B.

Either the asset username or password is incorrect.

C.

The asset endpoint requires a token rather than a username and password.

D.

Asset credentials do not have adequate permissions.

Buy Now
Questions 17

How can you incorporate additional context into notable events generated by correlation searches?

Options:

A.

By adding enriched fields during search execution

B.

By using the dedup command in SPL

C.

By configuring additional indexers

D.

By optimizing the search head memory

Buy Now
Questions 18

What does the following search do?

source=WinEventLog:security* sourcetype= " WinEventLog* " EventCode=4688

| stats count, values(process) as process by parent_process_name

Options:

A.

Displays a count of processes created by the same user.

B.

Displays a list of newly created processes and the user that created them.

C.

Displays a count of processes created by the same child process.

D.

Displays a list of processes and their parent processes.

Buy Now
Questions 19

An effective method for building automation workflows is to follow the OODA (Observe, Orient, Decide, Act) loop stages. When transitioning between the Decide and Act stages, what additional step should be included before automating the Act stage?

Options:

A.

Validate response data paths from the Decide stage.

B.

Validate if the asset, identity, or service has an exemption.

C.

Create a new automation playbook.

D.

Create a new response template.

Buy Now
Questions 20

Which of the following is not a type of metadata that can be returned by the metadata command?

Options:

A.

hosts

B.

sources

C.

assets

D.

sourcetypes

Buy Now
Questions 21

The SOC Manager requested a better method to standardize the list of tasks that analysts follow when they evaluate events or cases. Which Splunk SOAR feature allows the creation of SOPs based on criteria like the type of event or attack vector?

Options:

A.

Workbooks

B.

Events

C.

Cases

D.

Incidents

Buy Now
Questions 22

What field is used by default to direct data into CIM data model datasets?

Options:

A.

tag

B.

sourcetype

C.

source

D.

dataset

Buy Now
Questions 23

If a correlation search cannot be run at the configured time, which scheduling option should an engineer use to ensure there are no backfill gaps in data?

Options:

A.

Default

B.

Continuous

C.

Real-time

D.

Auto

Buy Now
Questions 24

One of the goals of a detection engineer is to facilitate the triage process by providing the analyst as much context as possible. One way of accomplishing this is to provide context options through the use of which of the following settings?

Options:

A.

Correlation Search Name

B.

Risk Object Name

C.

Risk Analysis Adaptive Response Action

D.

Drill-down search

Buy Now
Questions 25

Which fields are used to determine asset priority, when priority is assigned through an asset and identity lookup?

Options:

A.

dest, src, or dvc

B.

dest, src, or tag

C.

user or src_user

D.

dest_user or src_user

Buy Now
Questions 26

Which of the following cURL commands would allow an engineer to effectively disable the REST API endpoint they ' ve been utilizing for testing a detection named TestSearchDevelopment?

Options:

A.

curl -k -u admin\:pass https://localhost:8089/servicesNS/admin/search/saved/searches/TestSearchDevelopment/ -X DELETE

B.

Splunk endpoints cannot be disabled.

C.

curl -k -u admin\:pass https://localhost:8089/servicesNS/admin/search/saved/searches/TestSearchDevelopment/disable -X POST

D.

curl -k -u admin\:pass https://localhost:8089/servicesNS/admin/search/saved/searches/TestSearchDevelopment/disable -X PUT

Buy Now
Questions 27

Below is an example of a Sysmon process create log. Which EventCode would be associated with this log entry?
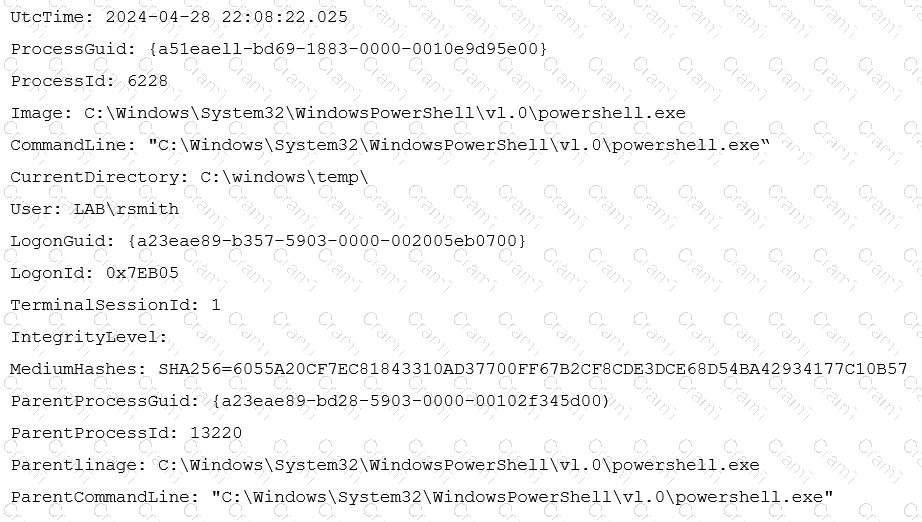
Options:

A.

EventCode=1

B.

EventCode=4

C.

EventCode=3

D.

EventCode=2

Buy Now
Questions 28

Which of the following actions will allow access to a list of alert actions via the API?

Options:

A.

| rest /services/alerts/adaptive_response_action

B.

| rest /services/alerts/correlationsearches

C.

| rest /services/alerts/alert actions/_acl

D.

| rest /services/alerts/alert_actions

Buy Now
Questions 29

Consider the following series of events:

4:00 GMT Detection runs for interval 3:30–4:00

4:30 GMT Detection runs for interval 4:00–4:30

4:35 GMT Event 1 occurs on an endpoint

4:45 GMT Event 1 is indexed

5:00 GMT Detection runs for interval 4:30–5:00

5:05 GMT Event 1 finding is added to ES with timestamp 4:35

5:24 GMT Event 2 occurs on an endpoint

5:30 GMT Detection runs for interval 5:00–5:30

5:35 GMT Event 2 is indexed

6:00 GMT Detection runs for interval 5:30–6:00

What is the problem with the detection schedule chosen and how can it be solved?

Options:

A.

The logs are delayed so the detection time window needs to be decreased.

B.

The time window for the detection is too small, causing duplicate alerts.

C.

The time window for the detection is too large, causing duplicate alerts.

D.

The logs are delayed so the detection time window needs to be increased.

Buy Now
Questions 30

Which of the following detections would use a high count of events with Windows Event Code 4740 grouped by a user to determine suspicious behavior?

Options:

A.

Detect Excessive AWS Security Scanning

B.

Detect Excessive User Account Lockouts

C.

Detect Excessive User Logins

D.

Detect Excessive Network Connections

Buy Now
Questions 31

An engineer wants to track and report on all authentication to corporate assets and wants to prioritize critical assets without significantly increasing the number of findings created. What process could be used to accomplish this goal?
Options:

A.

Decrease the risk score of non-critical assets in all existing detections.

B.

Add all access attempts to the Risk Index and increase criticality of critical assets.

C.

Add the critical assets to the risk data model.

D.

Determine a general risk rule for all access attempts to all assets, and then increase the Risk Factor for critical assets.

Buy Now
Exam Code: SPLK-5002
Exam Name: Splunk Certified Cybersecurity Defense Engineer
Last Update: Oct 6, 2026
Questions: 105
SPLK-5002 pdf

SPLK-5002 PDF

$25.5  $84.99
SPLK-5002 Engine

SPLK-5002 Testing Engine

$30  $99.99
SPLK-5002 PDF + Engine

SPLK-5002 PDF + Testing Engine

$40.5  $134.99