Black Friday Madness- 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: fifty75ct

NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect Questions and Answers

Questions 4

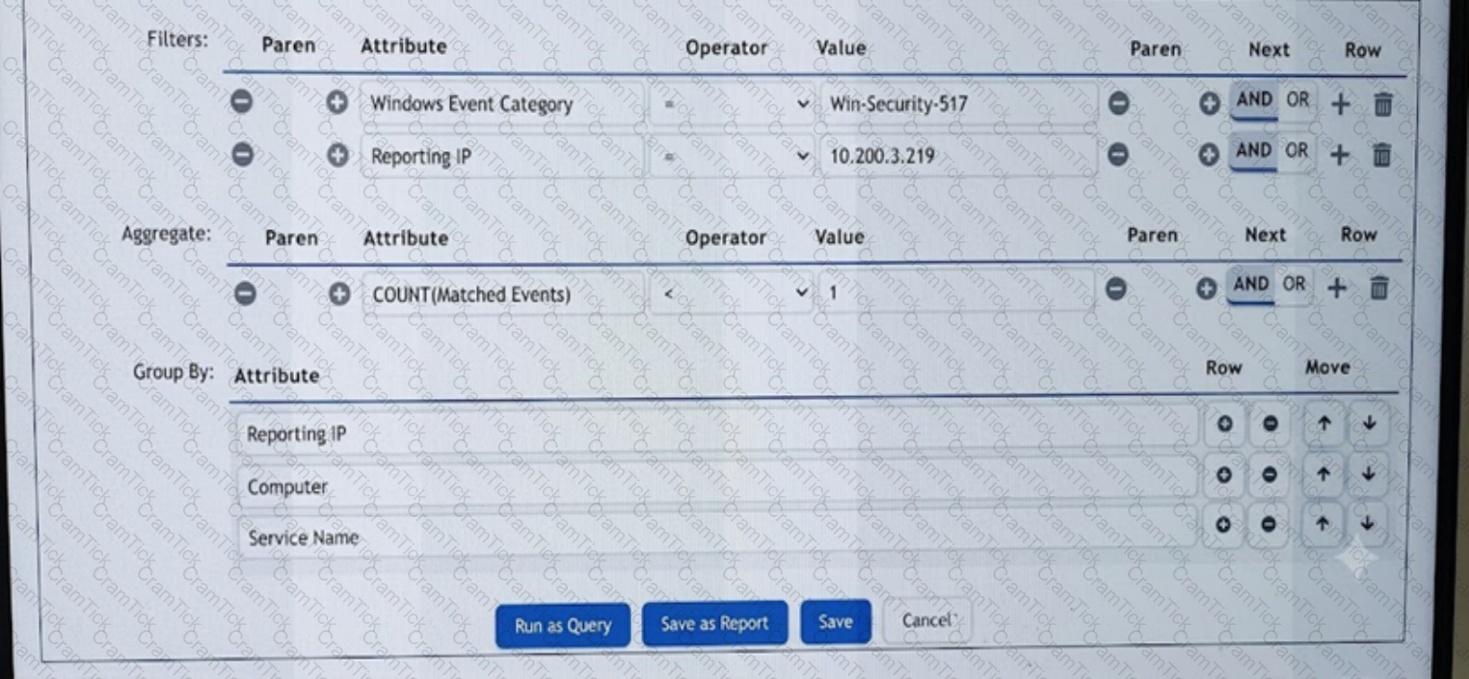
Refer to the exhibit.
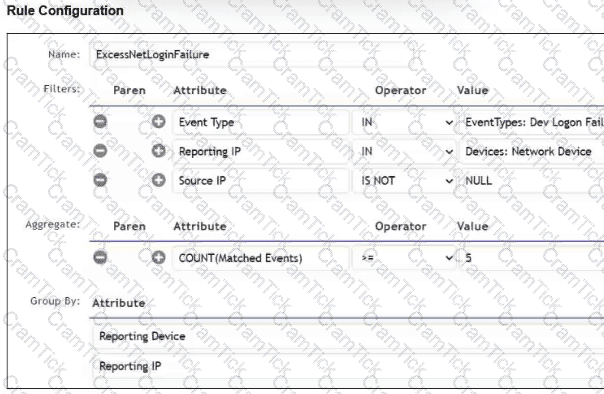
You created a subpattern to detect at least five failed login attempts from any single user and source IP address to the same network device. However, it is creating more incidents than you had anticipated.

What are the two mistakes in the incident subpattern rule configuration? (Choose two.)

Exhibit: FortiSIEM Rule Configuration

FortiSIEM failed login rule configuration

Options:

A.

The Group By attributes are missing the User field.

B.

The Group By attributes are missing the Source IP field.

C.

The aggregate condition is too restrictive.

D.

The mandatory Event Parser Name attribute is missing.

Buy Now
Questions 5

A partner organization recently suffered a distributed denial-of-service (DDoS) attack, but the adversary’s identity and TTPs remain unknown. Your SOC has not received any relevant threat intelligence from the partner organization, but you are asked to determine whether similar activity could be happening in your environment. Which threat hunting action should you perform first? Choose one answer.

Options:

A.

Configure SIEM rules to alert when inbound traffic exceeds baseline thresholds.

B.

Use a packet analyzer to capture and review all traffic flows on critical devices.

C.

Develop a hunting hypothesis based on how DDoS can be executed against your network.

D.

Use threat intelligence to enrich the IP addresses of all external source IP addresses.

Buy Now
Questions 6

While monitoring your network, you discover that one FortiGate device is sending significantly more logs to FortiAnalyzer than all of the other FortiGate devices in the topology.

Additionally, the ADOM that the FortiGate devices are registered to consistently exceeds its quota.

What are two possible solutions? (Choose two.)

Options:

A.

Increase the storage space quota for the first FortiGate device.

B.

Create a separate ADOM for the first FortiGate device and configure a different set of storage policies.

C.

Reconfigure the first FortiGate device to reduce the number of logs it forwards to FortiAnalyzer.

D.

Configure data selectors to filter the data sent by the first FortiGate device.

Buy Now
Questions 7

You want to trigger an incident when multiple failed logins from the same host are followed by a successful login on that same host within 15 minutes. The rule must correlate all events by source IP address and user to ensure they belong to the same login sequence. Which three configurations achieve this goal? Choose three answers.

Options:

A.

Ensure both subpatterns have the same aggregate condition.

B.

Define a time window condition for each subpattern.

C.

Configure two subpatterns—one for failed logins and one for the successful login.

D.

Apply sequential logic using a FOLLOWED_BY operator between the subpatterns.

E.

Define the subpattern relationships and constraints.

Buy Now
Questions 8

Which two types of variables can you use in playbook tasks? (Choose two.)

Options:

A.

input

B.

Output

C.

Create

D.

Trigger

Buy Now
Questions 9

Refer to the exhibit.

Assume that all devices in the FortiAnalyzer Fabric are shown in the image.

Which two statements about the FortiAnalyzer Fabric deployment are true? (Choose two.)

Options:

A.

FortiGate-B1 and FortiGate-B2 are in a Security Fabric.

B.

There is no collector in the topology.

C.

All FortiGate devices are directly registered to the supervisor.

D.

FAZ-SiteA has two ADOMs enabled.

Buy Now
Questions 10

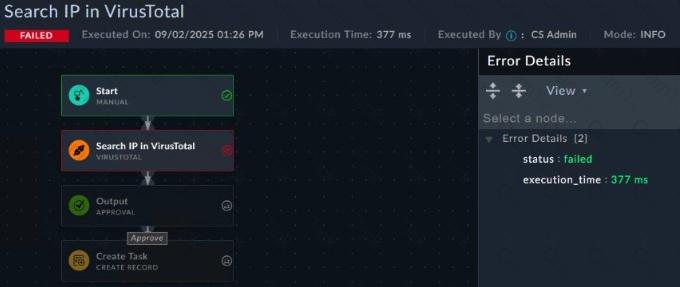
Refer to the exhibit.

You created a new playbook and executed it as a test. However, it failed to run. You want to investigate, but you do not see details about the error. What is the reason for the lack of details?

Options:

A.

The connector is deactivated.

B.

The playbook logging level must be debug.

C.

The Ignore Error option is enabled.

D.

The user that executed the playbook does not have the necessary permissions.

Buy Now
Questions 11

You want to use the queue and shift management feature to automatically assign newly created low-priority tasks to members of the L1 queue. However, you are unable to add the Tasks module to the Module Types list. What is the problem? Choose one answer.

Options:

A.

The Queueable option is disabled for the Tasks module.

B.

There is a higher priority queue for the Tasks module.

C.

The Tasks module is not supported by queue and shift management.

D.

Shift-based assignment is disabled.

Buy Now
Questions 12

Refer to the exhibit,

which shows the partial output of the MITRE ATT & CK Enterprise matrix on FortiAnalyzer.

Which two statements are true? (Choose two.)

Options:

A.

There are four techniques that fall under tactic T1071.

B.

There are four subtechniques that fall under technique T1071.

C.

There are event handlers that cover tactic T1071.

D.

There are 15 events associated with the tactic.

Buy Now
Questions 13

Refer to the exhibits.

You configured a custom event handler and an associated rule to generate events whenever FortiMail detects spam emails. However, you notice that the event handler is generating events for both spam emails and clean emails.

Which change must you make in the rule so that it detects only spam emails?

Options:

A.

In the Log Type field, select Anti-Spam Log (spam)

B.

In the Log filter by Text field, type type==spam.

C.

Disable the rule to use the filter in the data selector to create the event.

D.

In the Trigger an event when field, select Within a group, the log field Spam Name (snane) has 2 or more unique values.

Buy Now
Questions 14

A very long FortiSOAR playbook failed at step 30 because of an intermittent networking issue, which has now been resolved. You want to finish executing the playbook without repeating earlier steps or losing prior context. Which action should you take? Choose one answer.

Options:

A.

Use mock input for step 30 and re-run the playbook.

B.

Use the Load ENV JSON option in the Jinja Editor and then render the output.

C.

Use the Rerun From Last Failed Step option from the executed playbook logs.

D.

Add a connector from the trigger to step 30 directly and re-run the playbook.

Buy Now
Questions 15

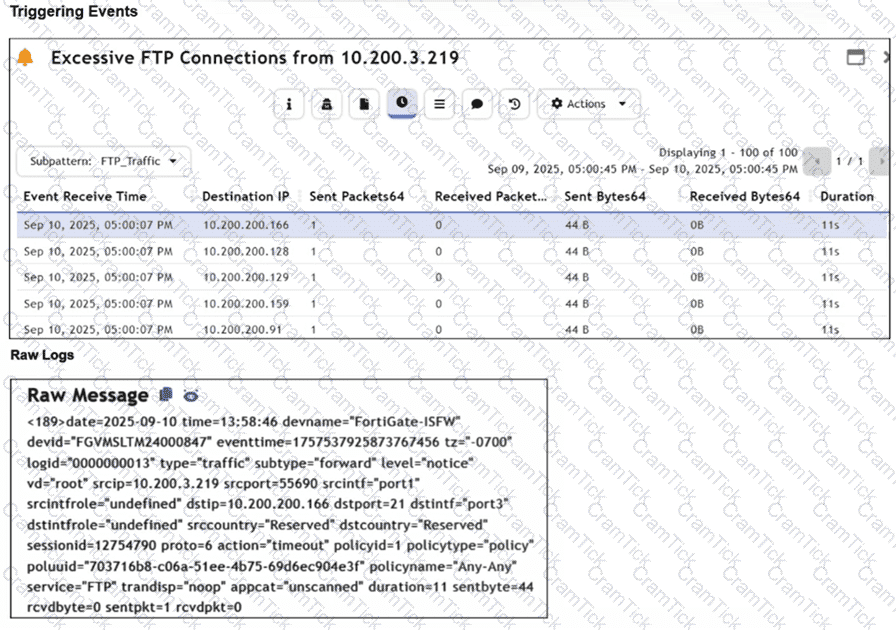
Refer to the exhibits.

Assume that the traffic flows are identical, except for the destination IP address. There is only one FortiGate in network address translation (NAT) mode in this environment.

Based on the exhibits, which two conclusions can you make about this FortiSIEM incident? (Choose two answers)

Options:

A.

The client 10.200.3.219 is conducting active reconnaissance.

B.

FortiGate is not routing the packets to the destination hosts.

C.

The destination hosts are not responding.

D.

FortiGate is blocking the return flows.

Buy Now
Questions 16

You need to create a nested query in FortiSIEM that satisfies the following conditions:

Find all devices discovered by any FortiSIEM Windows Agent.

From those devices, identify those that have generated Windows Login Failure events.

Which two query components should be used for this nested query? Choose two answers.

Options:

A.

Outer Event Query

B.

Outer CMDB Query

C.

Inner CMDB Query

D.

Inner Event Query

Buy Now
Questions 17

A customer wants FortiAnalyzer to run an automation stitch that executes a CLI command on FortiGate to block a predefined list of URLs, if a botnet command-and-control (C & C) server IP is detected.

Which FortiAnalyzer feature must you use to start this automation process?

Options:

A.

Playbook

B.

Data selector

C.

Event handler

D.

Connector

Buy Now
Questions 18

Which role does a threat hunter play within a SOC?

Options:

A.

investigate and respond to a reported security incident

B.

Collect evidence and determine the impact of a suspected attack

C.

Search for hidden threats inside a network which may have eluded detection

D.

Monitor network logs to identify anomalous behavior

Buy Now
Questions 19

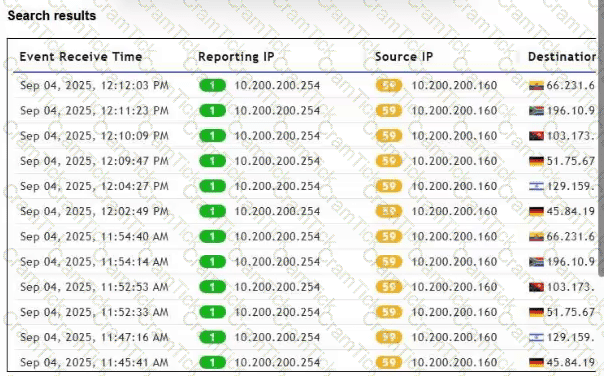
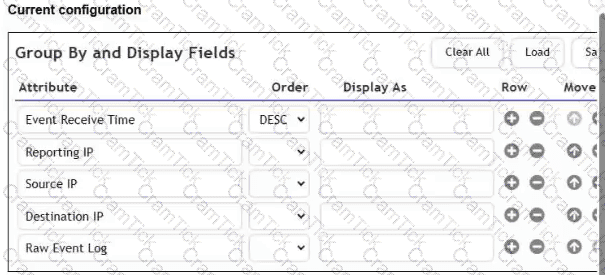
Refer to the exhibits.

You are searching for permitted traffic to public destination IP addresses outside of North America. Your investigation shows that one local computer is communicating with destination IP addresses that fit the criteria. However, you also notice that some of those IP addresses are duplicates, and you must aggregate the results.

Which three steps do you need to use to configure the Group By and Display Fields window to show only aggregated results? (Choose three.)

Options:

A.

Sort the Destination IP attribute row by descending order.

B.

Remove the Event Receive Time attribute row.

C.

Add the SUM (Matched Events) attribute row.

D.

Add the Count (Matched Events) attribute row.

E.

Remove the Raw Event Log attribute row.

Buy Now
Questions 20

Refer to the exhibit.

What are the two mistakes in the incident subpattern rule configuration? Choose two answers.

Options:

A.

The subpattern is missing a time window definition.

B.

The aggregate operator is incorrect.

C.

The Group By attributes conflict with each other.

D.

The mandatory Event Type attribute is missing.

Buy Now
Questions 21

Review the following incident report:

Attackers leveraged a phishing email campaign targeting your employees.

The email likely impersonated a trusted source, such as the IT department, and requested login credentials.

An unsuspecting employee clicked a malicious link in the email, leading to the download and execution of a Remote Access Trojan (RAT).

The RAT provided the attackers with remote access and a foothold in the compromised system.

Which two MITRE ATT & CK tactics does this incident report capture? (Choose two.)

Options:

A.

Initial Access

B.

Defense Evasion

C.

Lateral Movement

D.

Persistence

Buy Now
Questions 22

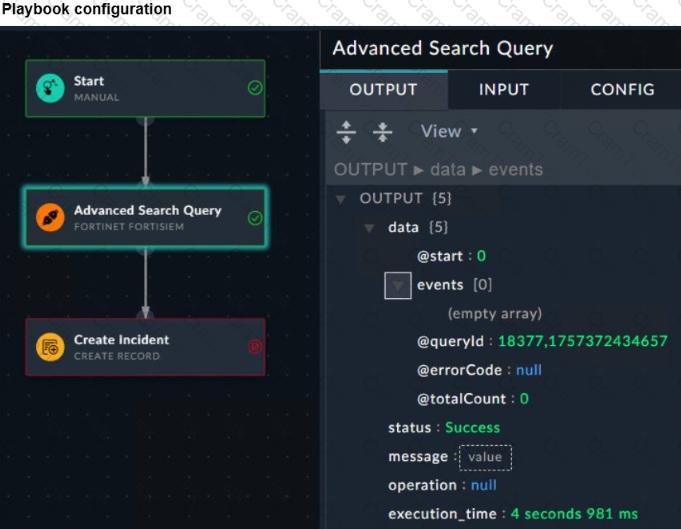
Refer to the exhibit.

You created a threat hunting playbook to perform a search query using the FortiSIEM connector. However, when you run the playbook, you do not see any output. Which step must you take first in your troubleshooting process?

Options:

A.

Confirm that the event logs matching your criteria exist on FortiSIEM.

B.

Configure a Set Variable step to save the output.

C.

Confirm that the FortiSIEM connector is up.

D.

Check the documentation for the input and output for the action.

Buy Now
Questions 23

A large enterprise FortiSIEM deployment is experiencing delays in log correlation and analytics. Which architectural adjustment is most appropriate? Choose one answer.

Options:

A.

Limit the number of rules using streaming mode.

B.

Add more workers.

C.

Add more collectors.

D.

Increase supervisor CPU and memory.

Buy Now
Questions 24

Which three statements accurately describe step utilities in a playbook step? (Choose three answers)

Options:

A.

The Timeout step utility sets a maximum execution time for the step and terminates playbook execution if exceeded.

B.

The Loop step utility can only be used once in each playbook step.

C.

The Variables step utility stores the output of the step directly in the step itself.

D.

The Condition step utility behavior changes depending on if a loop exists for that step.

E.

The Mock Output step utility uses HTML format to simulate real outputs.

Buy Now
Questions 25

When you use a manual trigger to save user input as a variable, what is the correct Jinja expression to reference the variable? (Choose one answer)

Options:

A.

{{ vars.input.params. < variable_name > }}

B.

{{ globalVars. < variable_name > }}

C.

{{ vars.item. < variable_name > }}

D.

{{ vars.steps. < variable_name > }}

Buy Now
Questions 26

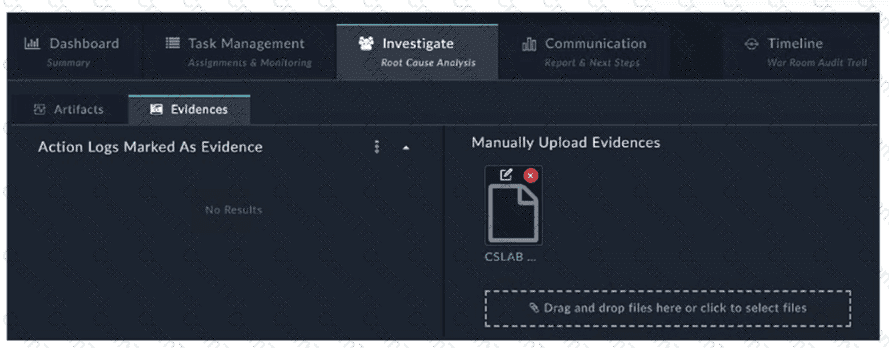
Refer to the exhibit.

How do you add a piece of evidence to the Action Logs Marked As Evidence area? (Choose one answer)

Options:

A.

By tagging output or a workspace comment with the keyword Evidence

B.

By linking an indicator to the war room

C.

By creating an evidence collection task and attaching a file

D.

By executing a playbook with the Save Execution Logs option enabled

Buy Now
Questions 27

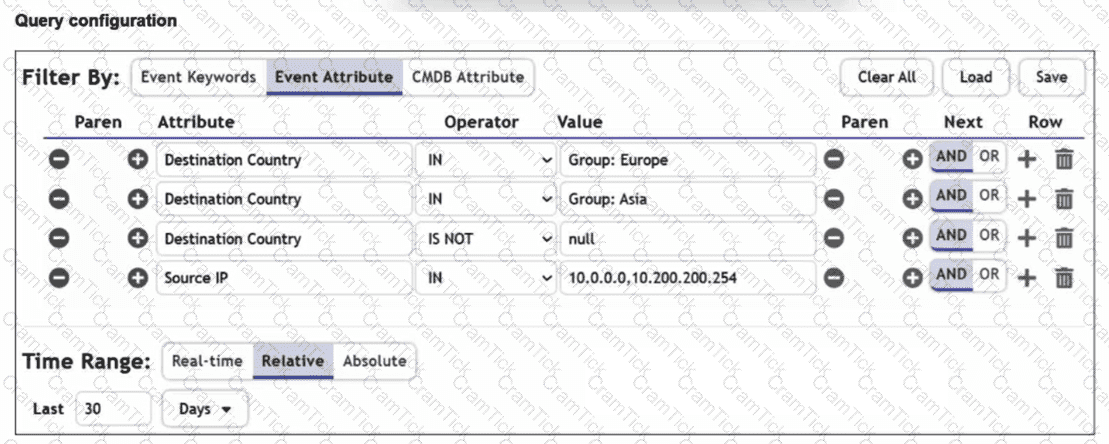
Refer to the exhibit.

You are trying to find traffic flows to destinations that are in Europe or Asia, for hosts in the local LAN segment. However, the query returns no results. Assume these logs exist on FortiSIEM.

Which three mistakes can you see in the query shown in the exhibit? (Choose three answers)

Options:

A.

The null value cannot be used with the IS NOT operator.

B.

The time range must be Absolute for queries that use configuration management database (CMDB) groups.

C.

There are missing parentheses between the first row (Group: Europe) and the second row (Group: Asia).

D.

The Source IP row operator must be BETWEEN 10.0.0.0, 10.200.200.254.

E.

The logical operator for the first row (Group: Europe) must be OR.

Buy Now
Questions 28

Which two ways can you create an incident on FortiAnalyzer? (Choose two answers)
Options:

A.

Using a custom event handler

B.

Using a connector action

C.

Manually, on the Event Monitor page

D.

By running a playbook

Buy Now
Exam Code: NSE7_SOC_AR-7.6
Exam Name: Fortinet NSE 7 - Security Operations 7.6 Architect
Last Update: Nov 17, 2026
Questions: 96
NSE7_SOC_AR-7.6 pdf

NSE7_SOC_AR-7.6 PDF

$22.5  $89.99
NSE7_SOC_AR-7.6 Engine

NSE7_SOC_AR-7.6 Testing Engine

$26.25  $104.99
NSE7_SOC_AR-7.6 PDF + Engine

NSE7_SOC_AR-7.6 PDF + Testing Engine

$35  $139.99