Your team uses HCP Terraform to manage infrastructure. You need to make a change to an infrastructure stack running in a public cloud. Which pattern follows Infrastructure as Code best practices for making the change?
Which type of block fetches or computes information for use elsewhere in a Terraform configuration?
You’ve enabled DEBUG-level logging for Terraform, and you’d like to send the log data to a file. Which action should you take?
If you don’t use the local Terraform backend, where else can Terraform save resource state?
You have a Terraform configuration that defines a single virtual machine with no references to it, You have run terraform apply to create the resource, and then removed the resource definition from your Terraform configuration file.
What will happen you run terraform apply in the working directory again?
INcheck block ' s assertion fails, Terraform blocks the current operation from executing.
You ' re writing a Terraform configuration that needs to read input from a local file called id_rsa.pub . Which built-in Terraform function can you use to import the file ' s contents as a string?
A senior admin accidentally deleted some of your cloud instances. What will Terraform do when you run terraform apply?
What is the name of the default file where Terraform stores the state?
Type your answer in the field provided. The text field is not case-sensitive and all variations of the correct answer are accepted.
Your Terraform configuration declares a variable. You want to enforce that its value meets your specific requirements, and you want to block the Terraform operation if it does not. What should you add to your configuration?
Which two steps are required to provision new infrastructure in the Terraform workflow? Choose two correct answers.
Which parameters does the import block require? (Pick the 2 correct responses below.)
Which of these actions will prevent two Terraform runs from changing the same state file at the same time?
A module block is shown in the Exhibit space of this page. When you use a module block to reference a module from the Terraform Registry such as the one in the example, how do you specify version 1.0.0 of the module?
If a DevOps team adopts AWS CloudFormation as their standardized method for provisioning public cloud resoruces, which of the following scenarios poses a challenge for this team?
You are updating a child module with the resource block shown in the exhibit below. The public_ip attribute of the resource needs to be accessible to the parent module.
Exhibit:
resource " aws_instance " " example " {
ami = " ami-0a123456789abcdef "
instance_type = " t3.micro "
}
How do you meet this requirement?
When you initialize Terraform, where does it cache modules from the public Terraform Registry?
Your team is using version 3.1.4 of a module from the public Terraform Registry, and they are worried about possible breaking changes in future versions of the module. Which version argument should you add to the module block to prevent newer versions from being used?
When you use a remote backend that needs authentication, HashiCorp recommends that you:
It is best practice to store secret data in the same version control repository as your Terraform configuration.
You add a new provider to your configuration and immediately run terraform apply in the CD using the local backend. Why does the apply fail?
You manage two workspaces in your HCP Terraform organization. The first workspace manages your network configuration. The second workspace manages your compute resources and retrieves values from the networking workspace.
What HCP Terraform feature lets you run an apply operation on the compute workspace every time you update the networking workspace?
You’ve updated your Terraform configuration, and you need to preview the proposed changes to your infrastructure. Which command should you run?
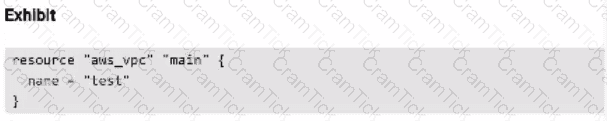
A resource block is shown in the Exhibit space of this page. What is the provider for this resource?
A resource block is shown in the Exhibit space of this page. What is the Terraform resource name of the resource block?
Terraform requires using a different provider for each cloud provider where you want to deploy resources.
You ' re building a CI/CD (continuous integration/continuous delivery) pipeline and need to inject sensitive variables into your Terraform run. How can you do this safely?
Which is a benefit of using infrastructure as code (IaC) tools compared to native platform APIs?
You have just developed a new Terraform configuration for two virtual machines with a cloud provider. You would like to create the infrastructure for the first time.
Which Terraform command should you runfirst?
What type of information can be found on the Terraform Registry when using published modules?
You just scaled your VM infrastructure and realize you set the count variable to the wrong value. You correct the value and save your change. What must you do next to make your infrastructure match your configuration?
You have deployed a new webapp with a public IP address on a cloud provider. However, you did not create any outputs for your code. What is the best method to quickly find the IP address of the resource you deployed?
Which of these are features of HCP Terraform/Terraform Cloud? Pick the 2 correct responses below.
Which of the following does HCP Terraform perform during a health assessment for a workspace?
Which command should you run to check if all code in a Terraform configuration that references multiple modules is properly formatted without making changes?
You must use different Terraform commands depending on the cloud provider you use.
Which command must you first run before performing further Terraform operations in a working directory?
You can execute terraform fmt to standardize all Terraform configurations within the current working directory to Terraform’s canonical format and style.
You are creating a reusable Terraform configuration and want to include an optional billing_dept tag so your Finance team can track team-specific spending on resources. Which of the following billing_dept variable declarations will achieve this?
What is the Terraform style convention for indenting a nesting level compared to the one above it?
You use a cloud provider account that is shared with other team members. You previously used Terraform to create a load balancer that listens on port 80. After application changes, you updated the Terraform code to change the port to 443.
You run terraform plan and see that the execution plan shows the port changing from 80 to 443 like you intended and step away to grab some coffee.
In the meantime, another team member manually changes the load balancer port to 443 through the cloud provider console before you get back to your desk.
What will happen when you run terraform apply upon returning to your desk?
Part of a configuration is shown in the exhibit below.
You want to pass the id of the vsphere_datacenter data source to the datacenter_id argument of the vsphere_folder resource.
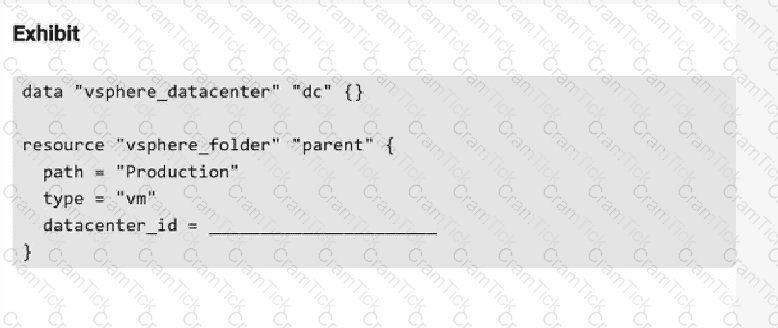 Which reference would you use?
You can reference a resource created with for_each using a Splat ( *) expression.
Which option cannot be used to keep secrets out of Terraform configuration files?
Which option does not keep secret variable values out of Terraform configuration files?
You have multiple team members collaborating on infrastructure as code (IaC) using Terraform, and want to apply formatting standards for readability.
How can you format Terraform HCL (HashiCorp Configuration Language) code according to standard Terraform style convention?
Which of these actions are forbidden when the Terraform state file is locked? (Pick the 3 correct responses)
If you manually destroy infrastructure, what is the best practice reflecting this change in Terraform?
Which method for sharing Terraform configurations fulfills the following criteria:
1. Keeps the configurations confidential within your organization
2. Support Terraform’s semantic version constrains
3. Provides a browsable directory
You want to create a string that is a combination of a generated random_id and a variable, and reuse that string several times in your configuration.
What is the simplest correct way to implement this without repeating the random_id and variable?
As a member of an operations team that uses infrastructure as code (lac) practices, you are tasked with making a change to an infrastructure stack running in a public cloud. Which pattern would follow laC best practices for making a change?
You need to destroy all of the resources in your Terraform workspace, except for aws_instance.ubuntu[1], which you want to keep. How can you tell Terraform to stop managing that specific resource without destroying it?
Where does HashiCorp recommend you store API tokens and other secrets within your team ' s Terraform workspaces?
Pick three correct responses below:
It is __________ to change the Terraform backend from the default local backend to a different backend after performing your first terraform apply.
You have set the TF_LOG_PATH environment variable for Terraform, and you would like to ensure the logs contain all debug-level messages and verbose process logs.
Which action should you take?
The exhibit below shows part of a Terraform configuration you have been asked to update. The name of the Azure Virtual Network should be set to the name of the resource group followed by a dash and the word vnet.
Exhibit:
data " azurerm_resource_group " " example " {
name = var.resource_group_name
}
resource " azurerm_virtual_network " " example " {
name = ______________________
}
Which expression fulfills this requirement?
Why is it considered important to treat your Terraform state file as sensitive?
Which argument can you set on a module block to prevent Terraform from updating the module’s configuration during an init or get operation?
When using Terraform to deploy resources into Azure, which scenarios are true regarding state files? (Choose two.)
Which of the following ate advantages of using infrastructure as code (laC) instead of provisioning with a graphical user interface (GUI)? Choose two correct answers.
Which of these are benefits of using Sentinel with HCP Terraform/Terraform Cloud? (Pick the 3 correct responses)
What information does the public Terraform Module Registry automatically expose about published modules?
Which of the following can you do with terraform plan?
Pick the two correct responses below.
A Terraform backend determines how Terraform loads state and stores updates when you execute which command?
You created infrastructure outside the Terraform workflow that you now want to manage using Terraform. Which command brings the infrastructure into Terraform state?
Outside of the required_providers block, Terraform configurations always refer to providers by their local names.
You used Terraform to create an ephemeral development environment in the cloud and are now ready to destroy all the infrastructure described by your Terraform configuration. To be safe, you would like to first see all the infrastructure that Terraform will delete.
Which command should you use to show all the resources that will be deleted? (Pick the 2 correct responses)
You have a list of numbers representing the number of free CPU cores on each virtual cluster:
numcpus = [18, 3, 7, 11, 2]
Which Terraform built-in function would you use to select the largest number from the list?
Which of the following is true about terraform apply?(Pick 2 correct responses)
You are tasked with making a change to an infrastructure stack running in a public cloud using HCP Terraform/Terraform Cloud. Which pattern follows IaC best practices?
What does Terraform use to deploy infrastructure for different cloud providers?
If one of your modules uses a local value, you can expose that value to callers of the module by defining a Terraform output in the module’s configuration.
Which of these ate secure options for storing secrets for connecting to a Terraform remote backend? Choose two correct answers.
Changing the Terraform backend from the default " local " backend to a different one after performing your first terrafom apply is:
What command can you run to generateDOT (Graphviz)formatted data to visualize Terraform dependencies?
Infrastructure as Code (laC) can be stored in a version control system along with application code.
Your configuration contains a module block that references a module from the Terraform Registry and sets the version argument to 1.0. You just published a new version of the module and updated your configuration to point to version 1.1.
Which command must be run to install the new version?
Where in your Terraform configuration do you specify remote state storage settings?
terraform apply is failing with the following error. What next step should you take to determine the root cause of the problem?
Error:
yaml
CopyEdit
Error loading state: AccessDenied: Access Denied
status code: 403, request id: 288766CE5CCA24A0, host id: web.example.com
terraform apply will fail if you have not run terraform plan first to update the plan output.
You modified your Terraform configuration to fix a typo in the resource ID by renaming it from photoes to photos. What configuration will you add to update the resource ID in state without destroying the existing resource?
Original configuration:
resource " aws_s3_bucket " " photoes " {
bucket_prefix = " images "
}
Updated configuration:
resource " aws_s3_bucket " " photos " {
bucket_prefix = " images "
}
TESTED 03 Oct 2026