You are going to perform a penetration test on a company LAN. As part of your preparation, you access the company’s websites, view webpage source code, and run internet searches to uncover domain information. You also use social media to gather details about the company and its employees.
Which type of reconnaissance activities are you performing?
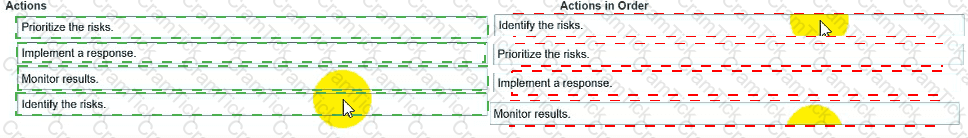
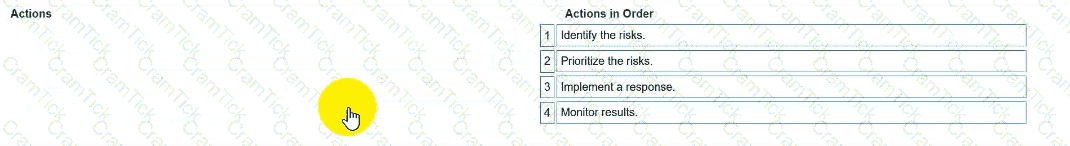
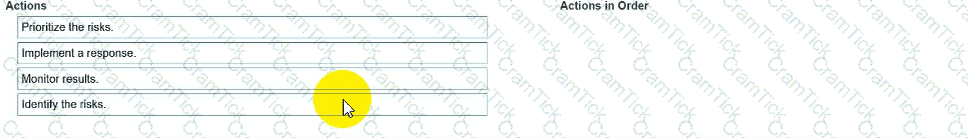
You need to manage security risks at your company. In which order should you complete the actions?
Move all the actions to the answer area and place them in the correct order.
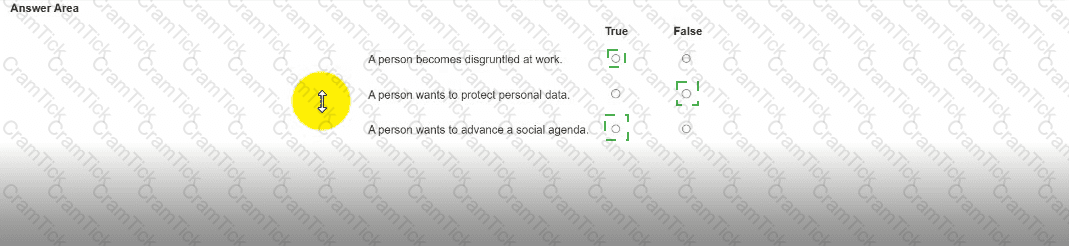
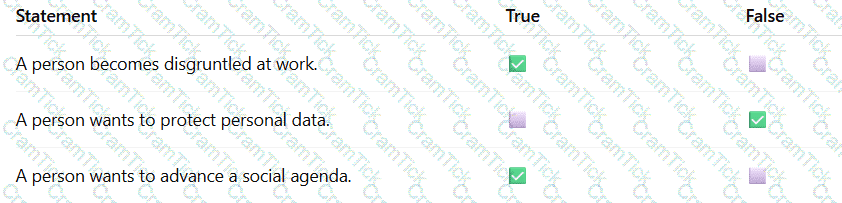
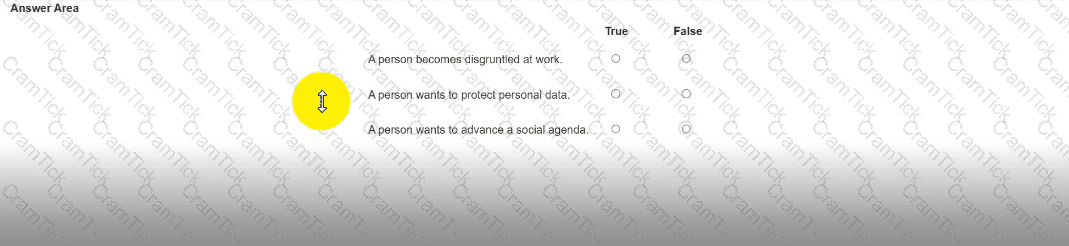
For each statement, select True if it is a common motivation to commit cyber attacks or False if it is not.
Note: You will receive partial credit for each correct selection.
What is the main purpose of a disaster recovery plan as compared to a business continuity plan?
A security assessment reveals that a system administrator accessed files outside normal working hours. The assessment identifies the commands executed and records how long the administrator was connected to the system.
Which AAA component does this represent?
Which activity performed by an adversary is an example of an exploit attempting to obtain user credentials?
Your supervisor suspects that someone is attempting to gain access to a Windows computer by guessing user account IDs and passwords. The supervisor asks you to use the Windows Event Viewer security logs to verify the attempts.
Which two audit policy events provide information to determine whether someone is using invalid credentials to attempt to log in to the computer? (Choose 2.)
Note: You will receive partial credit for each correct selection.
An administrator wants to ensure that any files downloaded from the internet are automatically scanned for malicious code before execution. Which security control should be implemented?
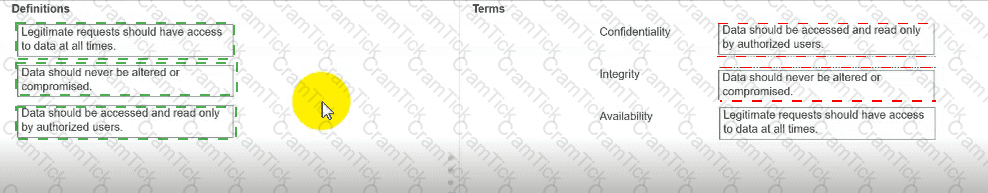
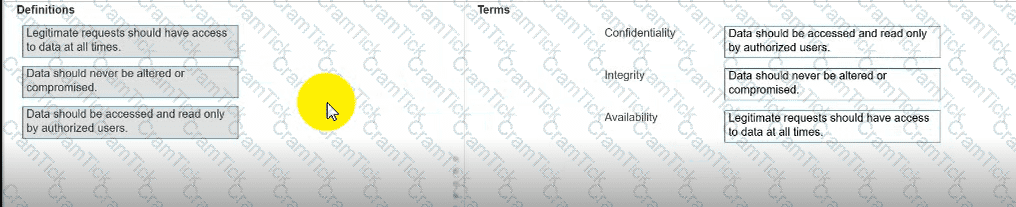
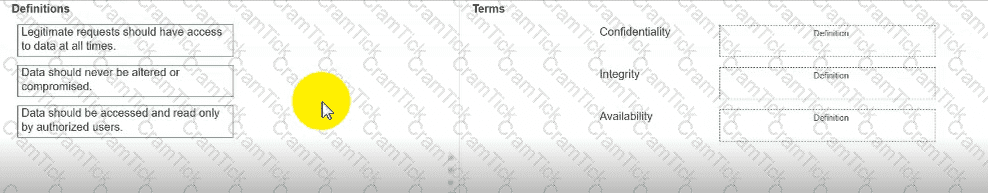
Move each definition from the list on the left to the correct CIA Triad term on the right.
Note: You will receive partial credit for each correct answer.
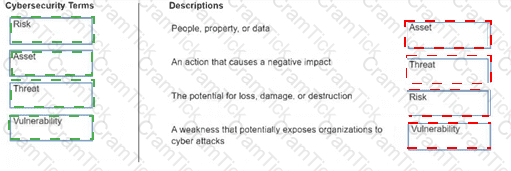
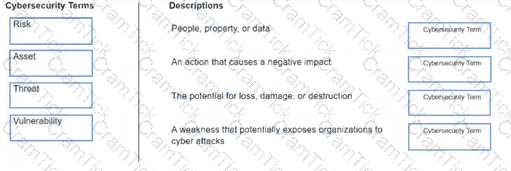
Move each cybersecurity term from the list on the left to the correct description on the right.
Note: You will receive partial credit for each correct answer.
A remote worker is visiting a branch office to attend face-to-face meetings. The worker tries to associate their company laptop with the branch wireless access point (WAP) but is unable to do so.
What is a possible cause?
A corporation hires a group of experienced cybercriminals to establish a prolonged and extensive presence within a competitor ' s network. This access will allow the corporation to steal or sabotage sensitive data belonging to its competitor.
Which type of attack does this scenario describe?
Which step should be performed immediately after identifying a critical vulnerability affecting internet-facing systems?
Your manager asks you to review the output of some vulnerability scans and report anything that may require escalation.
Which two findings should you report for further investigation as potential security vulnerabilities? (Choose 2.)
You are collecting data after a suspected intrusion on the local LAN.
You need to capture incoming IP packets to a file for an investigator to analyze.
Which two tools should you use? (Choose 2.)
CCST |
TESTED 19 Nov 2026