Pre-Winter Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cramtick70

300-710 Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Questions and Answers

Questions 4

An engineer must configure a correlation policy in Cisco Secure Firewall Management Center to detect when an IP address from an internal network communicates with a known malicious host. Connections made by the internal IP addresses must be tracked, and an external dynamic list must be used for the condition. Which type of event must the engineer configure on the correlation policy?

Options:

A.

Intrusion Impact Alert

B.

Connection tracker

C.

Network discovery

D.

Malware

Buy Now
Questions 5

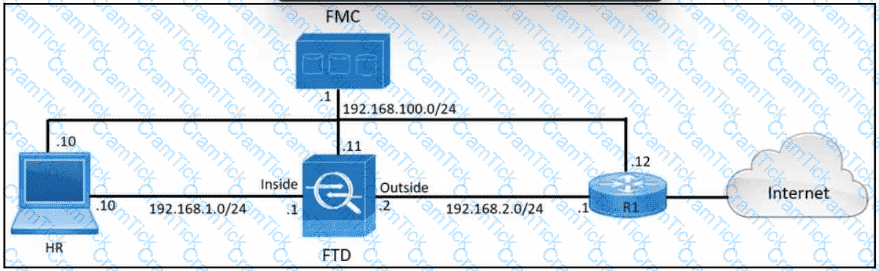
Refer to the exhibit.

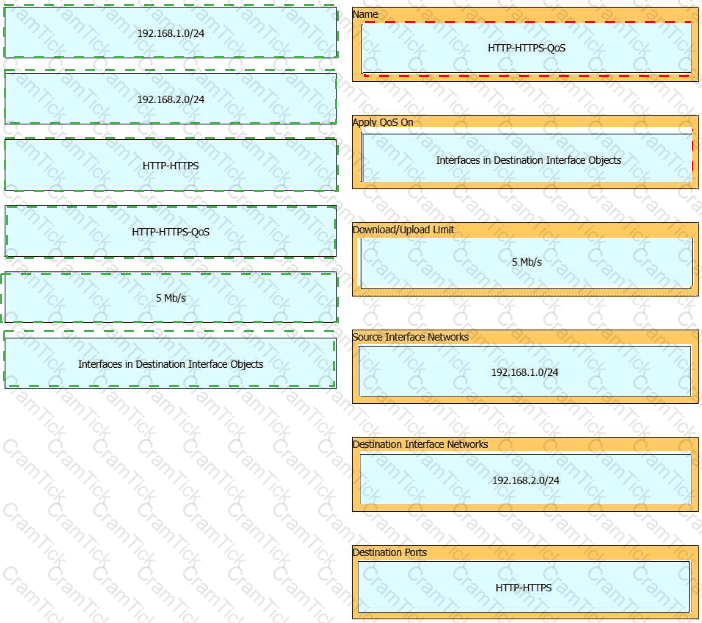
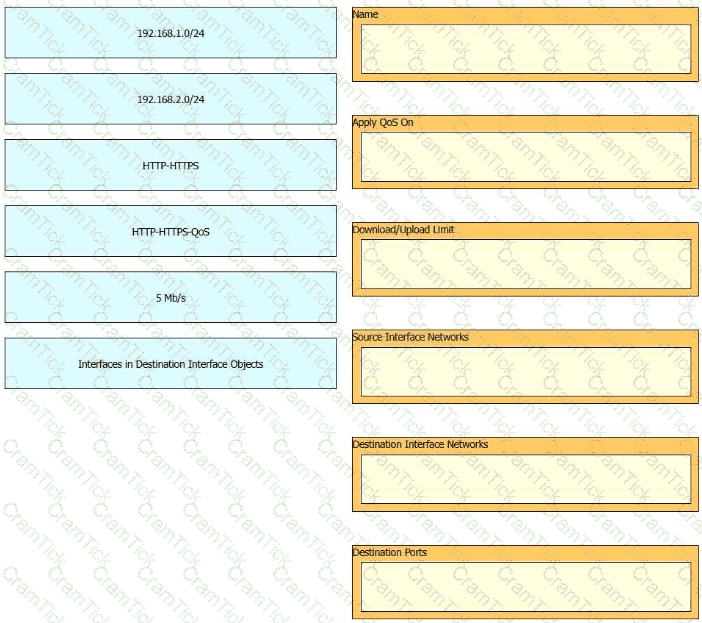
An engineer must create a QoS policy in Cisco Secure Firewall Management Center to limit HTTP and HTTPS traffic originating from users in the HR department. The download and upload limits for HTTP and HTTPS traffic must both be set to 5 Mb/s. Drag and drop the values onto the corresponding QoS rule settings.
Options:

Buy Now
Questions 6

A network administrator is reviewing a monthly advanced malware risk report and notices a host that Is listed as CnC Connected. Where must the administrator look within Cisco FMC to further determine if this host is infected with malware?

Options:

A.

Analysis > Hosts > indications of Compromise

B.

Analysts > Files > Malware Events

C.

Analysis > Hosts > Host Attributes

D.

Analysis > Flies > Network File Trajectory

Buy Now
Questions 7

An engineer configures a network discovery policy on Cisco FMC. Upon configuration, it is noticed that excessive and misleading events filing the database and overloading the Cisco FMC. A monitored NAT device is executing multiple updates of its operating system in a short period of time. What configurationchange must be made to alleviate this issue?

Options:

A.

Leave default networks.

B.

Change the method to TCP/SYN.

C.

Increase the number of entries on the NAT device.

D.

Exclude load balancers and NAT devices.

Buy Now
Questions 8

A network administrator notices that remote access VPN users are not reachable from inside the network. It is determined that routing is configured correctly, however return traffic is entering the firewall but not leaving it What is the reason for this issue?

Options:

A.

A manual NAT exemption rule does not exist at the top of the NAT table.

B.

An external NAT IP address is not configured.

C.

An external NAT IP address is configured to match the wrong interface.

D.

An object NAT exemption rule does not exist at the top of the NAT table.

Buy Now
Questions 9

A network engineer wants to add a third-party threat feed into the Cisco FMC for enhanced threat detectionWhich action should be taken to accomplish this goal?

Options:

A.

Enable Threat Intelligence Director using STIX and TAXII

B.

Enable Rapid Threat Containment using REST APIs

C.

Enable Threat Intelligence Director using REST APIs

D.

Enable Rapid Threat Containment using STIX and TAXII

Buy Now
Questions 10

A network administrator reviews me attack risk report and notices several Low-Impact attacks. What does this type of attack indicate?

Options:

A.

All attacks are listed as low until manually categorized.

B.

The host is not vulnerable to those attacks.

C.

The attacks are not dangerous to the network.

D.

The host is not within the administrator ' s environment.

Buy Now
Questions 11

A network administrator is seeing an unknown verdict for a file detected by Cisco FTD. Which malware policy configuration option must be selected in order to further analyse the file in the Talos cloud?

Options:

A.

Spero analysis

B.

Malware analysis

C.

Dynamic analysis

D.

Sandbox analysis

Buy Now
Questions 12

A network administrator cannot select the link to be used for failover when configuring an active/passive HA Cisco FTD pair.

Which configuration must be changed before setting up the high availability pair?

Options:

A.

An IP address in the same subnet must be added to each Cisco FTD on the interface.

B.

The interface name must be removed from the interface on each Cisco FTD.

C.

The name Failover must be configured manually on the interface on each cisco FTD.

D.

The interface must be configured as part of a LACP Active/Active EtherChannel.

Buy Now
Questions 13

An organization does not want to use the default Cisco Firepower block page when blocking HTTP traffic. The organization wants to include information about its policies and procedures to help educate the users whenever a block occurs. Which two steps must be taken to meet these requirements? (Choose two.)
Options:

A.

Modify the system-provided block page result using Python.

B.

Create HTML code with the information for the policies and procedures.

C.

Edit the HTTP request handling in the access control policy to customized block.

D.

Write CSS code with the information for the policies and procedures.

E.

Change the HTTP response in the access control policy to custom.

Buy Now
Questions 14

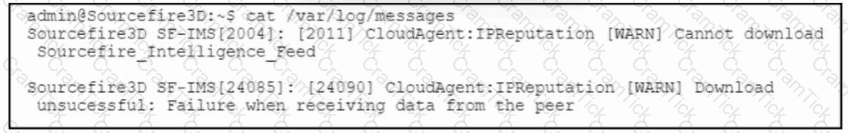
Refer to the exhibit. A Cisco Secure Firewall Management Center, 7.0 device fails to receive intelligence feed updates. The Cisco Secure Firewall Management Center is configured to use a proxy server that performs SSL inspection. Which action allows the Cisco Secure Firewall Management Center device to download the intelligence feed updates?

Options:

A.

Install a self-signed certificate on the proxy server for intelligence.sourcefire.com.

B.

Verify that the proxy server can use HTTPS to communicate to the internet.

C.

Ensure that proxy authentication is disabled for the Cisco Secure Firewall Management Center device.

D.

Bypass the proxy server for intelligence.sourcefire.com.

Buy Now
Questions 15

An engineer is attempting to create a new dashboard within the Cisco FMC to have a single view with widgets from many of the other dashboards. The goal is to have a mixture of threat and security related widgets along with Cisco Firepower device health information. Which two widgets must be configured to provide this information? (Choose two).

Options:

A.

Intrusion Events

B.

Correlation Information

C.

Appliance Status

D.

Current Sessions

E.

Network Compliance

Buy Now
Questions 16

Cisco Security Analytics and Logging SaaS licenses come with how many days of data retention by default?

Options:

A.

60

B.

365

C.

90

D.

120

Buy Now
Questions 17

A security engineer is configuring a remote Cisco FTD that has limited resources and internet bandwidth. Which malware action and protection option should be configured to reduce the requirement for cloud lookups?

Options:

A.

Malware Cloud Lookup and dynamic analysis

B.

Block Malware action and dynamic analysis

C.

Block Malware action and local malware analysis

D.

Block File action and local malware analysis

Buy Now
Questions 18

What is a characteristic of bridge groups on a Cisco FTD?

Options:

A.

In routed firewall mode, routing between bridge groups must pass through a routed interface.

B.

In routed firewall mode, routing between bridge groups is supported.

C.

In transparent firewall mode, routing between bridge groups is supported

D.

Routing between bridge groups is achieved only with a router-on-a-stick configuration on a connected router

Buy Now
Questions 19

A network engineer must provide a high-level statistical summary of a Cisco Secure Firewall Threat Defense device. The organization is approaching its peak season, so network downtime must be minimized. Which type of report must the network engineer use?

Options:

A.

Malware

B.

SNMP

C.

Risk

D.

Host

Buy Now
Questions 20

A security engineer must configure a Cisco FTD appliance to inspect traffic coming from the internet. The Internet traffic will be mirrored from the Cisco Catalyst 9300 Switch. Which configuration accomplishes the task?

Options:

A.

Set interface configuration mode to none.

B.

Set the firewall mode to transparent.

C.

Set the firewall mode to routed.

D.

Set interface configuration mode to passive.

Buy Now
Questions 21

A security administrator must configure Cisco Secure Firewall Management Center so that certain intrusion rules are active only during specified times. Which action must the administrator take?

Options:

A.

Assign a time range directly to every intrusion rule in the intrusion policy.

B.

Configure a time-based trigger in the intrusion policy to enable the rules at defined times.

C.

Create time-based access control rules that apply the intrusion policy at the scheduled intervals.

D.

Create a scheduled task that activates and deactivates the intrusion rules at the required times.

Buy Now
Questions 22

An engineer is attempting to add a new FTD device to their FMC behind a NAT device with a NAT ID of ACME001 and a password of Cisco388267669. Which command set must be used in order to accomplish this?

Options:

A.

configure manager add ACME001 < registration key > < FMC IP >

B.

configure manager add < FMC IP > ACME0O1 < registration key >

C.

configure manager add DONTRESOLVE < FMC IP > AMCE001 < registration key >

D.

configure manager add < FMC IP > registration key > ACME001

Buy Now
Questions 23

An engineer must configure a passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:

•Set the interface mode to Passive.

•Configure the MTU.

•Set the speed and duplex. Which action completes the configuration?

Options:

A.

Reset the NGIPS

B.

Reregister the NGIPS.

C.

Enable the bridge virtual interface.

D.

Enable the interface.

Buy Now
Questions 24

Which command is typed at the CLI on the primary Cisco FTD unit to temporarily stop running high- availability?

Options:

A.

configure high-availability resume

B.

configure high-availability disable

C.

system support network-options

D.

configure high-availability suspend

Buy Now
Questions 25

Which Cisco Firepower rule action displays an HTTP warning page?

Options:

A.

Monitor

B.

Block

C.

Interactive Block

D.

Allow with Warning

Buy Now
Questions 26

An engineer must block all the web traffic that targets an IP address instead of the associated hostname by using Secure Firewall Management Center. Access control, intrusion, and file policies have been configured; however, specific web traffic that has been identified is still coming through Which configuration must be done next for protection?

Options:

A.

application detector

B.

SNMP alert

C.

correlation policy

D.

NMAPscan

Buy Now
Questions 27

Which Cisco Secure Firewall Threat Defense interface mode must be deployed when implementing an IPS that uses a SPAN port for traffic monitoring?

Options:

A.

Routed

B.

Passive

C.

Transparent

D.

Inline

Buy Now
Questions 28

An engineer has been asked to show application usages automatically on a monthly basis and send the information to management What mechanism should be used to accomplish this task?

Options:

A.

event viewer

B.

reports

C.

dashboards

D.

context explorer

Buy Now
Questions 29

What is the result when two users modify a VPN policy at the same lime on a Cisco Secure Firewall Management Center managed device?
Options:

A.

Both users can edit the policy arid the last saved configuration persists.

B.

The first user locks the configuration when selecting edit on the policy.

C.

The changes from both users will be merged together into the policy.

D.

The system prevents modifications to the policy by multiple users.

Buy Now
Questions 30

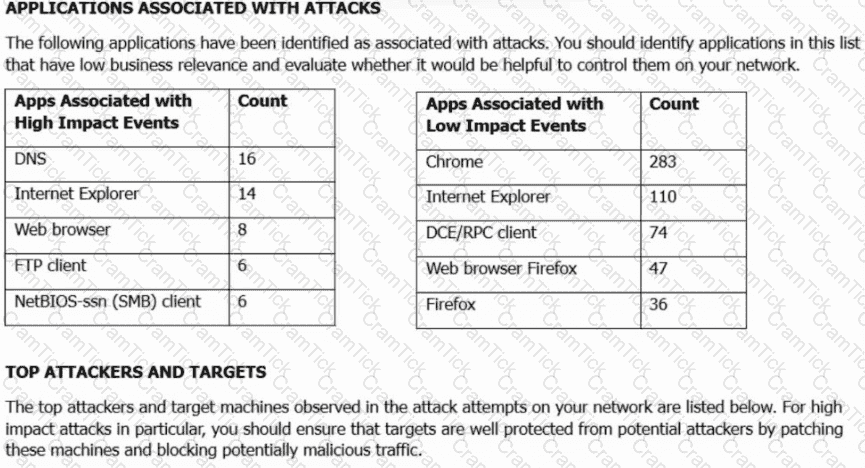
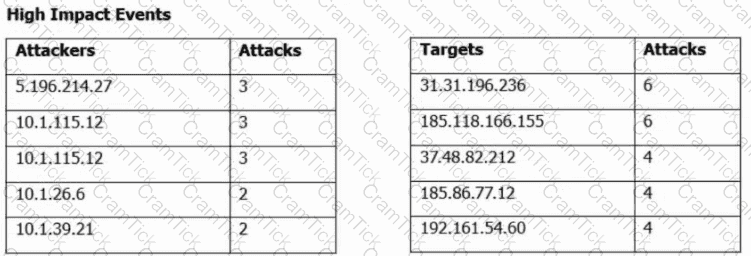
Refer to the exhibit. A security engineer must improve security in an organization and is producing a risk mitigation strategy to present to management for approval. Which action must the security engineer take based on this Attacks Risk Report?

Options:

A.

Block Internet Explorer.

B.

Block NetBIOS.

C.

Inspect TCP port 80 traffic.

D.

Inspect DNS traffic.

Buy Now
Questions 31

A security engineer wants to add the Interface Traffic widget to the Summary Dashboard in Cisco Secure Firewall Management Center. The engineer clicks Add Widgets and enters edit mode. Which set of actions must the security engineer take to complete the configuration?

Options:

A.

Click All Categories, open the Analysis & Reporting tab, and then click the Add widget button.

B.

Click All Categories, open the New tab, and then click the Add widget button.

C.

Click All Categories, open the Operations tab, and then click the Add widget button.

D.

Click All Categories, open the Miscellaneous tab, and then click the Add widget button.

Buy Now
Questions 32

On the advanced tab under inline set properties, which allows interfaces to emulate a passive interface?

Options:

A.

transparent inline mode

B.

TAP mode

C.

strict TCP enforcement

D.

propagate link state

Buy Now
Questions 33

A network administrator reviews the file report for the last month and notices that all file types, except exe. show a disposition of unknown. What is the cause of this issue?

Options:

A.

The malware license has not been applied to the Cisco FTD.

B.

The Cisco FMC cannot reach the Internet to analyze files.

C.

A file policy has not been applied to the access policy.

D.

Only Spero file analysis is enabled.

Buy Now
Questions 34

A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface. What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?

Options:

A.

Only the UDP packet type is supported.

B.

The output format option for the packet logs is unavailable.

C.

The destination MAC address is optional if a VLAN ID value is entered.

D.

The VLAN ID and destination MAC address are optional.

Buy Now
Questions 35

When a Cisco FTD device is configured in transparent firewall mode, on which two interface types can an IP address be configured? (Choose two.)

Options:

A.

Diagnostic

B.

EtherChannel

C.

BVI

D.

Physical

E.

Subinterface

Buy Now
Questions 36

What is the benefit of selecting the trace option for packet capture?

Options:

A.

The option indicates whether the packet was dropped or successful.

B.

The option indicated whether the destination host responds through a different path.

C.

The option limits the number of packets that are captured.

D.

The option captures details of each packet.

Buy Now
Questions 37

An engineer must export a packet capture from Cisco Secure Firewall Management Center to assist in troubleshooting an issue an a Secure Firewall Threat Defense device. When the engineer navigates to URL for Secure Firewall Management Center at:

.. < FMC IP > /capture/CAP/pcap/sample.pcap

An engineer receives a 403: Forbidden error instead of being provided with the PCAP file. Which action resolves the issue?

Options:

A.

Disable the HTTPS server and use HTTP.

B.

Enable the proxy setting in the device platform policy.

C.

Enable HTTPS in the device platform policy.

D.

Disable the proxy setting on the client browser.

Buy Now
Questions 38

An engineer must configure an ERSPAN passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:

Configure the passive interface.

Configure the ERSPAN IP address.

Which two additional settings must be configured to complete the configuration? (Choose two.)

Options:

A.

Source IP

B.

Bypass Mode

C.

TCP Intercept

D.

Flow ID

E.

Destination MAC

Buy Now
Questions 39

An engineer wants to add an additional Cisco FTD Version 6.2.3 device to their current 6.2.3 deployment to create a high availability pair.

The currently deployed Cisco FTD device is using local management and identical hardware including the available port density to enable the failover and stateful links required in a proper high availability deployment. Which action ensures that the environment is ready to pair the new Cisco FTD with the old one?

Options:

A.

Change from Cisco FDM management to Cisco FMC management on both devices and register them to FMC.

B.

Ensure that the two devices are assigned IP addresses from the 169 254.0.0/16 range for failoverinterfaces.

C.

Factory reset the current Cisco FTD so that it can synchronize configurations with the new Cisco FTDdevice.

D.

Ensure that the configured DNS servers match on the two devices for name resolution.

Buy Now
Questions 40

Which two routing options are valid with Cisco Firepower Threat Defense? (Choose two.)

Options:

A.

BGPv6

B.

ECMP with up to three equal cost paths across multiple interfaces

C.

ECMP with up to three equal cost paths across a single interface

D.

BGPv4 in transparent firewall mode

E.

BGPv4 with nonstop forwarding

Buy Now
Questions 41

An engineer wants to convert a Cisco Secure Firewall Threat Defense device that is currently managed by Cisco Secure Firewall Management Center from routed mode to transparent mode. Which CLI command must the engineer execute first to perform this conversion?

Options:

A.

no configure manager

B.

no configure firewall routed

C.

configure manager delete

D.

configure firewall transparent

Buy Now
Questions 42

Which Cisco Firepower feature is used to reduce the number of events received in a period of time?

Options:

A.

rate-limiting

B.

suspending

C.

correlation

D.

thresholding

Buy Now
Questions 43

A company has many Cisco FTD devices managed by a Cisco FMC. The security model requires that access control rule logs be collected for analysis. The security engineer is concerned that the Cisco FMC will not be able to process the volume of logging that will be generated. Which configuration addresses this concern?

Options:

A.

Send Cisco FTD connection events and security events directly to SIEM system for storage and analysis.

B.

Send Cisco FTD connection events and security events to a cluster of Cisco FMC devices for storage and analysis.

C.

Send Cisco FTD connection events and security events to Cisco FMC and configure it to forward logs to SIEM for storage and analysis.

D.

Send Cisco FTD connection events directly to a SIEM system and forward security events from Cisco FMC to the SIEM system for storage and analysis.

Buy Now
Questions 44

When using Cisco Threat Response, which phase of the Intelligence Cycle publishes the results of the investigation?

Options:

A.

direction

B.

dissemination

C.

processing

D.

analysis

Buy Now
Questions 45

Within Cisco Firepower Management Center, where does a user add or modify widgets?

Options:

A.

dashboard

B.

reporting

C.

context explorer

D.

summary tool

Buy Now
Questions 46

Which interface type allows packets to be dropped?

Options:

A.

passive

B.

inline

C.

ERSPAN

D.

TAP

Buy Now
Questions 47

An engineer must integrate a thud-party security Intelligence teed with Cisco Secure Firewall Management Center. Secure Firewall Management Center is running Version 6.2 3 and has 8 GB of memory. Which two actions must be taken to implement Throat Intelligence Director? (Choose two.)

Options:

A.

Upgrade to version 6.6.

B.

Enable REST API access.

C.

Add the URL of the TAXII server.

D.

Add 7 GB of memory.

E.

Add a TAXII server

Buy Now
Questions 48

What is a feature of Cisco AMP private cloud?

Options:

A.

It supports anonymized retrieval of threat intelligence

B.

It supports security intelligence filtering.

C.

It disables direct connections to the public cloud.

D.

It performs dynamic analysis

Buy Now
Questions 49

An engineer runs the command restore remote-manager-backup location 2.2.2.2 admin /Volume/home/admin FTD408566513.zip on a Cisco FMC. After connecting to the repository, the Cisco FTD device is unable to accept the backup file. What is the reason for this failure?

Options:

A.

The backup file is not in .cfg format.

B.

The wrong IP address is used.

C.

The backup file extension was changed from .tar to .zip.

D.

The directory location is incorrect.

Buy Now
Questions 50

Which two features of Cisco AMP for Endpoints allow for an uploaded file to be blocked? (Choose two.)

Options:

A.

application blocking

B.

simple custom detection

C.

file repository

D.

exclusions

E.

application whitelisting

Buy Now
Questions 51

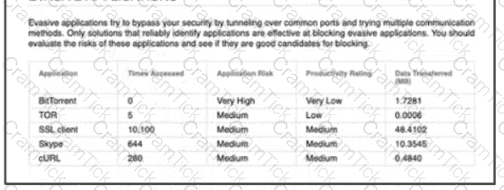
An analyst is reviewing the Cisco FMC reports for the week. They notice that some peer-to-peer applications are being used on the network and they must identify which poses the greatest risk to the environment. Which report gives the analyst this information?
Options:

A.

Attacks Risk Report

B.

User Risk Report

C.

Network Risk Report

D.

Advanced Malware Risk Report

Buy Now
Questions 52

Refertothe exhibit. An engineer is analyzing a Network Risk Report from Cisco FMC. Which application must the engineer take immediate action against to prevent unauthorized network use?

Options:

A.

Kerberos

B.

YouTube

C.

Chrome

D.

TOR

Buy Now
Questions 53

An administrator receives reports that users cannot access a cloud-hosted web server. The access control policy was recently updated with several new policy additions and URL filtering. What must be done to troubleshoot the issue and restore access without sacrificing the organization ' s security posture?

Options:

A.

Create a new access control policy rule to allow ports 80 and 443 to the FQDN of the web server.

B.

Identify the blocked traffic in the Cisco FMC connection events to validate the block, and modify the policy to allow the traffic to the web server.

C.

Verify the blocks using the packet capture tool and create a rule with the action monitor for the traffic.

D.

Download a PCAP of the traffic attempts to verify the blocks and use the flexconfig objects to create a rule that allows only the required traffic to the destination server.

Buy Now
Questions 54

The CEO ask a network administrator to present to management a dashboard that shows custom analysis tables for the top DNS queries URL category statistics, and the URL reputation statistics.

Which action must the administrator take to quickly produce this information for management?

Options:

A.

Run the Attack report and filter on DNS to show this information.

B.

Create a new dashboard and add three custom analysis widgets that specify the tables needed.

C.

Modify the Connection Events dashboard to display the information in a view for management.

D.

Copy the intrusion events dashboard tab and modify each widget to show the correct charts.

Buy Now
Questions 55

What is a valid Cisco AMP file disposition?

Options:

A.

non-malicious

B.

malware

C.

known-good

D.

pristine

Buy Now
Questions 56

An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration takes must be performed to achieve this file lookup? (Choose two.)

Options:

A.

The Cisco FMC needs to include a SSL decryption policy.

B.

The Cisco FMC needs to connect to the Cisco AMP for Endpoints service.

C.

The Cisco FMC needs to connect to the Cisco ThreatGrid service directly for sandboxing.

D.

The Cisco FMC needs to connect with the FireAMP Cloud.

E.

The Cisco FMC needs to include a file inspection policy for malware lookup.

Buy Now
Questions 57

A user within an organization opened a malicious file on a workstation which in turn caused a ransomware attack on the network. What should be configured within the Cisco FMC to ensure the file is tested for viruses on a sandbox system?

Options:

A.

Capacity handling

B.

Local malware analysis

C.

Spere analysis

D.

Dynamic analysis

Buy Now
Questions 58

A network administrator is concerned about (he high number of malware files affecting users ' machines. What must be done within the access control policy in Cisco FMC to address this concern?

Options:

A.

Create an intrusion policy and set the access control policy to block.

B.

Create an intrusion policy and set the access control policy to allow.

C.

Create a file policy and set the access control policy to allow.

D.

Create a file policy and set the access control policy to block.

Buy Now
Questions 59

An organization is implementing Cisco FTD using transparent mode in the network. Which rule in the default Access Control Policy ensures that this deployment does not create a loop in the network?

Options:

A.

ARP inspection is enabled by default.

B.

Multicast and broadcast packets are denied by default.

C.

STP BPDU packets are allowed by default.

D.

ARP packets are allowed by default.

Buy Now
Questions 60

In which two places can thresholding settings be configured? (Choose two.)

Options:

A.

on each IPS rule

B.

globally, within the network analysis policy

C.

globally, per intrusion policy

D.

on each access control rule

E.

per preprocessor, within the network analysis policy

Buy Now
Questions 61

An administrator must use Cisco FMC to install a backup route within the Cisco FTD to route traffic in case of a routing failure with the primary route. Which action accomplishes this task?

Options:

A.

Install the static backup route and modify the metric to be less than the primary route.

B.

Configure EIGRP routing on the FMC to ensure that dynamic routes are always updated.

C.

Use a default route on the FMC instead of having multiple routes contending for priority.

D.

Create the backup route and use route tracking on both routes to a destination IP address in the network.

Buy Now
Questions 62

Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session. Which action must the engineer take to resolve the issue?

Options:

A.

Forward the captured data lo an FTP server

B.

Increase the amount of RAM allocated for the capture.

C.

Provide a file name to save the data.

D.

Ensure that the allocated memory is sufficient.

Buy Now
Questions 63

The network administrator wants to enhance the network security posture by enabling machine learning tor malware detection due to a concern with suspicious Microsoft executable file types that were seen while creating monthly security reports for the CIO. Which feature must be enabled to accomplish this goal?

Options:

A.

Spero

B.

dynamic analysis

C.

static analysis

D.

Ethos

Buy Now
Questions 64

A security engineer is deploying a Cisco Secure Firewall Threat Defense device through Cisco Secure Firewall Management Center. The Threat license is installed, the Encrypted Visibility Engine is enabled in the access control policy Decryption policy is configured with the Decrypt - Resign action to inspect outbound TLS/SSL traffic. Users report that a banking applications repeatedly fails to load. The engineer confirms the endpoint performs certificate pinning to validate the server certificate. Engineer must allow the traffic to pass while all other outbound traffic continues to be inspected. The engineer created a rule that matches banking category and placed the rule above Decrypt - Resign policy. Which decryption rule action must be configured to meet the requirement?

Options:

A.

Decrypt - Known Key

B.

Do Not Decrypt

C.

Trust

D.

Block

Buy Now
Questions 65

After using Firepower for some time and learning about how it interacts with the network, an administrator is trying to correlate malicious activity with a user Which widget should be configured to provide this visibility on the Cisco Firepower dashboards?

Options:

A.

Custom Analysis

B.

Current Status

C.

Current Sessions

D.

Correlation Events

Buy Now
Questions 66

An engineer is troubleshooting an intermittent connectivity issue on a Cisco Secure Firewall Threat Defense appliance and must collect 24 hours worth of data. The engineer started a packet capture, however it stops prematurely during this time period. The engineer notices that the packet capture buffer size is set to the default of 32 MB. Which buffer size is the maximum that the engineer must set to enable the packet capture to run successfully?

Options:

A.

64 MB

B.

1 GB

C.

10 GB

D.

100 GB

Buy Now
Questions 67

A large online retailer places Cisco Secure Firewall NGIPS Inline between core and edge firewalls. Seasonal promotions generate sudden traffic spikes that occasionally overwhelm the inspection engine. The device must automatically forward packets uninspected during the overload periods while resuming normal analysis and blocking afterward. Which configuration action must be done to meet the requirement?

Options:

A.

enable Snort Fail Open

B.

configure LINA Failsafe

C.

increase capture buffer size

D.

switch inline interface pair to tap mode

Buy Now
Questions 68

A network engineer must configure IPS mode on a Cisco Secure firewall Threat Defense device to inspect traffic and act as an IDS. The engineer already configured the passive-interface on the secure firewall threat Defence device and SPAN on the switch. What must be configured next by the engineer?

Options:

A.

intrusion policy on the Secure Firewall Threat Defense device

B.

active Interface on me Secure Firewall threat Defense device

C.

DHCP on the switch

D.

active SPAN port on the switch

Buy Now
Questions 69

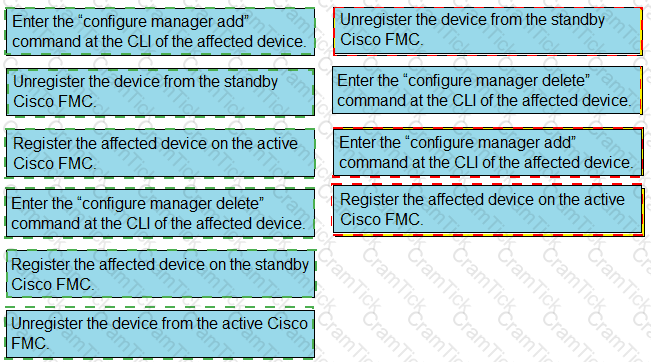
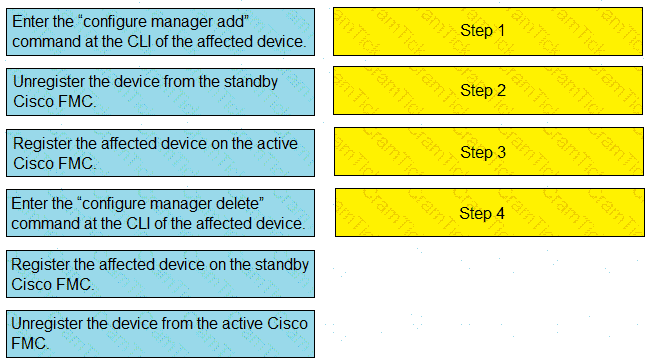
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
Options:

Buy Now
Questions 70

Which limitation applies to Cisco Firepower Management Center dashboards in a multidomain environment?

Options:

A.

Child domains can view but not edit dashboards that originate from an ancestor domain.

B.

Child domains have access to only a limited set of widgets from ancestor domains.

C.

Only the administrator of the top ancestor domain can view dashboards.

D.

Child domains cannot view dashboards that originate from an ancestor domain.

Buy Now
Questions 71

An engineer must change the mode of a Cisco Secure Firewall Threat Defense (FTD) firewall in the Cisco Secure Firewall Management Center (FMC) inventory. The engineer must take these actions:

• Register Secure FTD with Secure FMC.

• Change the firewall mode.

• Deregister the Secure FTD device from Secure FMC.

How must the engineer take FTD take the actions?

Options:

A.

Reload the Secure FTD device.

B.

Configure the management IP address.

C.

Access the Secure FTD CLI from the console port.

D.

Erase the Secure FTD configuration

Buy Now
Questions 72

A company is deploying Cisco Secure Endpoint private cloud. The Secure Endpoint private cloud instance has already been deployed by the server administrator. The server administrator provided the hostname of the private cloud instance to the network engineer via email. What additional information does the network engineer require from the server administrator to be able to make the connection to Secure Endpoint private cloud in Cisco Secure Firewall Management Centre?

Options:

A.

SSL certificate for the Secure Endpoint ornate cloud instance

B.

Internet access for the Secure End point private cloud to reach the Secure Endpoint public cloud

C.

Username and password to the Secure Endpoint private cloud instance

D.

IP address and port number for the connection proxy

Buy Now
Questions 73

A network administrator is configuring a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center to exchange routing information with an upstream BGP router. The administrator must verify which networks the device is advertising to the upstream router. Which action must the administrator take?

Options:

A.

Run the show bgp neighbors NEIGHBOR-IP advertised-routes command from Advanced Troubleshooting.

B.

Select Route Inject under the Device Routing configuration of the Secure Firewall Threat Defense device.

C.

Select Route Inject under the Device Routing configuration of Secure Firewall Management Center.

D.

Run the show route command from the Secure Firewall Management Center CLI.

Buy Now
Questions 74

A company wants a solution to aggregate the capacity of two Cisco FTD devices to make the best use of resources such as bandwidth and connections per second. Which order of steps must be taken across the Cisco FTDs with Cisco FMC to meet this requirement?

Options:

A.

Configure the Cisco FTD interfaces, add members to FMC, configure cluster members in FMC, and create cluster in Cisco FMC.

B.

Add members to Cisco FMC, configure Cisco FTD interfaces in Cisco FMC. configure cluster members in Cisco FMC, create cluster in Cisco FMC. and configure cluster members in Cisco FMC.

C.

Configure the Cisco FTD interfaces and cluster members, add members to Cisco FMC. and create the cluster in Cisco FMC.

D.

Add members to the Cisco FMC, configure Cisco FTD interfaces, create the cluster in Cisco FMC, and configure cluster members in Cisco FMC.

Buy Now
Questions 75

Which two solutions are used to access and view aggregated log data from the firewalls using Cisco Security Analytics and Logging? (Choose two.)

Options:

A.

Cisco Secure Network Analytics

B.

Cisco Defense Orchestrator

C.

Cisco Catalyst Center

D.

Secure Cloud Analytics

E.

Cisco Prime Infrastructure

Buy Now
Questions 76

A network administrator observes an attempted attack from a specific IP address in Cisco Secure Firewall Management Center. Which Cisco security tool can be used directly from the Secure Firewall Management Center web interface to obtain additional information about the IP address?

Options:

A.

Cisco Threat Response browser plugin

B.

Cisco Secure Network Analytics

C.

Cisco Identity Services Engine

D.

Cisco Secure Endpoint

Buy Now
Questions 77

A network administrator is troubleshooting access to a website hosted behind a Cisco FTD device External clients cannot access the web server via HTTPS The IP address configured on the web server is 192 168 7.46 The administrator is running the command capture CAP interface outside match ip any 192.168.7.46 255.255.255.255 but cannot see any traffic in the capture Why is this occurring?

Options:

A.

The capture must use the public IP address of the web server.

B.

The FTD has no route to the web server.

C.

Theaccess policy is blocking the traffic.

D.

The packet capture shows only blocked traffic

Buy Now
Questions 78

An engineer must permit SSH on the inside interface of a Cisco Secure Firewall Threat Defense device. SSH is currently permitted only on the management interface. Which type of policy

must the engineer configure?

Options:

A.

platform policy

B.

access control policy

C.

NAT policy

D.

intrusion policy

Buy Now
Questions 79

There is an increased amount of traffic on the network and for compliance reasons, management needs visibility into the encrypted traffic What is a result of enabling TLS ' SSL decryption to allow this visibility?

Options:

A.

It prompts the need for a corporate managed certificate

B.

It has minimal performance impact

C.

It is not subject to any Privacy regulations

D.

It will fail if certificate pinning is not enforced

Buy Now
Questions 80

Remote users who connect via Cisco AnyConnect to the corporate network behind a Cisco FTD device report that they get no audio when calling between remote users using their softphones. These same users can call internal users on the corporate network without any issues. What is the cause of this issue?

Options:

A.

The hairpinning feature is not available on FTD.

B.

Split tunneling is enabled for the Remote Access VPN on FTD

C.

FTDhas no NAT policy that allows outside to outside communication

D.

The Enable Spoke to Spoke Connectivity through Hub option is not selected on FTD.

Buy Now
Questions 81

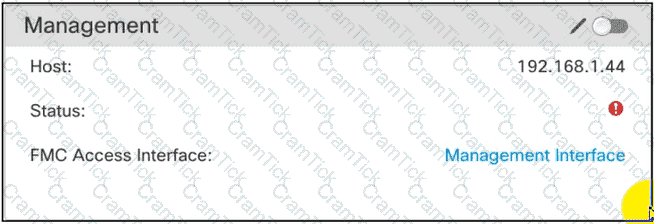
Refer to the exhibit.

What is the effect of the existing Cisco FMC configuration?

Options:

A.

The remote management port for communication between the Cisco FMC and the managed device changes to port 8443.

B.

The managed device is deleted from the Cisco FMC.

C.

The SSL-encrypted communication channel between the Cisco FMC and the managed device becomes plain-text communication channel.

D.

The management connection between the Cisco FMC and the Cisco FTD is disabled.

Buy Now
Questions 82

When an engineer captures traffic on a Cisco FTD to troubleshoot a connectivity problem, they receive a large amount of output data in the GUI tool. The engineer found that viewing the Captures this way is time-consuming and difficult lo son and filter. Which file type must the engineer export the data in so that it can be reviewed using a tool built for this type of analysis?

Options:

A.

NetFlow v9

B.

PCAP

C.

NetFlow v5

D.

IPFIX

Buy Now
Questions 83

A security engineer found a suspicious file from an employee email address and is trying to upload it for analysis, however the upload is failing. The last registration status is still active. What is the cause for this issue?
Options:

A.

Cisco AMP for Networks is unable to contact Cisco Threat Grid on premise.

B.

Cisco AMP for Networks is unable to contact Cisco Threat Grid Cloud.

C.

There is a host limit set.

D.

The user agent status is set to monitor.

Buy Now
Questions 84

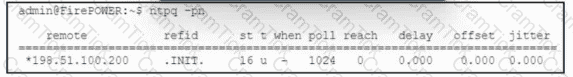
Refer to the exhibit. A security engineer views the health alerts in Cisco Secure Firewall Management Center by using the Health Monitor in the web interface. One of the alerts shows an appliance as critical because the Time Synchronization module status is out of sync. To troubleshoot the issue, the engineer runs the ntpq command in Secure Firewall Management Center. The output is shown in the exhibit. Which action must the security engineer take next to resolve the issue?

Options:

A.

Reset the appliance with a hard reboot.

B.

Reestablish the connection to the timeserver.

C.

Configure the appliance to receive the time from an NTP server.

D.

Configure the appliance to sync with its own internal clock.

Buy Now
Questions 85

An engineer has been tasked with performing an audit of network projects to determine which objects are duplicated across the various firewall models (Cisco Secure Firewall Threat Defense Cisco Secure firewall ASA, and Meraki MX Series) deployed throughout the company Which tool will assist the engineer in performing that audit?

Options:

A.

Cisco Firepower Device Manager

B.

Cisco SecureX

C.

Cisco Defense Orchestrator

D.

Cisco Secure Firewall Management Center

Buy Now
Questions 86

A software development company hosts the website http:dev.company.com for contractors to share code for projects they are working on with internal developers. The web server is on premises and is protected by a Cisco Secure Firewall Threat Defense appliance. The network administrator is worried about someone trying to transmit infected files to internal users via this site. Which type of policy must be able associated with an access control policy to enable Cisco Secure Firewall Malware Defense to detect and block malware?

Options:

A.

SSL policy

B.

Prefilter policy

C.

File policy

D.

Network discovery policy

Buy Now
Questions 87

A connectivity issue is occurring between a client and a server which are communicating through a Cisco Firepower device While troubleshooting, a network administrator sees that traffic is reaching the server, but the client is not getting a response Which step must be taken to resolve this issue without initiating traffic from the client?

Options:

A.

Use packet-tracer to ensure that traffic is not being blocked by an access list.

B.

Use packet capture to ensure that traffic is not being blocked by an access list.

C.

Use packet capture to validate that the packet passes through the firewall and is NATed to the corrected IP address.

D.

Use packet-tracer to validate that the packet passes through the firewall and is NATed to the corrected IP address.

Buy Now
Questions 88

What is a result of enabling Cisco FTD clustering?

Options:

A.

For the dynamic routing feature, if the master unit fails, the newly elected master unit maintains all existing connections.

B.

Integrated Routing and Bridging is supported on the master unit.

C.

Site-to-site VPN functionality is limited to the master unit, and all VPN connections are dropped if the master unit fails.

D.

All Firepower appliances can support Cisco FTD clustering.

Buy Now
Questions 89

A network engineer wants to disable the HTTP response page and interactive blocking of the entire access control policy in Cisco Secure Firewall Management Center. What must be

selected in Block Response Page and Interactive Block Response Page?

Options:

A.

Custom

B.

View

C.

System

D.

None

Buy Now
Questions 90

An engineer is implementing clustering in Cisco Secure Firewall Management Center. The configuration must ensure that the cluster has a designated control node with more resources than the other nodes. What must the engineer set for the priority value of that node?

Options:

A.

0

B.

A value lower than the values assigned to the other nodes in the cluster

C.

A value higher than the values assigned to the other nodes in the cluster

D.

255

Buy Now
Questions 91

Which two statements about bridge-group interfaces in Cisco FTD are true? (Choose two.)

Options:

A.

The BVI IP address must be in a separate subnet from the connected network.

B.

Bridge groups are supported in both transparent and routed firewall modes.

C.

Bridge groups are supported only in transparent firewall mode.

D.

Bidirectional Forwarding Detection echo packets are allowed through the FTD when using bridge-group members.

E.

Each directly connected network must be on the same subnet.

Buy Now
Questions 92

Which CLI command is used to control special handling of clientHello messages?

Options:

A.

system support ssl-client-hello-tuning

B.

system support ssl-client-hello-display

C.

system support ssl-client-hello-force-reset

D.

system support ssl-client-hello-reset

Buy Now
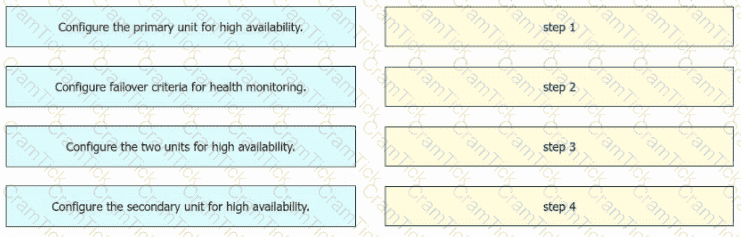
Questions 93

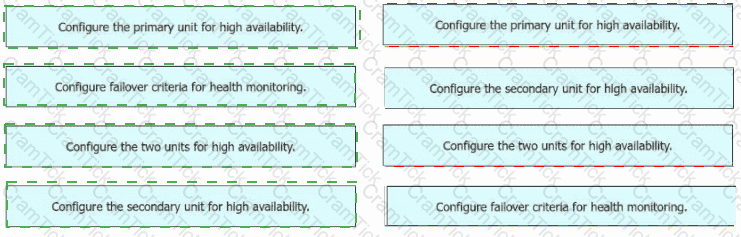
An engineer must configure high availability on two Cisco Secure Firewall Threat Defense appliances. Drag and drop the configuration steps from the left into the sequence on the right.
Options:

Buy Now
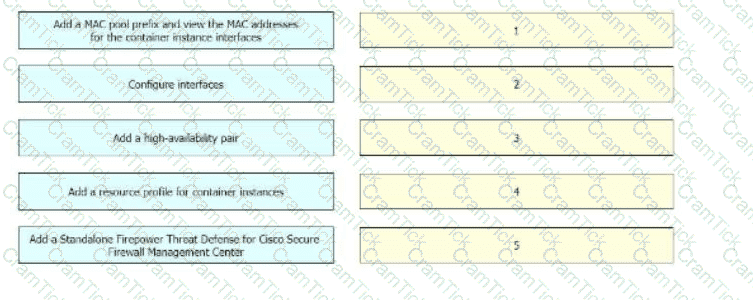
Questions 94

A network engineer is deploying a Cisco Firepower 4100 appliance and must configure a multi-instance environment for high availability. Drag and drop me actions from the left into sequence on the right far this configuration.
Options:

Buy Now
Questions 95

An engineer is configuring a Cisco Secure Firewall Threat Defense device to operate in transparent mode between two switch stacks. VLAN 10 is used for in-band management on both switch stacks. Which two actions are required on the device to inspect traffic between the switch stacks without interrupting network traffic? (Choose two.)

Options:

A.

Configure a BVI interface for VLAN 10.

B.

Configure at least one bridge group.

C.

Exempt BPDUs from advanced inspection.

D.

Set the MTU to 9198 on all interfaces to support jumbo frames.

E.

Add separate routes for data and management traffic.

Buy Now
Questions 96

Which firewall design allows a firewall to forward traffic at layer 2 and layer 3 for the same subnet?

Options:

A.

Cisco Firepower Threat Defense mode

B.

transparent mode

C.

routed mode

D.

integrated routing and bridging

Buy Now
Questions 97

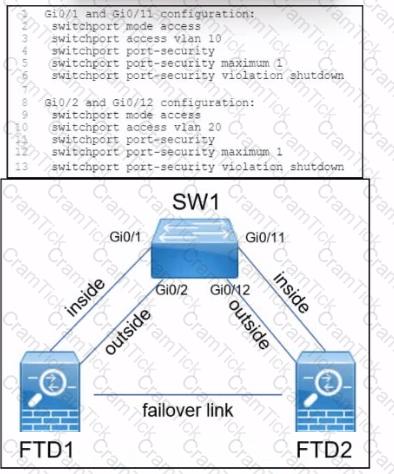
Refer to the exhibit.

A company is deploying a pair of Cisco Secure Firewall Threat defence devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link. What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?

Options:

A.

Disable port security on the switch interfaces connected to FTD1 and FTD2.

B.

Set maximum secured addresses to two on the switch interfaces on FTD1 and FTD2.

C.

Connect and configure a stateful link and thon deploy the changes.

D.

Configure the spanning-tree PortFasI feature on SW1 and FTD2

Buy Now
Questions 98

A network administrator is reviewing a weekly scheduled attacks risk report and notices a host that is flagged for an impact 2 attack. Where should the administrator look within Cisco FMC to find out more relevant information about this host and attack?

Options:

A.

Analysis > Lookup > Whols

B.

Analysis > Correlation > Correlation Events

C.

Analysis > Hosts > Vulnerabilities

D.

Analysis > Hosts > Host Attributes

Buy Now
Questions 99

What is a functionality of port objects in Cisco FMC?

Options:

A.

to mix transport protocols when setting both source and destination port conditions in a rule

B.

to represent protocols other than TCP, UDP, and ICMP

C.

to represent all protocols in the same way

D.

to add any protocol other than TCP or UDP for source port conditions in access control rules.

Buy Now
Questions 100

A network administrator discovers that a user connected to a file server and downloaded a malware file. The Cisc FMC generated an alert for the malware event, however the user still remained connected. Which Cisco APM file rule action within the Cisco FMC must be set to resolve this issue?

Options:

A.

Detect Files

B.

Malware Cloud Lookup

C.

Local Malware Analysis

D.

Reset Connection

Buy Now
Questions 101

An engineer is configuring a new dashboard within Cisco Secure Firewall Management Center and is having trouble implementing a custom widget. When a custom analysis widget is configured which option is mandatory for the system to display the information?

Options:

A.

table

B.

filter

C.

title

D.

results

Buy Now
Questions 102

What is the role of the casebook feature in Cisco Threat Response?

Options:

A.

sharing threat analysts

B.

pulling data via the browser extension

C.

triage automaton with alerting

D.

alert prioritization

Buy Now
Questions 103

An administrator is adding a new URL-based category feed to the Cisco FMC for use within the policies. The intelligence source does not use STIX. but instead uses a .txt file format. Which action ensures that regular updates are provided?

Options:

A.

Add a URL source and select the flat file type within Cisco FMC.

B.

Upload the .txt file and configure automatic updates using the embedded URL.

C.

Add a TAXII feed source and input the URL for the feed.

D.

Convert the .txt file to STIX and upload it to the Cisco FMC.

Buy Now
Questions 104

An engineer must implement Cisco Secure Firewall transparent mode due to a new server recently being added that must communicate with an existing server that is currently separated by the firewall. Which implementation action must be taken next by the engineer to accomplish the goal?

Options:

A.

Enable both servers to share the same VXLAN segment.

B.

Configure the same default gateway for both servers.

C.

Ensure that both servers are in the same bridge domain.

D.

Assign the same subnet to both servers.

Buy Now
Questions 105

Which feature issupportedby IRB on Cisco FTD devices?

Options:

A.

redundant interface

B.

dynamic routing protocol

C.

EtherChannel interface

D.

high-availability cluster

Buy Now
Questions 106

A network administrator is configuring an access control policy on a Secure Firewall Threat Defense device. The administrator wants to exclude traffic to a certain banking site from being decrypted. What must the rule include to specify the banking site?

Options:

A.

action of trust, specified protocol for SSL, and below the SSL decryption rule

B.

action of deny and for the HTTP and HTTPS access protocols

C.

action of block, specified protocol for SSL, and above the SSL decryption rule

D.

action of trust and above the SSL decryption rule

Buy Now
Questions 107

What is an attribute of the risk reporting capability in Cisco Secure Firewall Management Center?
Options:

A.

Includes all domains in a multidomain system

B.

Uses the same templates available to standard reports

C.

Includes the current domain in a multidomain system

D.

Uses the XML format to export all reporting

Buy Now
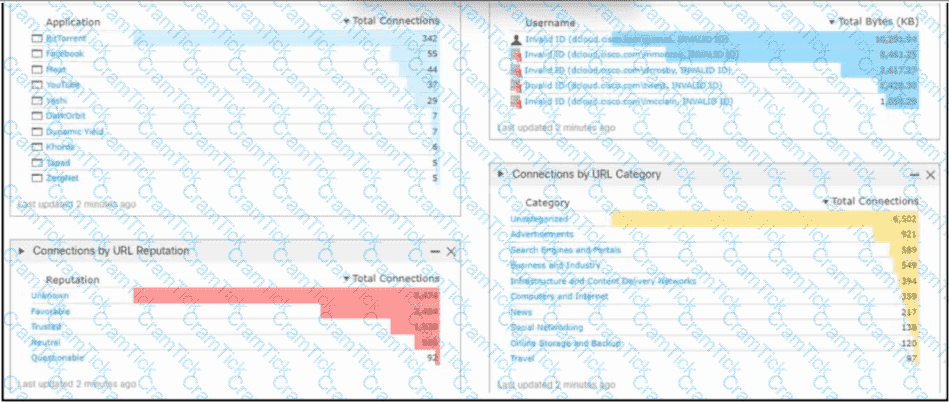
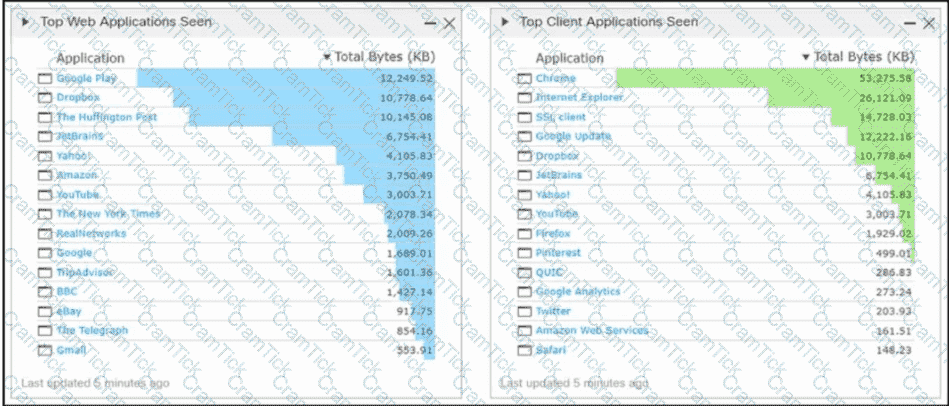
Questions 108

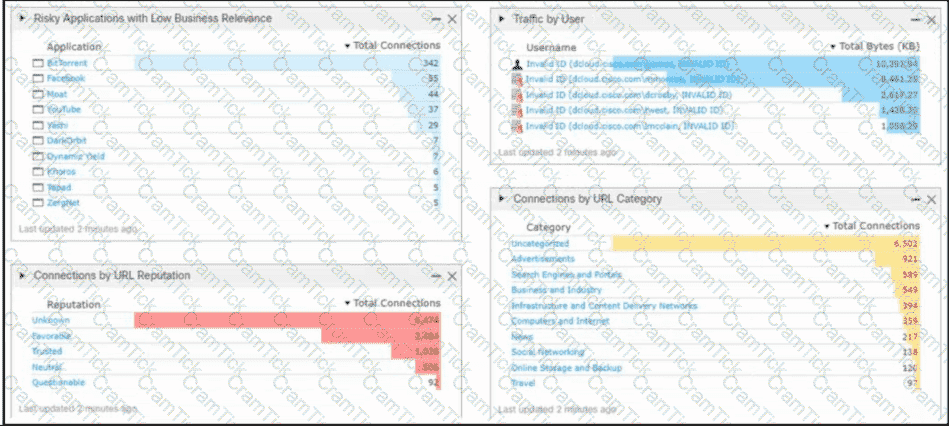
Refer to the exhibit. An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must be taken by the user to decrease the risk of data loss?

Options:

A.

Stop all URLs that have an unknown reputation.

B.

Block the use of Dropbox.

C.

Stop all the URLs that are uncategorized.

D.

Block all the BitTorrent applications.

Buy Now
Questions 109

An engineer is investigating connectivity problems on Cisco Firepower for a specific SGT. Which command allows the engineer to capture real packets that pass through the firewall using an SGT of 64?

Options:

A.

capture CAP type inline-tag 64 match ip any any

B.

capture CAP match 64 type inline-tag ip any any

C.

capture CAP headers-only type inline-tag 64 match ip any any

D.

capture CAP buffer 64 match ip any any

Buy Now
Questions 110

What is the RTC workflow when the infected endpoint is identified?

Options:

A.

Cisco ISE instructs Cisco AMP to contain the infected endpoint.

B.

Cisco ISE instructs Cisco FMC to contain the infected endpoint.

C.

Cisco AMP instructs Cisco FMC to contain the infected endpoint.

D.

Cisco FMC instructs Cisco ISE to contain the infected endpoint.

Buy Now
Questions 111

An engineer is configuring a cisco FTD appliance in IPS-only mode and needs to utilize fail-to-wire interfaces. Which interface mode should be used to meet these requirements?

Options:

A.

transparent

B.

routed

C.

passive

D.

inline set

Buy Now
Questions 112

Which Cisco Rapid Threat Containment mitigation action is enabled by integrating pxGrid Adaptive Network Control with Cisco ISE and Cisco Secure Firewall Management Center?
Options:

A.

Block

B.

Terminate

C.

Suspend

D.

Reject

Buy Now
Questions 113

An engineer must perform a packet capture on a Cisco Secure Firewall Threat Defense device to confirm the MAC address of the host using IP address 192.168.100.100 while troubleshooting an ARP issue. What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?

Options:

A.

-w capture.pcap -s 1518 host 192.168.100.100 mac

B.

-nm src 192.168.100.100

C.

-w capture.pcap -s 1518 host 192.168.100.100 ether

D.

-ne src 192.168.100.100

Buy Now
Questions 114

An engineer is configuring a Cisco Secure Firewall Management Center appliance. The company requires the use of a TAXII server in Threat Intelligence Director and requires the Action to be set to Block. On which two object types can the engineer configure the Block action? (Choose two.)

Options:

A.

Observable

B.

Element

C.

Indicator

D.

Complex indicator

E.

Source

Buy Now
Questions 115

A security engineer manages a firewall console and an endpoint console and finds it challenging and the consuming to review events and modify blocking of specific files in both consoles. Which action must the engineer take to streamline this process?

Options:

A.

From the Secure FMC. create a Cisco Secure Endpoint object and reference the object in the Cisco Secure Endpoint console.

B.

From the Cisco Secure Endpoint console, Croats and copy an API key and paste into the Cisco Secure AMP tab

C.

initiate the integration between Secure FMC and Cisco Secure Endpoint from the Secure FMC using the AMP tab

D.

Within the Cisco Secure Endpoint console, copy the connector GUID and paste into the Cisco Secure Firewall Management Center (FMC) AMP tab.

Buy Now
Questions 116

A mid-sized company is experiencing higher network bandwidth utilization due to a recent acquisition The network operations team is asked to scale up their one Cisco FTD appliance deployment to higher capacities due to the increased network bandwidth. Which design option should be used to accomplish this goal?

Options:

A.

Deploy multiple Cisco FTD appliances in firewall clustering mode to increase performance.

B.

Deploy multiple Cisco FTD appliances using VPN load-balancing to scale performance.

C.

Deploy multiple Cisco FTD HA pairs to increase performance

D.

Deploy multiple Cisco FTD HA pairs in clustering mode to increase performance

Buy Now
Questions 117

An organization has implemented Cisco Firepower without IPS capabilities and now wants to enable inspection for their traffic. They need to be able to detect protocol anomalies and utilize the Snort rule sets to detect malicious behaviour. How is this accomplished?

Options:

A.

Modify the access control policy to redirect interesting traffic to the engine

B.

Modify the network discovery policy to detect new hosts to inspect

C.

Modify the network analysis policy to process the packets for inspection

D.

Modify the intrusion policy to determine the minimum severity of an event to inspect.

Buy Now
Questions 118

What is needed to start a threat investigation in Cisco XDR?

Options:

A.

indicator of compromise

B.

local IP address

C.

user name

D.

indicator of attack

Buy Now
Questions 119

An engineer must deploy a Cisco FTD appliance via Cisco FMC to span a network segment to detect malware and threats. When setting the Cisco FTD interface mode, which sequence of actions meets this requirement?

Options:

A.

Set to passive, and configure an access control policy with an intrusion policy and a file policy defined

B.

Set to passive, and configure an access control policy with a prefilter policy defined

C.

Set to none, and configure an access control policy with a prefilter policy defined

D.

Set to none, and configure an access control policy with an intrusion policy and a file policy defined

Buy Now
Questions 120

Which component is needed to perform rapid threat containment with Cisco FMC?

Options:

A.

ISE

B.

RESTful API

C.

SIEM

D.

DDI

Buy Now
Questions 121

An engineer must deploy URL filtering in Cisco Secure Firewall Management Center Version 7.0. The engineer is configuring a URL condition for an access control rule to filter websites that display bad behavior or are malicious or undesirable. Which reputation level must be configured?

Options:

A.

Questionable

B.

Untrusted

C.

Favorable

D.

Neutral

Buy Now
Questions 122

An engineer is monitoring network traffic from their sales and product development departments, which are on two separate networks What must be configured in order to maintain data privacy for both departments?
Options:

A.

Use a dedicated IPS inline set for each department to maintain traffic separation

B.

Use 802 1Q mime set Trunk interfaces with VLANs to maintain logical traffic separation

C.

Use passive IDS ports for both departments

D.

Use one pair of inline set in TAP mode for both departments

Buy Now
Questions 123

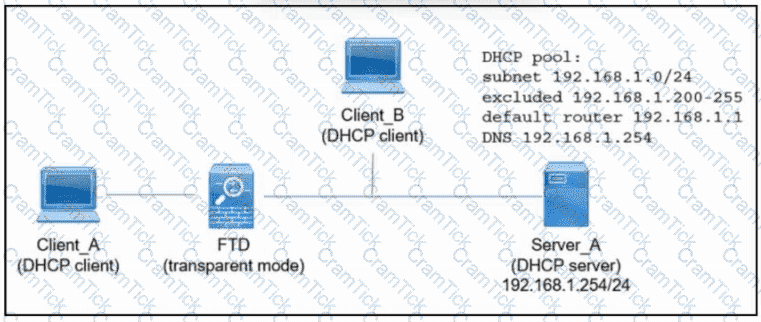
Refer to the exhibit. An engineer is deploying a new instance of Cisco Secure Firewall Threat Defense. Which action must the engineer take next so that Client_A and Client_B receive an IP address via DHCP from Server_A?

Options:

A.

Disable Option 82 in the DHCP relay configuration properties using Secure Firewall Management Center.

B.

Add access rules that allow DHCP traffic by using Cisco Secure Firewall Management Center.

C.

Add another DHCP pool on Server_A with DHCP relay on Secure Firewall Threat Defense.

D.

Disable all the DHCP Snort rules by using Secure Firewall Device Manager.

Buy Now
Questions 124

A consultant Is working on a project where the customer is upgrading from a single Cisco Firepower 2130 managed by FDM to a pair of Cisco Firepower 2130s managed oy FMC tor nigh availability. The customer wants the configures of the existing device being managed by FDM to be carried over to FMC and then replicated to the additional: device being added to create the high availability pair. Which action must the consultant take to meet this requirement?

Options:

A.

The current FDM configuration must be configured by hand into FMC before the devices are registered.

B.

The current FDM configuration will be converted automatically into FMC when the device registers.

C.

The current FDM configuration must be migrated to FMC using the Secure Firewall Migration Tool.

D.

The FTD configuration must be converted to ASA command format, which can then be migrated to FMC.

Buy Now
Questions 125

A network administrator must send a daily email report to management detailing changes made during the previous 24 hours in Cisco Secure Firewall Management Center. Which system setting must be enabled to meet this requirement?

Options:

A.

Change Reconciliation

B.

Send Audit Log to HTTP Server

C.

Send Audit Log to Syslog

D.

STIG Compliance

Buy Now
Questions 126

Encrypted Visibility Engine (EVE) is enabled under which lab on an access control policy in Cisco Secure Firewall Management Centre?

Options:

A.

Network Analysis Policy

B.

Advanced

C.

Security Intelligence

D.

SSL

Buy Now
Questions 127

An engineer is building a new access control policy using Cisco FMC. The policy must inspect a unique IPS policy as well as log rule matching. Which action must be taken to meet these requirements?

Options:

A.

Configure an IPS policy and enable per-rule logging.

B.

Disable the default IPS policy and enable global logging.

C.

Configure an IPS policy and enable global logging.

D.

Disable the default IPS policy and enable per-rule logging.

Buy Now
Questions 128

A network administrator is trying to convert from LDAP to LDAPS for VPN user authentication on a Cisco FTD. Which action must be taken on the Cisco FTD objects to accomplish this task?

Options:

A.

Add a Key Chain object to acquire the LDAPS certificate.

B.

Create a Certificate Enrollment object to get the LDAPS certificate needed.

C.

Identify the LDAPS cipher suite and use a Cipher Suite List object to define the Cisco FTD connection requirements.

D.

Modify the Policy List object to define the session requirements for LDAPS.

Buy Now
Questions 129

An engineer must configure a SPAN to monitor traffic by using a Cisco Secure IPS device in passive mode. The Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst Switch interface Gi0/3. Which SPAN configuration meets the requirement?

A)
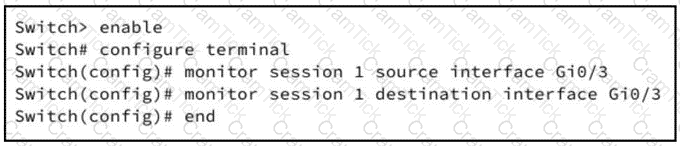
B)
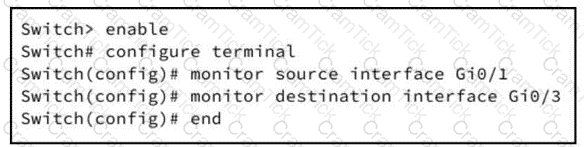
C)
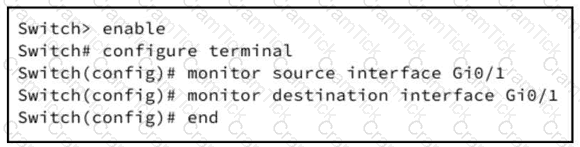
D)
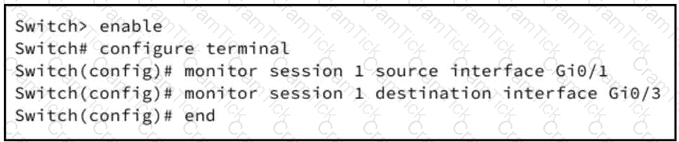
Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Questions 130

An engineer must implement static route tracking on a Cisco Secure Firewall Threat Defense appliance. Static route and IP SLA operation has already been configured. Static route must be removed from the routing table if the tracked object is unreachable. Which action must the engineer take next to meet the requirement?

Options:

A.

Implement a secondary route that has a higher precedence.

B.

Enable the IP SLA Responder on the backup path interface.

C.

Assign a tracking object to the static route and the IP SLA operation.

D.

Enable an ICMP redirect message on the interface connected to the backup path.

Buy Now
Questions 131

Which command is entered in the Cisco FMC CLI to generate a troubleshooting file?

Options:

A.

show running-config

B.

show tech-support chassis

C.

system support diagnostic-cli

D.

sudo sf_troubleshoot.pl

Buy Now
Questions 132

A network administrator manages a network with multiple firewalls in a datacenter using Cisco Secure Firepower Management Center. The administrator must change a next-generation firewall from routed to transparent mode. Which action must the administrator take next to meet the requirement?

Options:

A.

Deregister the firewall in Cisco Secure Firewall Management Center.

B.

Enter the configure transparent firewall command from the CLI.

C.

Create one or more bridge groups from the CLI.

D.

Manually delete the interface configuration from the CLI.

Buy Now
Questions 133

An engineer is configuring a multidomain instance of Cisco Secure Firewall Management Center. The instance must be integrated with Cisco Secure Endpoint. What must the engineer configure to allow multiple domains to have hosts with the same IP-MAC address pairs?

Options:

A.

second-level domain

B.

leaf domain

C.

global domain

D.

subdomain

Buy Now
Exam Code: 300-710
Exam Name: Securing Networks with Cisco Firepower (300-710 SNCF) v1.2
Last Update: Oct 14, 2026
Questions: 444
300-710 pdf

300-710 PDF

$28.5  $94.99
300-710 Engine

300-710 Testing Engine

$33  $109.99
300-710 PDF + Engine

300-710 PDF + Testing Engine

$43.5  $144.99