A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?
Which configuration method provides the options to prevent physical and virtual endpoint devices that are in the same base EPG or uSeg from being able to communicate with each other with Vmware VDS or Microsoft vSwitch?
Which solution stops unauthorized access to the system if a user ' s password is compromised?
What is the recommendation in a zero-trust model before granting access to corporate applications and resources?
A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
A security administrator must implement a network intrusion policy in Cisco Secure Firewall to block new potential threats without sacrificing network performance. The administrator plans to create a base policy with a broad rule set optimized to protect the environment without significantly affecting throughput. Which type of policy should the administrator create?
What is the purpose of the Decrypt for Application Detection feature within the WSA Decryption options?
Which command is used to log all events to a destination colector 209.165.201.107?
Which method must be used to connect Cisco Secure Workload to external orchestrators at a client site when the client does not allow incoming connections?
Which feature requires a network discovery policy on the Cisco Firepower Next Generation Intrusion Prevention
System?
Which two Cisco Umbrella security categories are used to prevent command-and-control callbacks on port 53 and protect users from being tricked into providing confidential information? (Choose two.)
A customer has various external HTTP resources available including Intranet. Extranet, and Internet, with a proxy configuration running in explicit mode Which method allows the client desktop browsers to be configured to select when to connect direct or when to use the proxy?
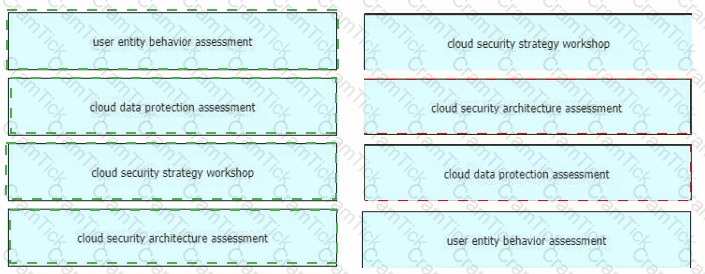
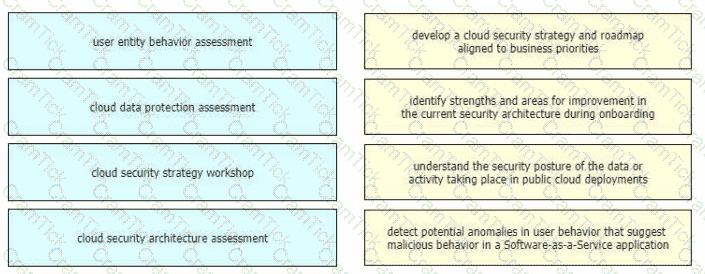
Drag and drop the cloud security assessment components from the left onto the definitions on the right.
Which action configures the IEEE 802.1X Flexible Authentication feature lo support Layer 3 authentication mechanisms?
An organization wants to reduce their attach surface for cloud applications. They want to understand application communications, detect abnormal application Behavior, and detect vulnerabilities within the applications. Which action accomplishes this task?
Which RADIUS attribute can you use to filter MAB requests in an 802.1 x deployment?
When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?
Which Cisco cloud security software centrally manages policies on multiple platforms such as Cisco ASA, Cisco Firepower, Cisco Meraki, and AWS?
An engineer needs to configure a Cisco Secure Email Gateway (SEG) to prompt users to enter multiple forms of identification before gaining access to the SEG. The SEG must also join a cluster using the preshared key of cisc421555367. What steps must be taken to support this?
A company identified a phishing vulnerability during a pentest. What are two ways the company can protect employees from the attack? (Choose two.)
A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)
A network engineer must enable SSH and SCP on a Cisco IOS router. The engineer has already generated the encryption keys and enabled SCP services on the router. Which configuration action must be performed next?
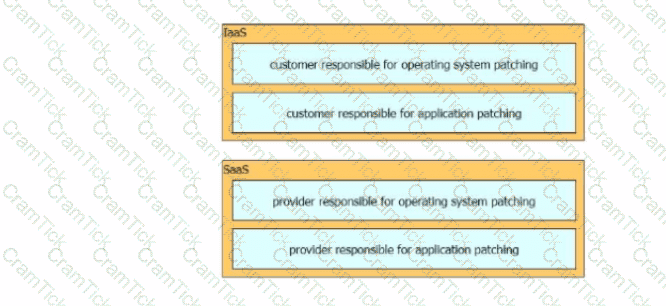
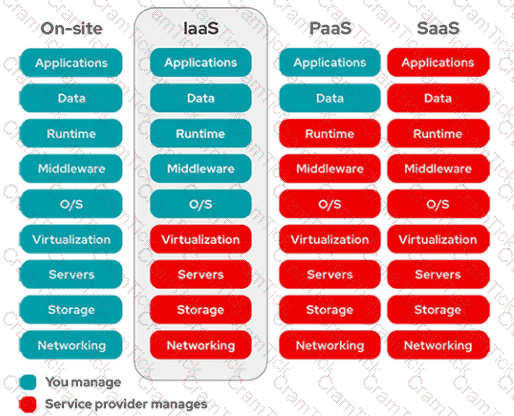
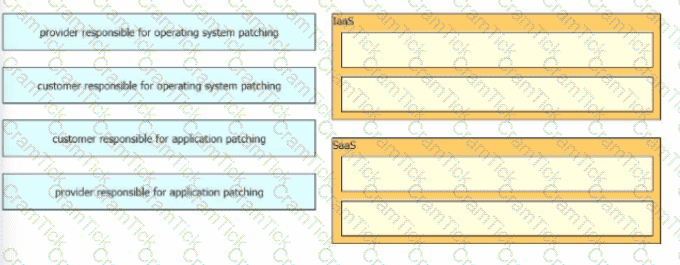
Drag and drop the security responsibilities from the left onto the corresponding cloud service models on the right.
Refer to the exhibit.
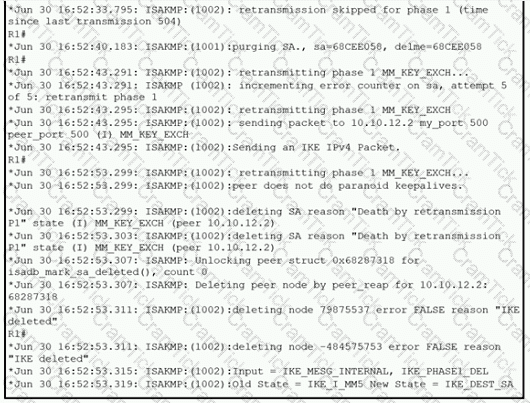
A network administrator configured a site-to-site VPN tunnel between two Cisco IOS routers, and hosts are unable to communicate between two sites of VPN. The network administrator runs the debug crypto isakmp sa command to track VPN status. What is the problem according to this command output?
A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?
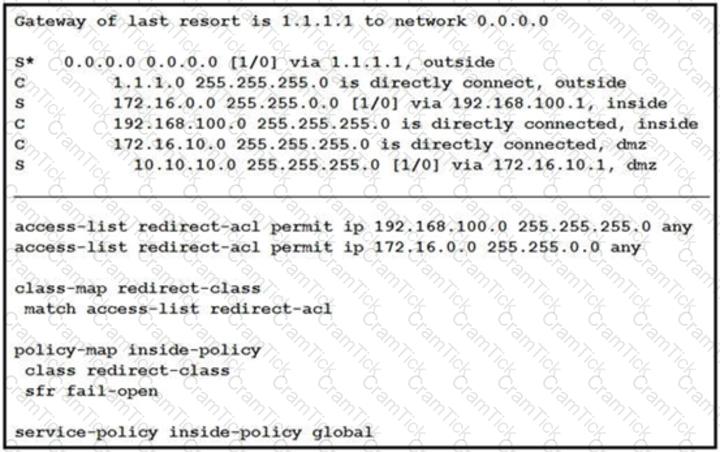
An organization must add new firewalls to its infrastructure and wants to use Cisco ASA or Cisco FTD.
The chosen firewalls must provide methods of blocking traffic that include offering the user the option to bypass the block for certain sites after displaying a warning page and to reset the connection. Which solution should the organization choose?
Which type of API is being used when a controller within a software-defined network architecture dynamically
makes configuration changes on switches within the network?
Which Splunk SOAR component automates multi-step security actions into a repeatable workflow?
Refer to the exhibit. When creating an access rule for URL filtering, a network engineer adds certain categories and individual URLs to block. What is the result of the configuration?
Which attack type attempts to shut down a machine or network so that users are not able to access it?
How does Cisco Umbrella protect clients when they operate outside of the corporate network?
Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?
A network engineer is deciding whether to use stateful or stateless failover when configuring two ASAs for high availability. What is the connection status in both cases?
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data
within a network perimeter?
II
An engineer musí set up 200 new laptops on a network and wants to prevent the users from moving their laptops around to simplify administration Which switch port MAC address security setting must be used?
Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?
An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users. Which action accomplishes this goal?
Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention
System?
Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco Secure Email Gateway?
What is the role of Cisco Umbrella Roaming when it is installed on an endpoint?
Which component of Cisco umbrella architecture increases reliability of the service?
An engineer must implement a file transfer solution between a company ' s data center and branches. The company has numerous servers hosted in a hybrid cloud implementation. The file transfer protocol must support authentication, protect the data against unauthorized access, and ensure that users cannot list directories or remove files remotely. Which protocol must be used?
An engineer has been tasked with configuring a Cisco FTD to analyze protocol fields and detect anomalies in the traffic from industrial systems. What must be done to meet these requirements?
Which IPS analysis technique matches traffic against a database of known attack patterns?
Which two deployment modes does the Cisco ASA FirePower module support? (Choose two)
A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?
Which two probes are configured to gather attributes of connected endpoints using Cisco Identity Services
Engine? (Choose two)
In which two ways does Easy Connect help control network access when used with Cisco TrustSec? (Choose two)
Refer to the exhibit.
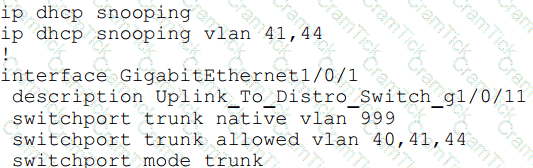
An organization is using DHCP Snooping within their network. A user on VLAN 41 on a new switch is
complaining that an IP address is not being obtained. Which command should be configured on the switch
interface in order to provide the user with network connectivity?
Which solution for remote workers enables protection, detection, and response on the endpoint against known and unknown threats?
A financial services firm is concerned about employees inadvertently pasting sensitive customer account information into public generative AI websites. The security team needs to implement a solution that inspects outbound traffic and prevents the transmission of sensitive data to AI platforms. Which two configuration actions must the administrator perform on Cisco Secure Access to achieve the requirement? (Choose two.)
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
What are the components of endpoint protection against social engineering attacks?
Which capability is exclusive to a Cisco AMP public cloud instance as compared to a private cloud instance?
An engineer must modify a policy to block specific addresses using Cisco Umbrella. The policy is created already and is actively u: of the default policy elements. What else must be done to accomplish this task?
Which two types of policies are used by ZTNA to provide access to an application? (Choose two.)
A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256
cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?
The security architect has concluded that the optimal mail flow positions the existing Cisco Secure Email Gateways as the first termination point for inbound messages, while Cisco Secure Email Threat Defense is positioned between the Secure Email Gateways and the cloud mail platform. The security engineer has been asked to configure the incoming-traffic domain setting in Cisco Secure Email Threat Defense so that it reflects the Secure Email Gateway handling inbound messages ahead of the service. Which domain configuration for incoming traffic must be selected to meet the requirement?
What is the function of the crypto is a kmp key cisc406397954 address 0.0.0.0 0.0.0.0 command when establishing an IPsec VPN tunnel?
An organization is trying to improve their Defense in Depth by blocking malicious destinations prior to a
connection being established. The solution must be able to block certain applications from being used within the network. Which product should be used to accomplish this goal?
Which two tasks allow NetFlow on a Cisco ASA 5500 Series firewall? (Choose two)
A large retail enterprise is deploying Cisco Secure Private Access to enable remote employees to reach internal applications without manual intervention. The IT department requires a seamless, zero-touch enrollment process in which users are registered and authenticated transparently without requiring end-user action. The architecture must support robust high availability for back-end connectivity to ensure continuous access to private resources. Which configuration approach must the administrator implement to meet the requirement?
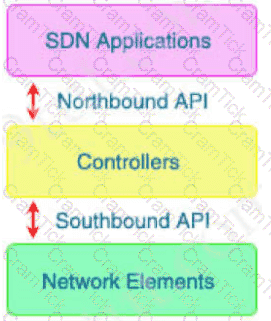
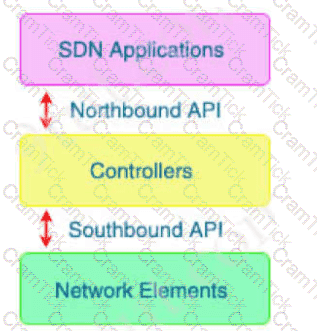
What are two functionalities of northbound and southbound APIs within Cisco SDN architecture? (Choose two.)
An organization has two systems in their DMZ that have an unencrypted link between them for communication.
The organization does not have a defined password policy and uses several default accounts on the systems.
The application used on those systems also have not gone through stringent code reviews. Which vulnerability
would help an attacker brute force their way into the systems?
What is a functional difference between a Cisco ASA and a Cisco IOS router with Zone-based policy firewall?
An engineer is configuring a Cisco ESA and wants to control whether to accept or reject email messages to a
recipient address. Which list contains the allowed recipient addresses?
Based on the NIST 800-145 guide, which cloud architecture is provisioned for exclusive use by a specific group of consumers from different organizations and may be owned, managed, and operated by one or more of those organizations?
Which security solution is used for posture assessment of the endpoints in a BYOD solution?
Using Cisco Cognitive Threat Analytics, which platform automatically blocks risky sites, and test unknown sites for hidden advanced threats before allowing users to click them?
Which two deployment model configurations are supported for Cisco FTDv in AWS? (Choose two)
An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users,
data, and applications. There is a requirement to use the Cisco cloud native CASB and cloud cybersecurity
platform. What should be used to meet these requirements?
Which cloud model is a collaborative effort where infrastructure is shared and jointly accessed by several organizations from a specific group?
Which algorithm provides encryption and authentication for data plane communication?
A network engineer is trying to figure out whether FlexVPN or DMVPN would fit better in their environment.
They have a requirement for more stringent security multiple security associations for the connections, more efficient VPN establishment as well consuming less bandwidth. Which solution would be best for this and why?
An engineer is configuring IPsec VPN and needs an authentication protocol that is reliable and supports ACK
and sequence. Which protocol accomplishes this goal?
A security test performed on one of the applications shows that user input is not validated. Which security vulnerability is the application more susceptible to because of this lack of validation?
Which two services are provided by the Cisco Talos Incident Response group? (Choose two.)
Which two methods must be used to add switches into the fabric so that administrators can control how switches are added into DCNM for private cloud management? (Choose two.)
Which action configures the IEEE 802.1X Flexible Authentication feature to support Layer 3 authentication mechanisms?
An engineer is configuring Cisco Secure Endpoint to enhance network security by specifying a large set of external IP addresses that must be monitored for potential threats. The engineer is configuring an IP List and must add the IP addresses to the list. Which configuration action must the engineer take next to meet the requirement?
Which component of a Cisco IOS NetFlow solution enables the aggregation of data packets into flows?
An administrator is implementing management plane protection and must configure an interface on a Cisco router to only terminate management packets that are destined for the router. Which set of IOS commands must be used to complete the implementation?
For which type of attack is multifactor authentication an effective deterrent?
Which Cisco security solution secures public, private, hybrid, and community clouds?
An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?
Which interface mode does a Cisco Secure IPS device use to block suspicious traffic?
Which Linux system call loads an eBPF program and manages eBPF maps within the kernel?
Which direction do attackers encode data in DNS requests during exfiltration using DNS tunneling?
Which cloud service offering allows customers to access a web application that is being hosted, managed, and maintained by a cloud service provider?
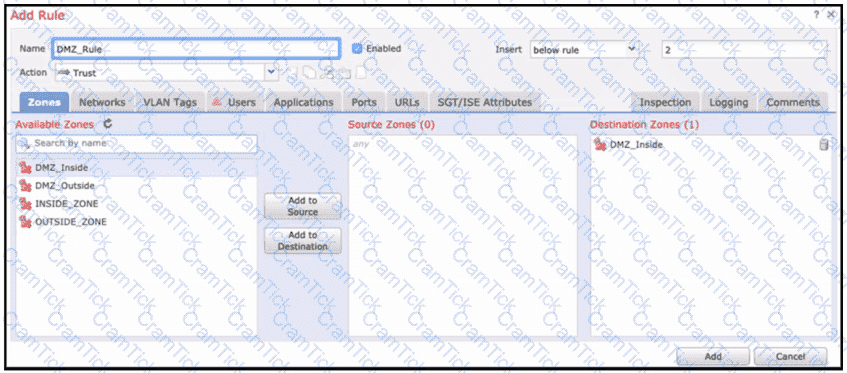
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?
Which two features of Cisco DNA Center are used in a Software Defined Network solution? (Choose two)
An engineer is implementing NTP authentication within their network and has configured both the client and server devices with the command ntp authentication-key 1 md5 Cisc392368270. The server at 1.1.1.1 is attempting to authenticate to the client at 1.1.1.2, however it is unable to do so. Which command is required to enable the client to accept the server’s authentication key?
An engineer is configuring Cisco WSA and needs to deploy it in transparent mode. Which configuration component must be used to accomplish this goal?
A Cisco ISE engineer configures Central Web Authentication (CWA) for wireless guest access and must have the guest endpoints redirect to the guest portal for authentication and authorization. While testing the policy, the engineer notices that the device is not redirected and instead gets full guest access. What must be done for the redirect to work?
In which two ways does a system administrator send web traffic transparently to the Web Security Appliance?
(Choose two)
How does Cisco Workload Optimization portion of the network do EPP solutions solely performance issues?
Which two capabilities of Cisco Secure Workload facilitate the detection of lateral movement within data-center and cloud environments? (Choose two.)
Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)
A Cisco Secure Email Gateway network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Secure Email Gateway is not dropping files that have an undetermined verdict. What is causing this issue?
Which two prevention techniques are used to mitigate SQL injection attacks? (Choose two)
An organization has two machines hosting web applications. Machine 1 is vulnerable to SQL injection while machine 2 is vulnerable to buffer overflows. What action would allow the attacker to gain access to machine 1 but not machine 2?
A Cisco Firepower administrator needs to configure a rule to allow a new application that has never been seen
on the network. Which two actions should be selected to allow the traffic to pass without inspection? (Choose
two)
An engineer wants to automatically assign endpoints that have a specific OUI into a new endpoint group. Which
probe must be enabled for this type of profiling to work?
A facilities team is onboarding a fleet of badge readers and IP cameras through MAB authentication on Cisco Catalyst access switches integrated with Cisco ISE. After Cisco ISE profiles each endpoint, an authorization policy must dynamically move the device into a dedicated IoT VLAN that differs from the access VLAN statically defined on the port. The endpoints lack a supplicant and cannot automatically renew their DHCP addresses. The network engineer requires Cisco ISE to issue a Change of Authorization that forces each endpoint to re-establish connectivity and request a fresh DHCP lease under the new authorization policy. Which configuration action must be performed on Cisco ISE to meet the requirement?
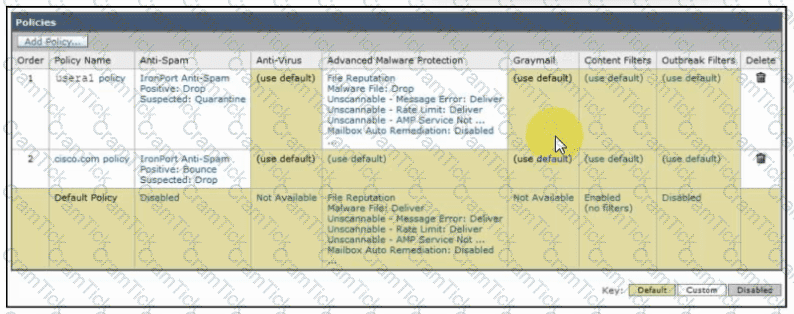
Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?
An engineer configures new features within the Cisco Umbrella dashboard and wants to identify and proxy traffic that is categorized as risky domains and may contain safe and malicious content. Which action accomplishes these objectives?
Which Cisco platform processes behavior baselines, monitors for deviations, and reviews for malicious processes in data center traffic and servers while performing software vulnerability detection?
A network engineer must configure a Cisco Secure Email Gateway to prompt users to enter two forms of information before gaining access. The Secure Email Gateway must also join a cluster machine using preshared keys. What must be configured to meet these requirements?
An administrator configures a new destination list in Cisco Umbrella so that the organization can block specific domains for its devices. What should be done to ensure that all subdomains of domain.com are blocked?
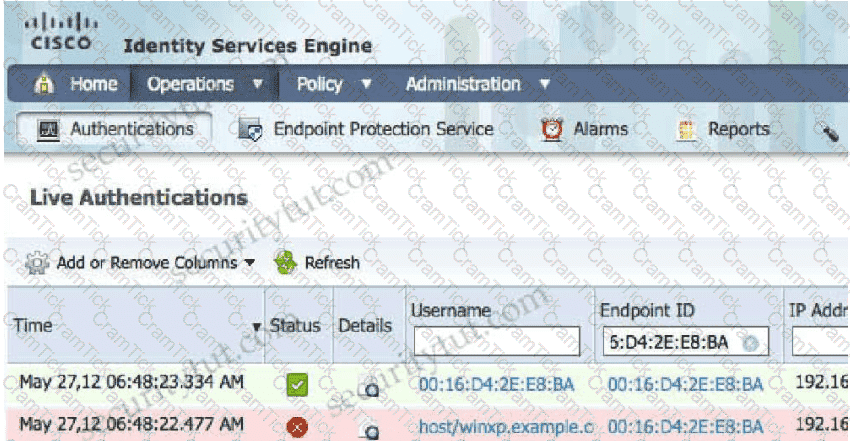
A network administrator is configuring a switch to use Cisco ISE for 802.1X. An endpoint is failing
authentication and is unable to access the network. Where should the administrator begin troubleshooting to verify the authentication details?
Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?
An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?
Which type of data exfiltration technique encodes data in outbound DNS requests to specific servers
and can be stopped by Cisco Umbrella?
Which cryptographic process provides origin confidentiality, integrity, and origin authentication for packets?
Refer to the exhibit.
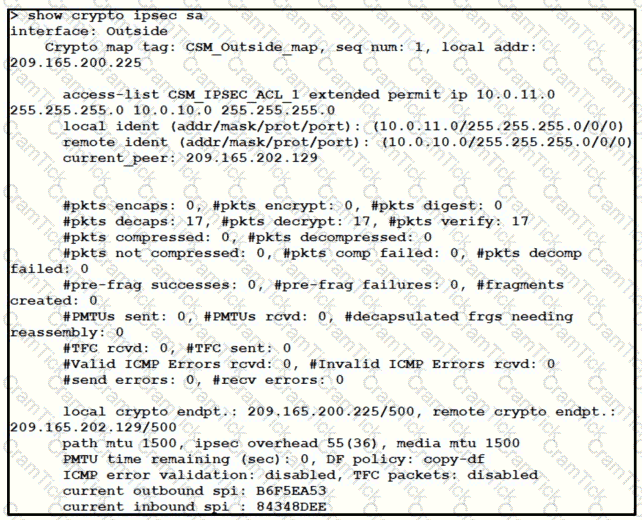
Traffic is not passing through IPsec site-to-site VPN on the Firepower Threat Defense appliance. What is causing this issue?
For a given policy in Cisco Umbrella, how should a customer block websites based on a custom list?
Which two risks is a company vulnerable to if it does not have a well-established patching solution for
endpoints? (Choose two)
Which solution allows an administrator to provision, monitor, and secure mobile devices on Windows and Mac computers from a centralized dashboard?
An organization is receiving SPAM emails from a known malicious domain. What must be configured in order to
prevent the session during the initial TCP communication?
Refer to the exhibit.
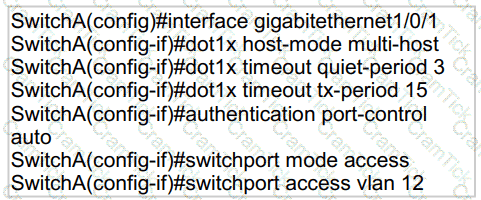
An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?
Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?
An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites but other sites are not accessible due to an error. Why is the error occurring?
For Cisco IOS PKI, which two types of Servers are used as a distribution point for CRLs? (Choose two)
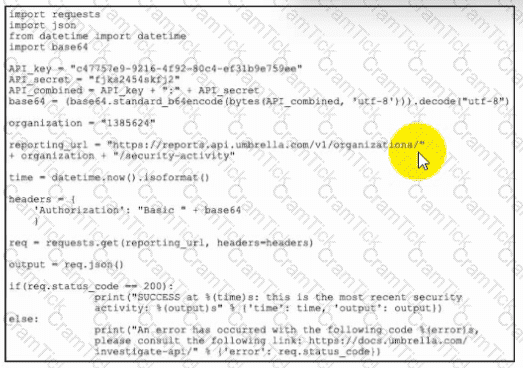
Refer to the exhibit. Which task is the Python script performing by using the Cisco Umbrella API?
An organization is implementing AAA for their users. They need to ensure that authorization is verified for every command that is being entered by the network administrator. Which protocol must be configured in order to provide this capability?
Which endpoint protection and detection feature performs correlation of telemetry, files, and intrusion
events that are flagged as possible active breaches?
A company recently discovered an attack propagating throughout their Windows network via a file named abc428565580xyz exe The malicious file was uploaded to a Simple Custom Detection list in the AMP for Endpoints Portal and the currently applied policy for the Windows clients was updated to reference the detection list Verification testing scans on known infected systems shows that AMP for Endpoints is not detecting the presence of this file as an indicator of compromise What must be performed to ensure detection of the malicious file?
Which PKI enrollment method allows the user to separate authentication and enrollment actions and also
provides an option to specify HTTP/TFTP commands to perform file retrieval from the server?
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?
When using Cisco AMP for Networks which feature copies a file to the Cisco AMP cloud for analysis?
A web hosting company must upgrade its older, unsupported on-premises servers. The company wants a cloud solution in which the cloud provider is responsible for:
Server patching
Application maintenance
Data center security
Disaster recovery
Which type of cloud meets the requirements?
Which mitigation strategy should be used to protect against session hijacking attacks in a cloud environment?
What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an
organization? (Choose two)
What Cisco command shows you the status of an 802.1X connection on interface gi0/1?
A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?
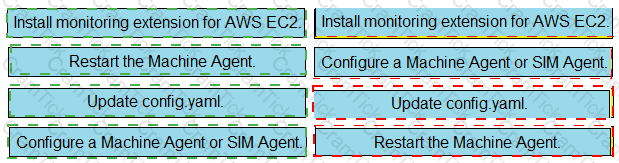
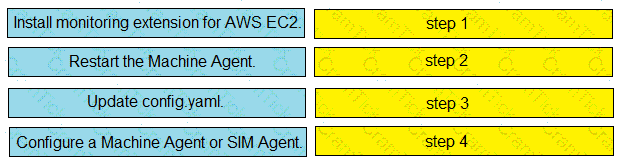
Drag and drop the steps from the left into the correct order on the right to enable AppDynamics to monitor an EC2 instance in Amazon Web Services.
What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?
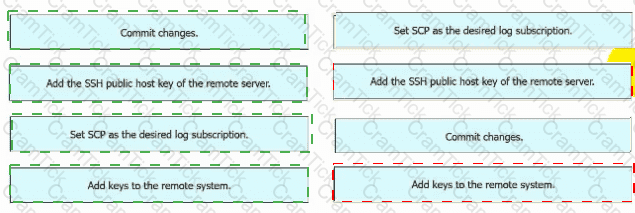
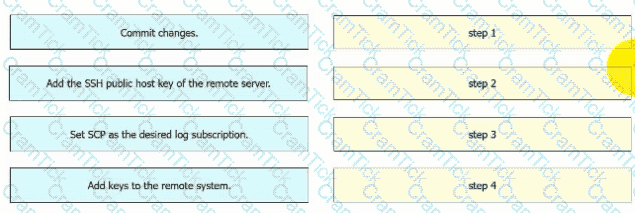
An engineer must configure AsyncOS for Cisco Secure Web Appliance to push log files to a syslog server using the SCP retrieval method. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
An engineer must modify a policy to block specific addresses using Cisco Umbrella. The policy is created already and is actively used by devices, using many of the default policy elements.
What else must be done to accomplish this task?
Which feature of Cisco ASA allows VPN users to be postured against Cisco ISE without requiring an inline
posture node?
An engineer needs to add protection for data in transit and have headers in the email message Which configuration is needed to accomplish this goal?
An engineer is deploying a Cisco Secure Email Gateway and must configure a sender group that decides which mail policy will process the mail. The configuration must accept incoming mails and relay the outgoing mails from the internal server. Which component must be configured to accept the connection to the listener and meet these requirements on a Cisco Secure Email Gateway?
Refer to the exhibit.
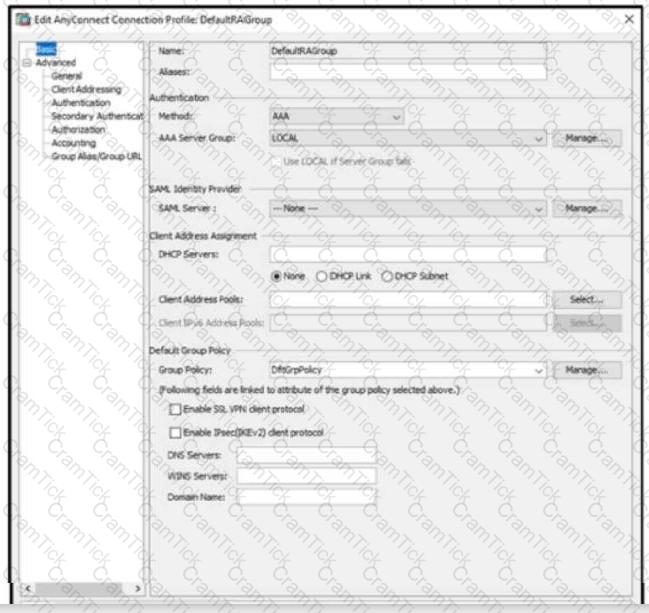
When configuring a remote access VPN solution terminating on the Cisco ASA, an administrator would like to utilize an external token authentication mechanism in conjunction with AAA authentication using machine
certificates. Which configuration item must be modified to allow this?
With which components does a southbound API within a software-defined network architecture communicate?
Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize
applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?
An administrator configures new authorization policies within Cisco ISE and has difficulty profiling the devices. Attributes for the new Cisco IP phones that are profiled based on the RADIUS authentication are seen however the attributes for CDP or DHCP are not. What should the administrator do to address this issue?
What is the result of the ACME-Router(config)#login block-for 100 attempts 4 within 60 command on a Cisco IOS router?
Which firewall mode does a Cisco Adaptive Security Appliance use to inspect Layer 2 traffic?
A security engineer must protect endpoints when a file appears harmless during initial inspection but later shows malicious behavior. The solution must continuously observe process and file activity after execution and respond when a threat emerges. The infrastructure includes Cisco Secure Endpoint. Which feature must the engineer configure to meet the requirements?
An engineer is configuring Cisco Secure Endpoint to enhance security by preventing the execution of certain files by users. The engineer needs to ensure that the specific executable file name Cisco_Software_0505446151.exe is blocked from running while never being quarantined. What must the engineer configure to meet the requirement?
A network engineer must create an access control list on a Cisco Adaptive Security Appliance firewall. The access control list must permit HTTP traffic to the internet from the organization ' s inside network 192.168.1.0/24. Which IOS command must oe used to create the access control list?
Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the
deployment?
Based on the NIST 800-145 guide, which cloud architecture may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises?
An engineer must force an endpoint to re-authenticate an already authenticated session without disrupting the
endpoint to apply a new or updated policy from ISE. Which CoA type achieves this goal?
Which two protocols must be configured to authenticate end users to the Web Security Appliance? (Choose two.)
How does a Cisco Secure Firewall help to lower the risk of exfiltration techniques that steal customer data?
Which exfiltration method does an attacker use to hide and encode data inside DNS requests and queries?
What is a functional difference between Cisco AMP for Endpoints and Cisco Umbrella Roaming Client?
Which information is required when adding a device to Firepower Management Center?
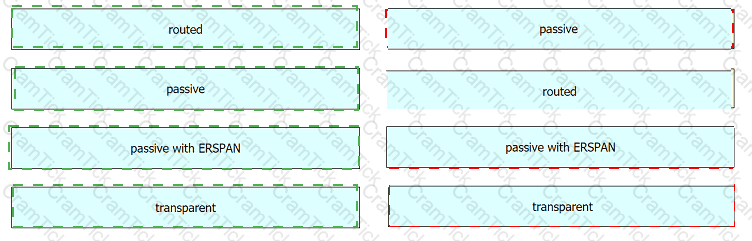
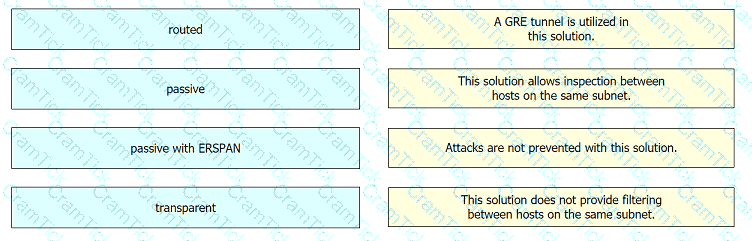
Drag and drop the deployment models from the left onto the explanations on the right.
Refer to the exhibit.
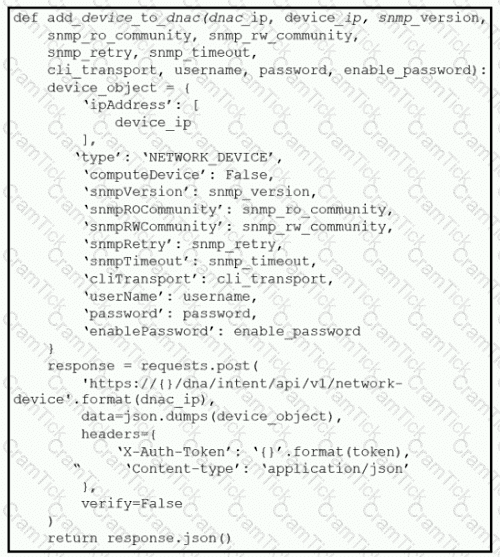
What is the result of this Python script of the Cisco DNA Center API?
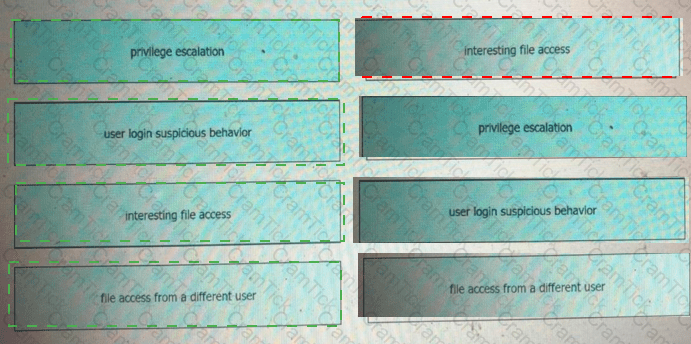
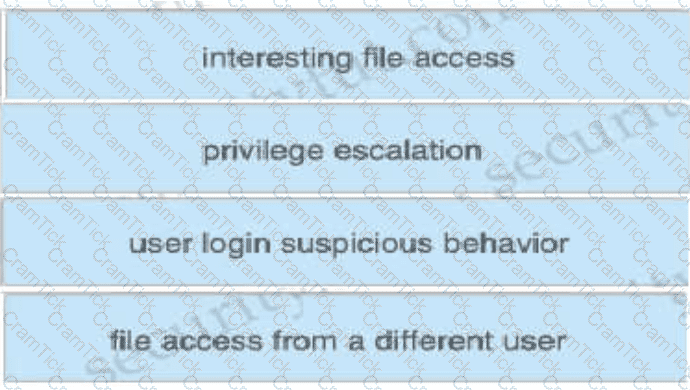
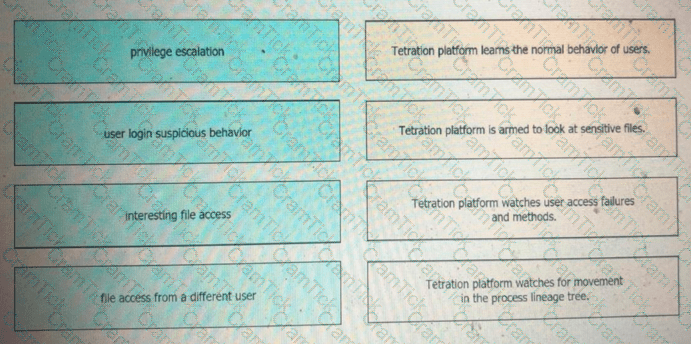
Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
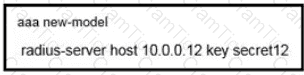
Refer to the exhibit. What is the result of using this authentication protocol in the configuration?
Which statement about the configuration of Cisco ASA NetFlow v9 Secure Event Logging is true?
Which flaw does an attacker leverage when exploiting SQL injection vulnerabilities?
When Cisco and other industry organizations publish and inform users of known security findings and
vulnerabilities, which name is used?
Which threat involves software being used to gain unauthorized access to a computer system?
The main function of northbound APIs in the SDN architecture is to enable communication between which two areas of a network?
Which Cisco platform onboards the endpoint and can issue a CA signed certificate while also automatically configuring endpoint network settings to use the signed endpoint certificate, allowing the endpoint to gain network access?
A recent change left network engineers unable to SSH into a branch Cisco Catalyst switch. The engineer confirms that the TACACS server group TACACS-GROUP is defined but unreachable. There is no fallback to the local database when TACACS+ is unavailable. Security policy requires TACACS+ as the primary authentication method with automatic fallback to local accounts. Which configuration command must be added to resolve the issue?
Which open standard underpins OpenID Connect, enabling Cisco Duo to authorize application access?
An engineer is deploying Cisco Advanced Malware Protection (AMP) for Endpoints and wants to create a policy that prevents users from executing file named abc424952615.exe without quarantining that file What type of Outbreak Control list must the SHA.-256 hash value for the file be added to in order to accomplish this?
An engineer must deploy Cisco Secure Email with Cloud URL Analysis and must meet these requirements:
To protect the network from large-scale virus outbreaks
To protect the network from non-viral attacks such as phishing scams and malware distribution
To provide active analysis of the structure of the URL and information about the domain and page contents
Which two prerequisites must the engineer ensure are configured? (Choose two.)
Refer to the exhibit.
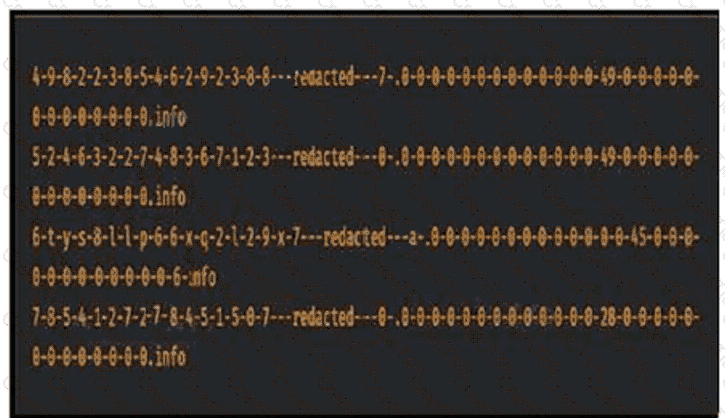
Consider that any feature of DNS requests, such as the length off the domain name
and the number of subdomains, can be used to construct models of expected behavior to which
observed values can be compared. Which type of malicious attack are these values associated with?
Which Cisco security solution determines if an endpoint has the latest OS updates and patches installed on the system?
How many interfaces per bridge group does an ASA bridge group deployment support?
A university policy must allow open access to resources on the Internet for research, but internal workstations are exposed to malware. Which Cisco AMP feature allows the engineering team to determine whether a file is installed on a selected few workstations?
What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)
Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?
An engineer needs behavioral analysis to detect malicious activity on the hosts, and is configuring the
organization’s public cloud to send telemetry using the cloud provider’s mechanisms to a security device. Which
mechanism should the engineer configure to accomplish this goal?
An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)
CCNP Security | 350-701 Written Exam | 350-701 Questions Answers | 350-701 Test Prep | 350-701 CCNP Security Actual Questions | Implementing and Operating Cisco Security Core Technologies (SCOR) Exam Questions PDF | 350-701 Online Exam | 350-701 Practice Test | 350-701 PDF | 350-701 CCNP Security Dumps | 350-701 Test Questions | 350-701 Study Material | 350-701 Exam Preparation | 350-701 Valid Dumps | 350-701 Real Questions | 350-701 CCNP Security Practice Test | CCNP Security 350-701 Dumps | Implementing and Operating Cisco Security Core Technologies (SCOR) Exam Questions
TESTED 05 Oct 2026